Launch your business into the cloud with vorza360’s expert cloud server deployment services. We build and manage powerful setups on AWS, Azure, and GCP to keep your apps fast and reliable.
The Challenge Hugo was running his online store on a single physical server that would frequently crash during holiday sales. Every time his traffic spiked, the website would go offline, costing him thousands in lost orders. He knew he needed to move to a more reliable setup but was overwhelmed by the technical complexity of cloud server deployment and feared the high monthly costs of getting it wrong.
The vorza360 Solution We stepped in to migrate his entire shop to a high-speed AWS cloud server development environment. We built a digital blueprint of his store using infrastructure as code, which allowed us to test every part of the move before it went live. To keep his costs low, we set up smart scaling rules that automatically add more power during busy sales and shrink back down when things are quiet.
The Result Hugo’s website handled his busiest Black Friday ever with zero downtime. He loves that his monthly bill stays small during slow weeks and only grows when he is actually making sales. He finally feels like he has a professional partner who handles the heavy lifting of cloud server deployment while he focuses on his customers in Sweden.
Elena Moretti (Italy)
The Challenge: Elena’s design firm in Milan was struggling with an old office server that made sharing large project files incredibly slow for her remote team. She wanted to move her office tools to a secure Windows Azure cloud server but was worried about losing data or having her team stuck in a long transition period. She needed a partner who could make the cloud feel simple and safe.
The vorza360 Solution We designed a tailored plan to move her creative suite and files into a managed Windows Azure cloud server environment. We focused on a smooth transition by building her new cloud office in the background while her team continued to work. Once everything was tested and ready, we flipped the switch, giving her team instant access to high-speed file sharing from anywhere in the world.
The Result: The frustration of slow loading bars is a thing of the past for Elena. Her team is now more productive than ever, and she appreciates the clear and easy words we used to explain the process. She values the ongoing support we provide to keep her Azure cloud server solutions running at peak performance.
Liam O’Sullivan (Ireland)
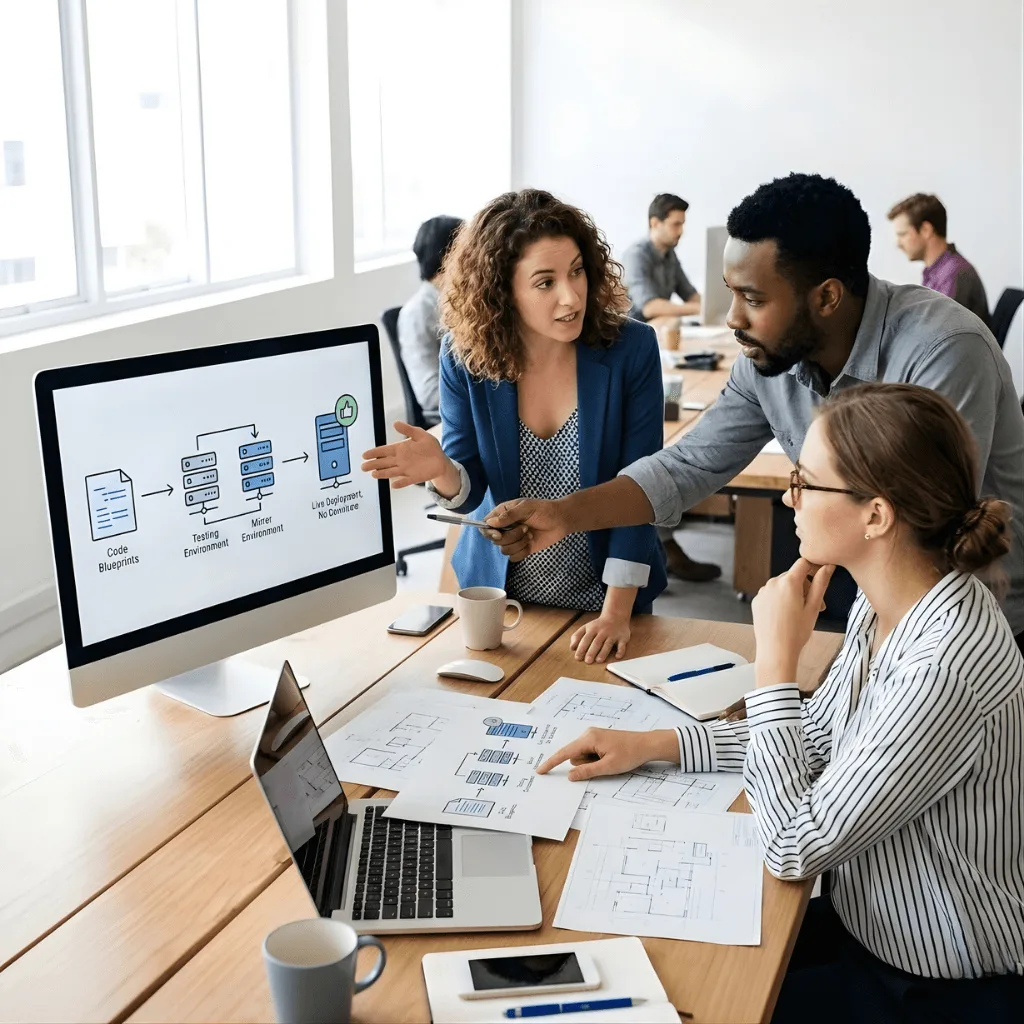
The Challenge Liam is a software developer in Dublin who was spending more time managing his servers than writing code. His local testing setup didn’t match his live environment, leading to constant bugs when he launched new features. He needed a professional development Azure cloud server that could mirror his live site perfectly without breaking his budget.
The vorza360 Solution We implemented an insightful strategy by setting up a dedicated development Azure cloud server that acts as a perfect twin to his production environment. We automated the entire deployment process, so now Liam can test his new code in a safe mirror world before it ever reaches a customer. This ensures that every update he launches is bug-free and professional.
The Result Liam has reclaimed hours of his time every week and can now launch new features with total confidence. He loves that vorza360 handles the server settings and security patches, acting as his internal tech team. His business in Ireland is growing faster because he can finally focus on his true passion of building great apps.
Sofia Rossi (Switzerland)
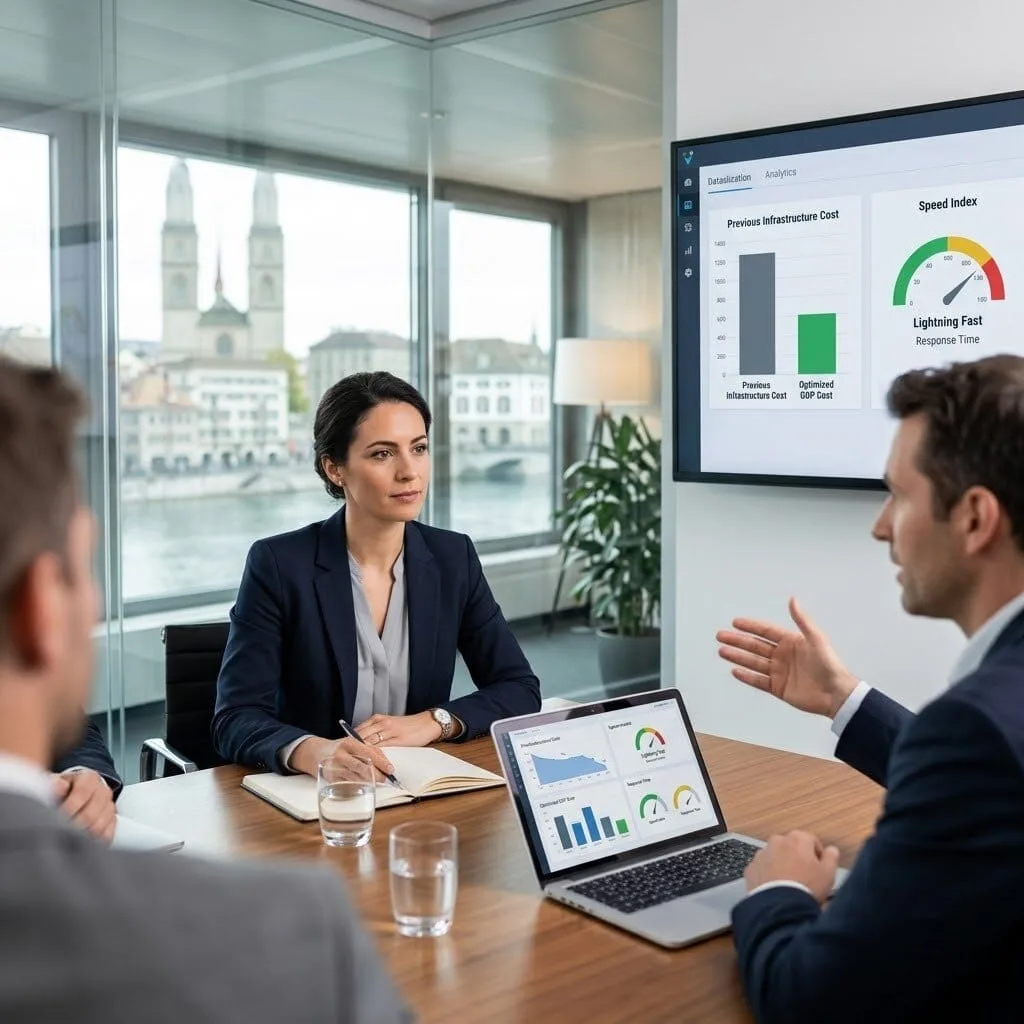
The Challenge Sofia runs a data-heavy analytics platform and was worried about the rising costs of her existing cloud setup. She felt like she was paying for massive amounts of power that she wasn’t actually using, but she was terrified that reducing her specs would cause her apps to lag for her global clients. She needed an expert to perform a deep-level cost optimization.
The vorza360 Solution We performed a full audit of her cloud server app development services and identified several areas where she was overpaying. We migrated her most demanding tasks to a GCP cloud server setup that uses more efficient storage and processing. By fine-tuning her resource limits, we ensured her platform stayed lightning-fast while slashing her monthly infrastructure bill.
The Result Sofia’s platform is now leaner and more profitable than ever. She saved over 30% on her monthly cloud costs without sacrificing a single second of speed for her users. She values the creative approach we took to find the perfect balance between high-end performance and budget-friendly management.
Mateo Santos (Spain)
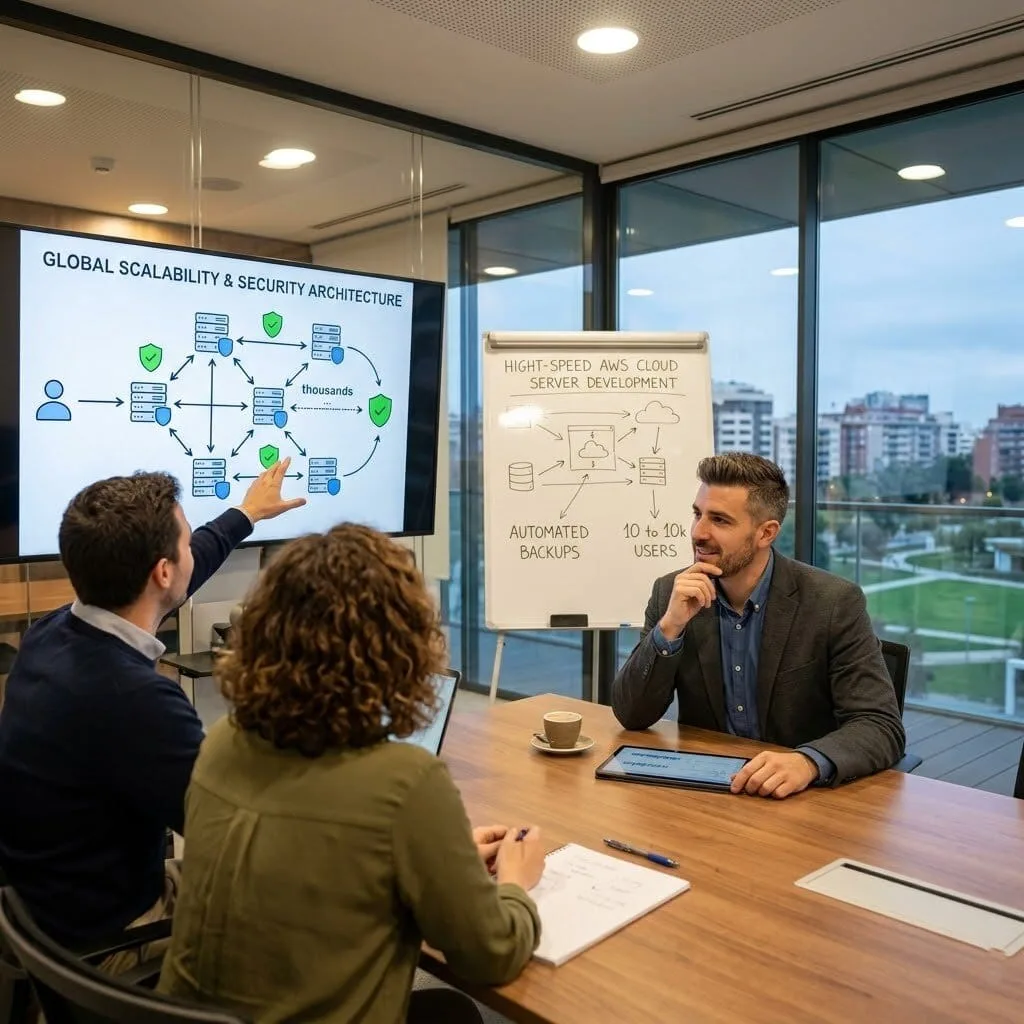
The Challenge Mateo wanted to launch a new mobile app but had no idea how to build a backend that could handle thousands of users across different countries. He was looking for a partner who could manage his AWS cloud server development from the ground up, ensuring his app would be “future-ready” and secure against potential cyber threats.
The vorza360 Solution We acted as Mateo’s expert guides, building a high-speed AWS cloud server development setup designed specifically for global reach. We used our Tech Edge to implement world-class security rules and automated backups, ensuring his users’ data is always protected. We built the foundation so strong that his app can now scale from ten users to ten thousand without him needing to change a single setting.
The Result Mateo’s app launch was a massive success, and he never had to worry about a server crash during the initial surge of downloads. He feels like he has a true partner in growth who speaks in easy words rather than technical jargon. His startup in Spain is now backed by the same technology used by the world’s biggest companies.
Clara Van den Berg (Netherlands)
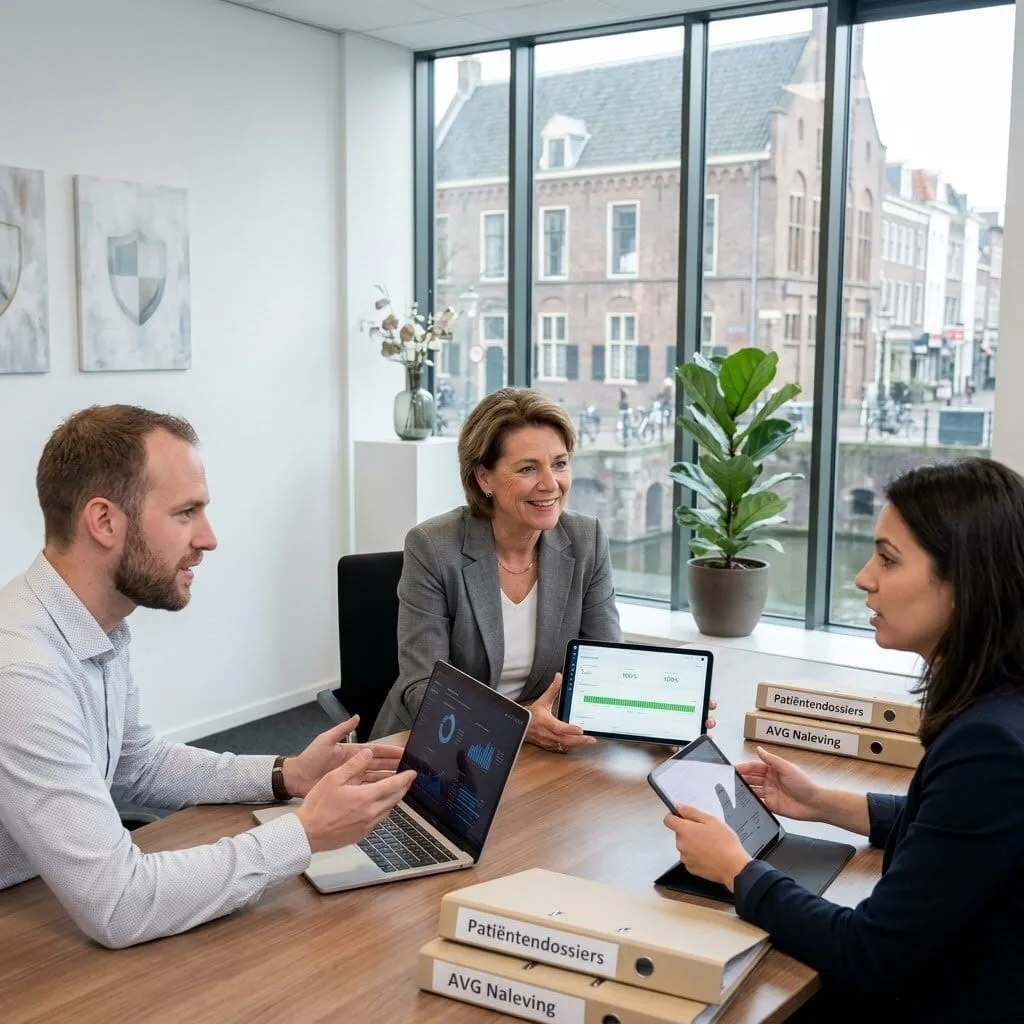
The Challenge: Clara manages a large network of medical clinics and needed a way to store patient records that was both highly secure and accessible 24/7. She was concerned about the strict privacy laws in Europe and needed a cloud server deployment that met the highest standards of safety while remaining simple for her staff to use every day.
The vorza360 Solution We built a custom-tailored cloud environment using secure Azure cloud server solutions. We implemented strict user permissions and encrypted storage to ensure that only authorized staff could view sensitive information. To guarantee 100% uptime, we set up a redundant system where a second GCP cloud server acts as a live backup, ready to take over instantly if any issues occur.
The Result Clara now has total peace of mind knowing her patient data is protected by a professional-grade shield. Her staff can access the files they need in the blink of an eye, and she hasn’t had a single security concern. She values the human-centered service we provide to her clinics in the Netherlands, making complex cloud technology feel safe and reliable.
Scaling Your Business with the Cloud
Moving your business to the cloud is like moving from a small office to a high-tech skyscraper. It gives you the space to grow, the speed to serve customers globally, and the safety of world-class security. At vorza360, we take the mystery out of the cloud by acting as your expert guides. We don’t just “set up” a server; we provide a complete service that ensures your Azure cloud server solutions or AWS instances are always healthy and ready for traffic.
Whether you are looking for AWS cloud server development to power a new app or need a stable Windows Azure cloud server for your office tools, we focus on making the transition smooth. Our team handles the complex settings and technical jargon, giving you a “ready-to-use” cloud environment. With vorza360, you get the full power of GCP cloud server and other top platforms with the personal care of a dedicated service partner.
How we do it
We provide hands-on service to turn complex cloud tools into simple business wins.
Creative Approaches
We use Infrastructure as Code to build digital blueprints of your servers. This allows us to test updates in a “mirror” environment before they go live, ensuring your cloud server deployment never faces unexpected downtime.
Insightful Strategies
Our focus is Cost-Optimization. We monitor your development Azure cloud server to ensure settings are “just right” fast enough for performance but efficient enough to save money by scaling with your traffic.
Tailored Solutions
We customize cloud server app development services for your platform of choice. Whether you need a high-speed AWS cloud server development setup or a secure Windows Azure cloud server, we pick the exact tools that fit your budget.
Creative Approaches
We use Infrastructure as Code to build digital blueprints of your servers. This allows us to test updates in a “mirror” environment before they go live, ensuring your cloud server deployment never faces unexpected downtime.
Insightful Strategies
Our focus is Cost-Optimization. We monitor your development Azure cloud server to ensure settings are “just right” fast enough for performance but efficient enough to save money by scaling with your traffic.
Tailored Solutions
We customize cloud server app development services for your platform of choice. Whether you need a high-speed AWS cloud server development setup or a secure Windows Azure cloud server, we pick the exact tools that fit your budget.
Here is what our Clients are saying About us
Mikael Virtanen (Finland)
vorza360 deployed our Ubuntu environment on AWS from scratch, VPC configuration, EC2 instances, security groups, and auto-scaling all set up correctly the first time. The ‘cloud-ready from day one’ infrastructure they built gave us a solid foundation to grow on.
Laila Al-Ahmadi (Kuwait)
We needed to migrate our on-premises Ubuntu servers to Azure and were worried about downtime and data loss. vorza360 handled the entire migration, lift-and-shift for some workloads, re-architecture for others, and we were fully operational in the cloud with less than two hours of total downtime.
Ananya Sharma (India)
vorza360 set up our Ubuntu-based infrastructure on GCP with proper networking, managed instance groups, and load balancing. They also configured CloudSQL to work alongside our Ubuntu application servers. The setup has scaled smoothly as our user numbers have grown.
Thibault Moreau (France)
Our team understood the applications but not the cloud infrastructure. vorza360 set up our Ubuntu servers on AWS, configured IAM roles correctly, and handed over a fully documented environment that our developers could actually work with. The ‘hand-it-over-properly’ approach they took was refreshing.
Chidinma Eze (Nigeria)
vorza360 deployed a multi-region Ubuntu setup on Azure for our business continuity requirements. They configured replication between regions, set up automated failover, and tested recovery thoroughly. We now have genuine geographic redundancy that actually works.
Elan Shapiro (Israel)
vorza360 built our entire cloud infrastructure on GCP using Ubuntu as the base for all our workloads. They optimised instance sizing, set up committed-use discounts correctly, and configured monitoring across the cloud environment. Our monthly cloud bill is 30% lower than our original estimate.
More about Ubuntu
Ubuntu Server Setup & Configuration
Get your business online quickly and securely with vorza360’s expert Ubuntu server setup…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What cloud deployment services does vorza360 provide for Ubuntu servers on AWS, Azure, and GCP?
vorza360 provides complete Ubuntu server deployment and management on all three major cloud platforms. On AWS, we deploy Ubuntu EC2 instances using official Canonical AMIs, configure instance types and storage (EBS volumes with appropriate type, gp3 for general purpose, io2 for database I/O performance), implement Security Groups for network access control, configure IAM instance profiles for application-level AWS API access without stored credentials, and integrate with AWS services (RDS, S3, Secrets Manager, CloudWatch). On Azure, we deploy Ubuntu VMs from Canonical Marketplace images, configure network security groups, managed disks, and Azure Monitor integration, and implement Managed Identities for secure Azure service access. On GCP, we deploy Ubuntu Compute Engine instances, configure firewall rules, managed persistent disks, and Cloud Monitoring integration. Across all platforms, we implement Infrastructure as Code using Terraform for repeatable, version-controlled deployments and configure cloud-native backup and monitoring integration.
How does vorza360 deploy Ubuntu servers on AWS with security and cost best practices?
AWS Ubuntu server deployments require cloud-specific security and cost management practices beyond the general Ubuntu hardening applied to all servers. vorza360 deploys Ubuntu servers on AWS following Well-Architected Framework principles: security-wise, we deploy instances in private subnets (with no public IP addresses) behind an Application Load Balancer or NAT Gateway, configure Security Groups with the principle of least access (only the specific ports from specific source Security Group IDs or CIDR ranges required for legitimate traffic), implement IAM instance profiles with minimum necessary permissions for any AWS API calls the application requires (avoiding long-term access keys stored on the instance), enable AWS Systems Manager Session Manager for administrative access without opening SSH port 22, enable AWS Inspector for automated vulnerability scanning, and configure GuardDuty for threat detection. For cost management, we recommend EC2 Reserved Instances or Savings Plans for consistent 24/7 workloads, configure instance autoscaling for variable workloads, and implement CloudWatch alarms and AWS Cost Anomaly Detection to alert on unexpected spend increases.
How does vorza360 configure Ubuntu servers on Azure with enterprise-grade management?
Ubuntu VMs on Azure can be managed through Azure’s native management plane, providing capabilities that significantly simplify operations at scale compared to managing on-premises Ubuntu servers. vorza360 configures Ubuntu on Azure with enterprise management features: we deploy VMs using Azure Resource Manager templates or Terraform for consistent, auditable provisioning, join VMs to Azure Active Directory for centralized identity and SSH authentication using AAD credentials, deploy the Azure Monitor Agent for centralized log collection and metric monitoring through Azure Monitor and Log Analytics, configure Azure Defender for Servers for continuous vulnerability assessment and threat detection, implement Azure Policy to enforce compliance baselines across all Ubuntu VMs (requiring disk encryption, requiring security updates, requiring specific configurations), configure Azure Backup for VM-level backup to Recovery Services Vault with appropriate retention policies, and use Azure Automation State Configuration (DSC) or Ansible to enforce and verify configuration compliance across the Ubuntu VM estate.
How does vorza360 implement auto-scaling for Ubuntu application servers in the cloud?
Auto-scaling allows cloud-deployed Ubuntu application servers to automatically add instances when traffic increases and remove them when traffic decreases, providing both cost efficiency (not paying for capacity during quiet periods) and performance resilience (not degrading during traffic spikes). vorza360 implements Ubuntu auto-scaling by building a custom AMI or Azure VM image (or Docker container image for container-based deployments) that contains a pre-configured, deployment-ready Ubuntu server application environment that can start serving traffic within minutes of provisioning without manual configuration. We configure the auto-scaling group (AWS ASG, Azure VMSS) with scaling policies based on CPU utilization, request count, or custom application metrics, defining scale-out thresholds (add instances when CPU exceeds 70 percent for 5 minutes) and scale-in thresholds (remove instances when CPU falls below 30 percent for 10 minutes). We implement instance warm-up periods preventing premature traffic routing to instances still initializing. We configure launch templates with all instance settings (instance type, security groups, IAM profile, user data bootstrap script) and test the scaling behaviour under simulated load before enabling auto-scaling in production.
How does vorza360 use Infrastructure as Code to manage Ubuntu cloud server deployments?
Infrastructure as Code (IaC) manages cloud Ubuntu server deployments as version-controlled code rather than manually configured resources, enabling repeatable deployments, auditable change history, and rapid disaster recovery from the code repository. vorza360 implements IaC for Ubuntu cloud deployments primarily using Terraform: we write Terraform configurations that define all cloud resources required for the Ubuntu server deployment, compute instances, storage volumes, networking (VPC, subnets, security groups), load balancers, DNS records, monitoring configuration, and backup policies. Terraform’s declarative approach means the configuration describes the desired end state, and Terraform calculates the changes needed to reach that state from the current infrastructure. We store all Terraform configurations in Git repositories with pull request-based review processes, ensuring every infrastructure change is reviewed before application. We implement Terraform workspaces or separate state files for each environment (development, staging, production), preventing accidental cross-environment changes. We combine Terraform for infrastructure provisioning with Ansible for Ubuntu OS-level configuration management, covering both the cloud resource layer and the operating system configuration layer with code.