
SSH & User Management
Secure your servers and control access with vorza360’s professional SSH and User Management services. We replace risky passwords with rock-solid security keys to keep your business data in the right hands.

Shopify

WordPress

Figma

PHP

Flutter

React Js

Node Js

Python

Swift

Java

Vue.js

Kotlin

CSS

HTML
JavaScript
Customer Success Story
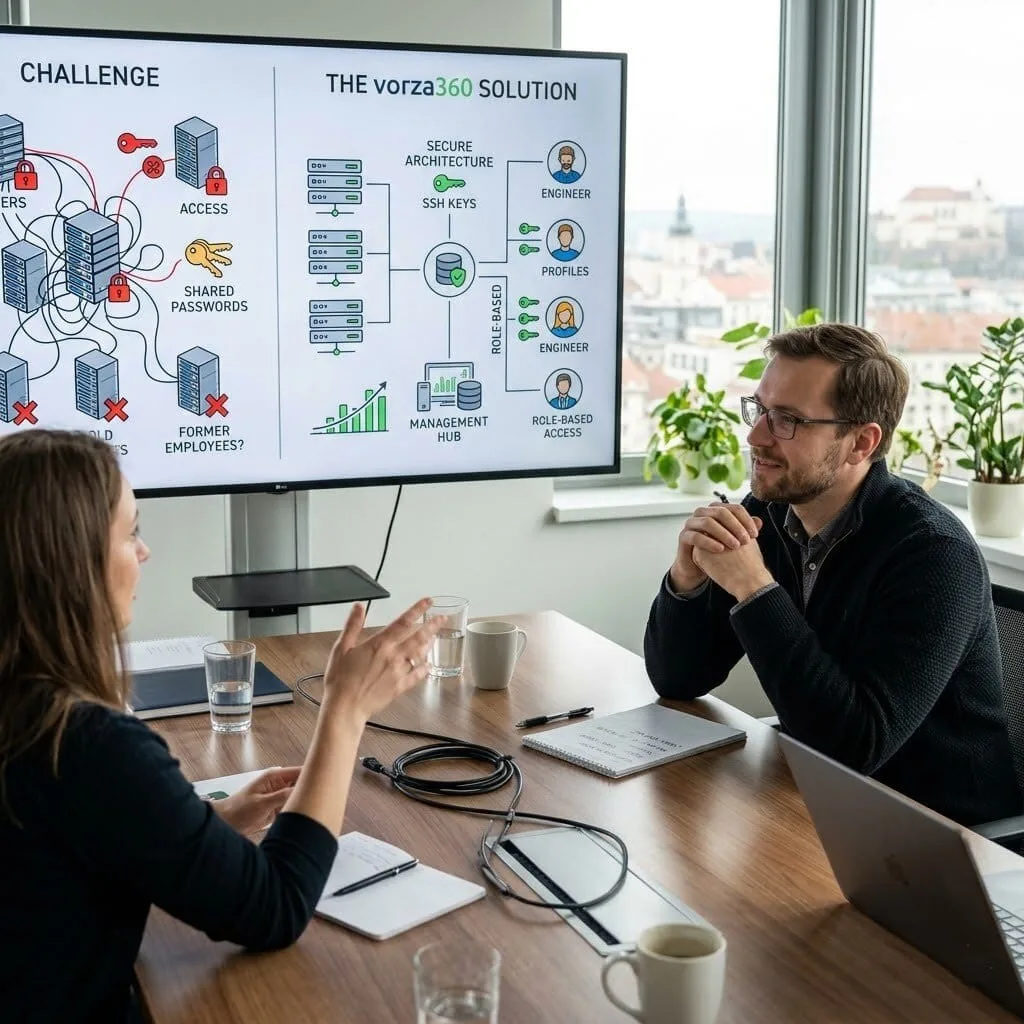
Tomas Novák (Czech Republic)
The Challenge: Tomas’s company had grown from a two-person startup to a team of fifteen engineers, but their server access management had never scaled with the team. There were shared root passwords on several servers, former employees still had active accounts on some systems, and nobody had a clear picture of who had access to what.
The vorza360 Solution: vorza360 conducted a full access audit, removed all stale accounts, replaced shared passwords with individual user accounts and SSH key authentication, implemented sudo policies giving each engineer access appropriate to their role, and set up centralised SSH key management so that adding or removing access could be done in one place.
The Result: Tomas finally had a clear, auditable picture of who could access which systems. When an engineer left the company the following month, revoking their access took minutes rather than the manual trawl across every server it had previously required.
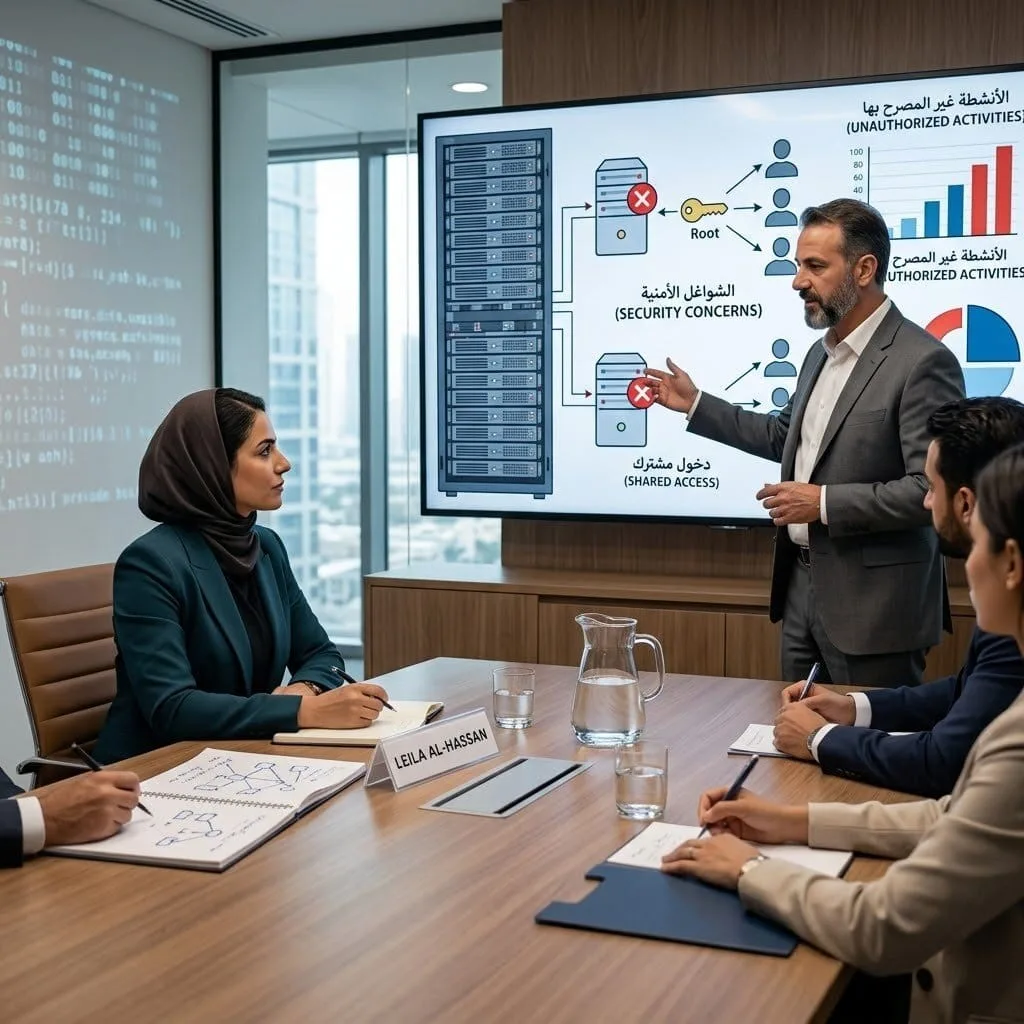
Leila Al-Hassan (Jordan)
The Challenge: Leila’s IT team managed over twenty Ubuntu servers for a government agency, and their SSH access management had become a serious compliance problem. Multiple people shared the same service accounts, root login was permitted from the internet, and there was no log of who had done what on which server.
The vorza360 Solution: vorza360 implemented individual user accounts across the entire fleet, disabled root SSH login, enforced SSH key authentication with a centralised key distribution mechanism, configured sudo with command-level logging, and integrated the servers with their existing syslog infrastructure to centralise audit trails.
The Result: The access audit that had been flagged as a critical compliance finding was resolved. Government auditors reviewing the system found clearly attributable access records and properly segregated permissions, a substantial improvement over the shared-account environment they had been running.
Cosmin Ionescu (Romania)
The Challenge: Cosmin’s software company had their source code repositories and deployment servers accessible via SSH, but after a developer left on poor terms, they realised they had no process for reliably revoking access across all systems. The audit took two days and they still weren’t certain they’d found everything.
The vorza360 Solution: vorza360 implemented LDAP-based centralised user management for their Ubuntu server fleet. User accounts, SSH keys, and sudo policies were all managed from a single directory, provisioning or deprovisioning a user meant one change that propagated to every server automatically.
The Result: The next time a team member departed, access was fully revoked across every server in under five minutes. Cosmin’s security team had the real-time visibility and control over server access they had needed, and onboarding new engineers became significantly simpler.
Rohan Sharma (India)
The Challenge: Rohan’s company used a third-party vendor for ongoing server maintenance, but they had been given full root SSH access to every server with no restrictions, no logging, and no way to know what they had actually done during their maintenance sessions.
The vorza360 Solution: vorza360 restructured the vendor’s access with a dedicated user account with only the sudo permissions their maintenance tasks required, SSH access restricted from their known IP ranges only, and sudo command logging enabled so that every privileged action was recorded in the audit log.
The Result: Rohan’s team had full visibility into what the vendor was doing during their maintenance sessions for the first time. The vendor relationship actually improved because clear boundaries and documented actions removed the ambiguity that had previously made both sides uneasy.
Maja Lindberg (Denmark)
The Challenge: Maja’s startup had recently received seed funding and was preparing for their first enterprise client security review. The client’s questionnaire asked about SSH access controls and user management practices, and the honest answer was that they had none. Everything ran as root, accessed with a shared password known to everyone on the team.
The vorza360 Solution: vorza360 implemented proper user management from scratch: individual accounts for every team member, SSH key-only authentication, root login disabled, and sudo configured so each person had the access their role required and nothing more. The setup was documented in a format suitable for security questionnaires.
The Result: Maja’s team completed the enterprise client security review with their server access controls scored as acceptable. The shared root password culture was gone, and the individual accountability that key-based authentication provided was something the whole team agreed was overdue.
Kwabena Mensah (Ghana)
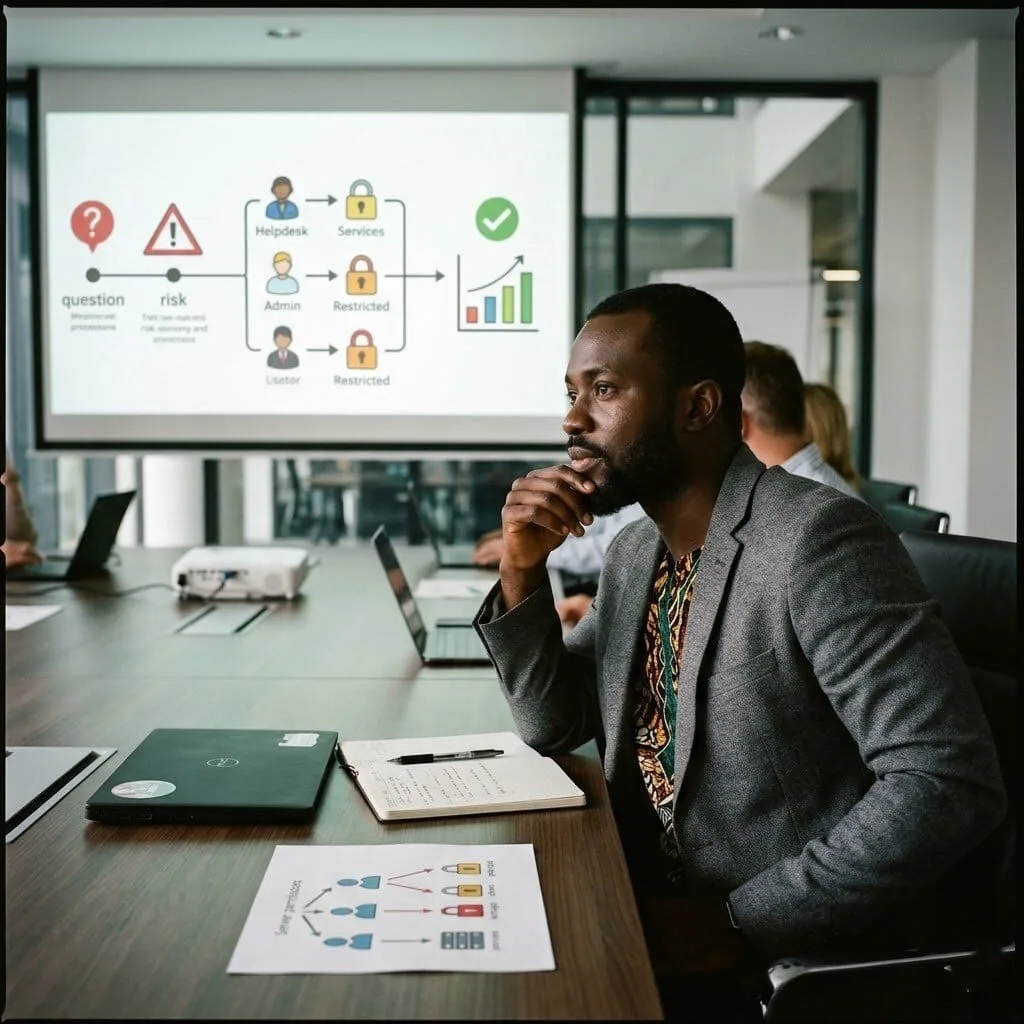
The Challenge: Kwabena’s organisation ran critical business applications on Ubuntu servers that were managed by a small IT team. The problem was that there was no clear policy for what each IT team member could do in practice, everyone could do everything, which made troubleshooting shared-responsibility problems difficult and created unnecessary risk.
The vorza360 Solution: vorza360 implemented role-based sudo policies for each IT team member: helpdesk staff could restart services but not modify configuration, system administrators could manage packages and configuration but required a second approval for destructive actions, and all privileged commands were logged to a tamper-resistant audit trail.
The Result: Accountability for changes improved immediately when something broke, the audit log showed exactly what had been done and by whom. The IT team found that clearer boundaries actually reduced friction rather than increasing it, and Kwabena had the oversight he needed.
vorza360’s Tech Edge
SSH Key-Based Authentication
Root Login Restriction
User Access Segmentation
+ 2
More
Session Timeout Policies
User Access Segmentation
vorza360’s Tech Edge
SSH Key-Based Authentication
Our team replaces simple passwords with unique digital keys, ensuring only your specific, approved devices can enter the server.
Root Login Restriction
We close the main “master” entrance to your system, requiring every user to log in with their own name so every action is recorded and safe.
User Access Segmentation
We divide your server into private sections, making sure employees only see the files and tools they need for their specific jobs.
Session Timeout Policies
We set up smart timers that automatically lock a connection if it’s left idle, protecting your data if a team member steps away from their desk.
Access Log Auditing
We maintain a clear, easy-to-read “visitor list” that shows exactly who accessed the server and when, giving you total oversight.
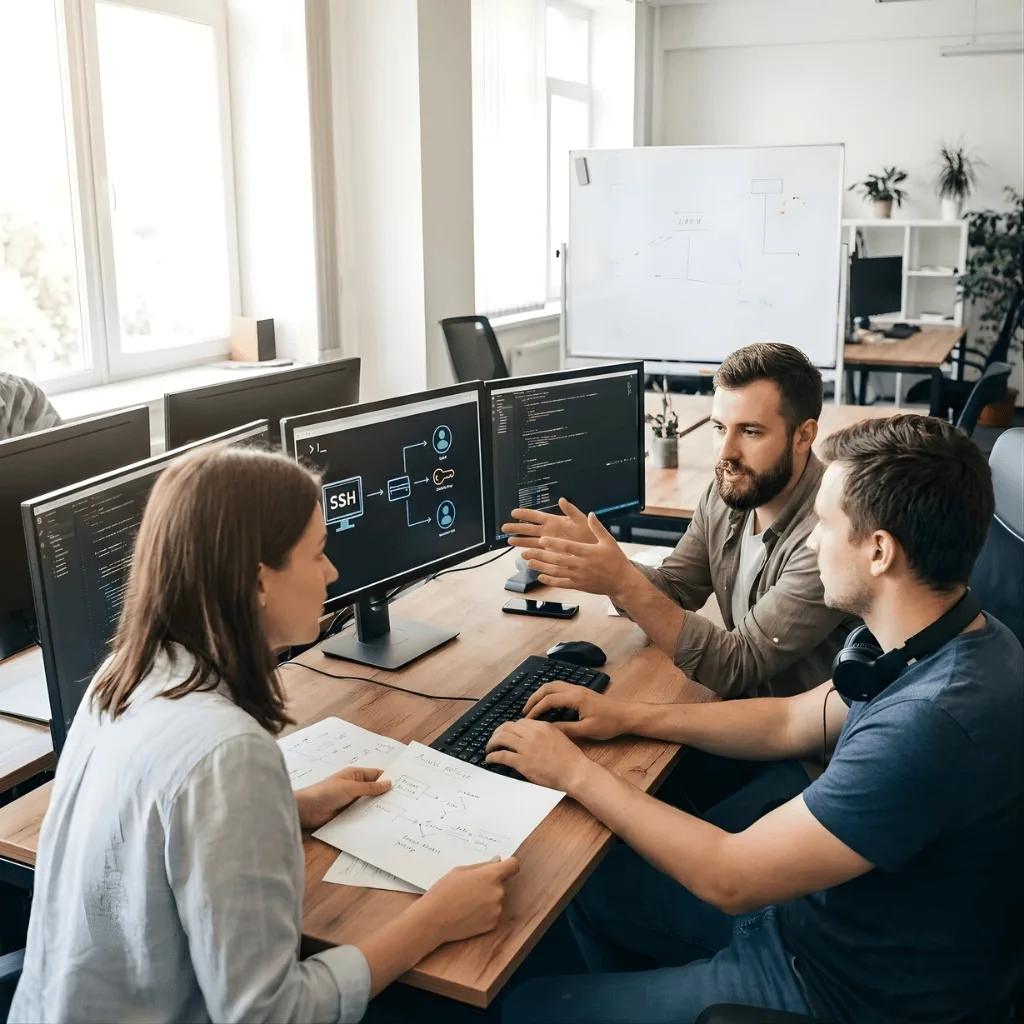
Professional Linux Manage SSH Users
We take the hassle out of server access by handling all the “behind-the-scenes” user settings for your team.
Advantages
- Creating unique accounts for every team member so no one has to share a password.
- Setting up custom permissions so staff can do their jobs without breaking system files.
- Managing a centralized SSH user management panel for quick updates.
- Removing old accounts immediately when an employee leaves the company.
- Ensuring every login follows your company's strict security rules.
Advanced SSH User Key Management
We move your business away from weak passwords and toward professional SSH user key management.
Advantages
- Generating ultra-secure 4096-bit digital keys for every authorized user.
- Helping your team set up and use their keys on Windows, Mac, or Linux.
- Linux servers manage user accounts SSH key storage to keep the system organized.
- Teaching your staff how to protect their private keys with a second password.
- Performing regular "key rotations" to keep your security fresh and updated.
AWS & Cloud User Management
Our experts help you manage user SSH keys AWS environments to keep your cloud servers protected.
Advantages
- Using AWS simple ad manage users Linux user accounts SSH to sync your office logins with the cloud.
- Providing professional AWS SSH user management for EC2 and other cloud instances.
- Configuring "Jump Hosts" so your team has one safe entrance to all your cloud tools.
- Managing cloud security groups to limit who can even try to connect.
- Integrating cloud-native tools for 24/7 monitoring of user activities.
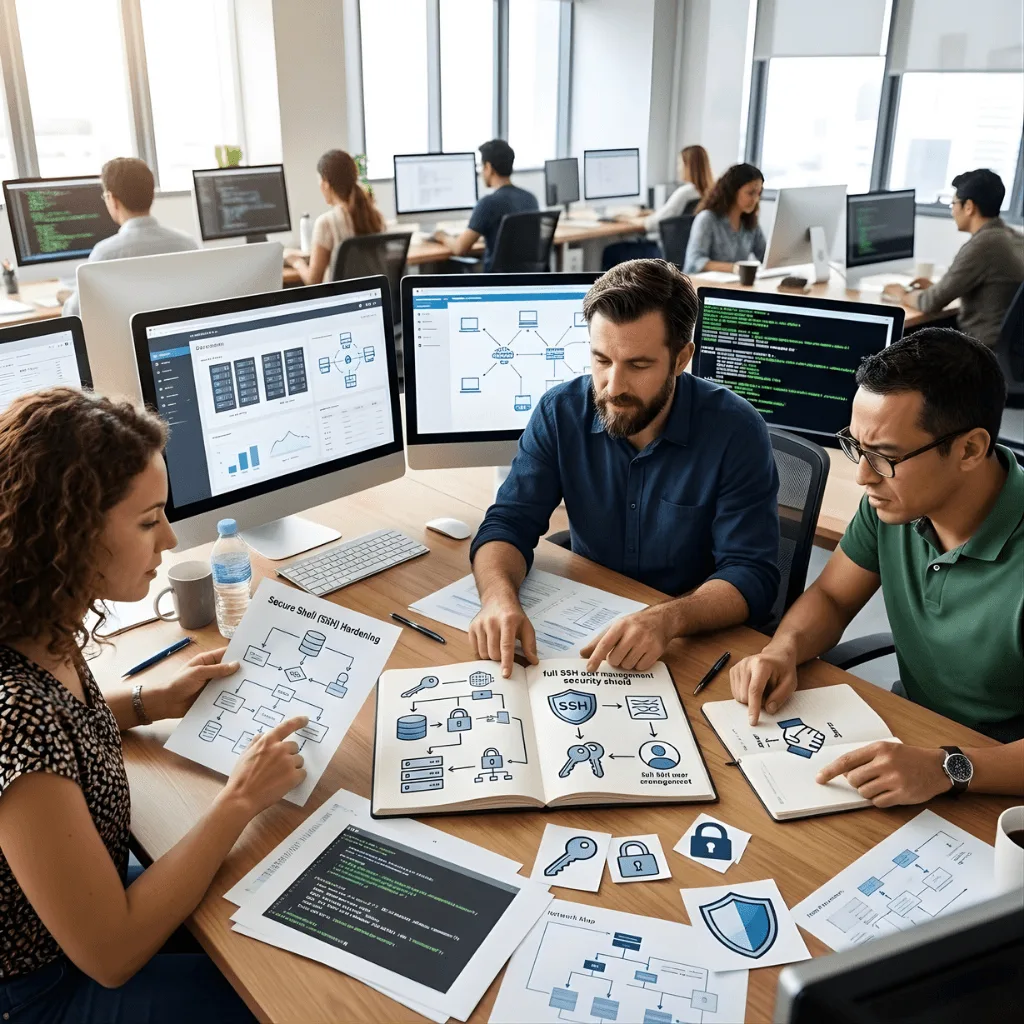
Secure Shell (SSH) Hardening
We go beyond simple logins to provide a full SSH user management security shield.
Advantages
- Changing the default "door number" (port) of your SSH to hide it from bots.
- Installing brute-force protection to block anyone who tries to guess a login.
- Disabling old, insecure connection methods that hackers like to use.
- Providing a human-led service that checks your security settings every day.
- Setting up "IP Whitelisting" so only your office can access the server.
User Activity Auditing & Support
Through our SSH & User Management services, we provide total visibility into your server’s health.
Advantages
- Reviewing logs to spot unusual login times or suspicious behavior.
- Providing a "searchable" history of every command typed by users.
- Troubleshooting connection issues for your team in plain English.
- Creating "read-only" accounts for auditors or guests who just need to see data.
- Offering a friendly, service-based partner to handle all your technical requests.
Professional Linux Manage SSH Users
We take the hassle out of server access by handling all the “behind-the-scenes” user settings for your team.
ADVANTAGES
- Creating unique accounts for every team member so no one has to share a password.
- Setting up custom permissions so staff can do their jobs without breaking system files.
- Managing a centralized SSH user management panel for quick updates.
- Removing old accounts immediately when an employee leaves the company.
- Ensuring every login follows your company's strict security rules.
Advanced SSH User Key Management
We move your business away from weak passwords and toward professional SSH user key management.
ADVANTAGES
- Generating ultra-secure 4096-bit digital keys for every authorized user.
- Helping your team set up and use their keys on Windows, Mac, or Linux.
- Linux servers manage user accounts SSH key storage to keep the system organized.
- Teaching your staff how to protect their private keys with a second password.
- Performing regular "key rotations" to keep your security fresh and updated.
AWS & Cloud User Management
Our experts help you manage user SSH keys AWS environments to keep your cloud servers protected.
ADVANTAGES
- Using AWS simple ad manage users Linux user accounts SSH to sync your office logins with the cloud.
- Providing professional AWS SSH user management for EC2 and other cloud instances.
- Configuring "Jump Hosts" so your team has one safe entrance to all your cloud tools.
- Managing cloud security groups to limit who can even try to connect.
- Integrating cloud-native tools for 24/7 monitoring of user activities.
Secure Shell (SSH) Hardening
We go beyond simple logins to provide a full SSH user management security shield.
ADVANTAGES
- Changing the default "door number" (port) of your SSH to hide it from bots.
- Installing brute-force protection to block anyone who tries to guess a login.
- Setting up "IP Whitelisting" so only your office can access the server.
- Disabling old, insecure connection methods that hackers like to use.
- Providing a human-led service that checks your security settings every day.
User Activity Auditing & Support
Through our SSH & User Management services, we provide total visibility into your server’s health.
ADVANTAGES
- Reviewing logs to spot unusual login times or suspicious behavior.
- Providing a "searchable" history of every command typed by users.
- Troubleshooting connection issues for your team in plain English.
- Creating "read-only" accounts for auditors or guests who just need to see data.
- Offering a friendly, service-based partner to handle all your technical requests.
Here is what our Clients are saying About us

Andris Kalniņš (Latvia)
Our SSH setup was wide open, password auth enabled, root login allowed, no rate limiting. vorza360 locked it down completely, set up key-based authentication for every user, and gave us a proper access policy. What was a glaring risk is now one of the tightest parts of our infrastructure.
Hira Baig (Pakistan)
We had accumulated dozens of old user accounts on our Ubuntu servers with no clear ownership or access policy. vorza360 came in, audited every account, removed the stale ones, and restructured our groups with proper permissions. The ‘clean-access’ model they implemented is now our standard.
Søren Madsen (Denmark)
vorza360 integrated our Ubuntu user management with our existing Active Directory environment. It required careful configuration across multiple systems but they handled it seamlessly. Our team now manages all access from one place rather than juggling separate systems.
Chiamaka Okonkwo (Nigeria)
Onboarding new developers was painfully slow because our user provisioning process was entirely manual. vorza360 built a streamlined SSH key management and user provisioning workflow that gets a new team member set up securely in minutes. The efficiency gain has been significant.
Matej Novák (Slovakia)
After a team member left under difficult circumstances, we needed to audit and tighten all SSH access quickly. vorza360 handled it methodically, key rotation, account removal, access review, and put a proper offboarding procedure in place so we’re never scrambling like that again.
Yasmine Khalil (Lebanon)
vorza360 set up sudo policies across our server fleet that gave our junior admins the access they needed to do their jobs without exposing production systems to unnecessary risk. The ‘right-access-right-role’ structure they implemented has made our team both more capable and more secure.
More about Ubuntu
Ubuntu Server Setup & Configuration
Get your business online quickly and securely with vorza360’s expert Ubuntu server setup…
Apache/Nginx Web Server Configuration
Launch your website with confidence using vorza360’s expert apache web server…
LAMP/LEMP Stack Deployment
Launch high-performance websites with vorza360’s expert LAMP and LEMP stack…
Firewall & Security Hardening
Protect your business from cyber threats with vorza360’s expert firewall hardening and…
Backup & Disaster Recovery
Secure your business future with vorza360’s professional backup and disaster recovery…
Database Installation & Optimization
Boost your website’s speed and reliability with vorza360’s expert database optimization…
+ 5
More
Virtualization & Containerization
Maximize your server’s potential with vorza360’s expert virtualization and containerization…
Performance Monitoring & Tuning
Keep your systems running at lightning speed with vorza360’s professional performance…
Package Management & Updates
Keep your systems modern and secure with vorza360’s professional package management…
More about Ubuntu
Ubuntu Server Setup & Configuration
Apache/Nginx Web Server Configuration
LAMP/LEMP Stack Deployment
+ 12
More
Firewall & Security Hardening
Backup & Disaster Recovery
Database Installation & Optimization
Virtualization & Containerization
Performance Monitoring & Tuning
Frequently Asked Questions
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
How does vorza360 manage SSH access to Ubuntu servers securely?
SSH is the primary administrative interface for Ubuntu servers and securing it correctly is one of the most consequential security decisions in the server’s lifecycle. vorza360 manages Ubuntu SSH security comprehensively: we configure key-based authentication as the exclusive authentication method, generating strong Ed25519 key pairs for each authorized administrator and deploying the public key to the server’s authorized_keys file. We harden the sshd_config with security-focused settings: PermitRootLogin prohibit-password (preventing direct root SSH even with a key), PasswordAuthentication no (disabling password login entirely), MaxAuthTries 3 (limiting authentication attempts per connection), LoginGraceTime 30 (limiting the window for authentication before disconnection), AllowUsers or AllowGroups directives restricting SSH access to specifically authorized accounts, and Protocol 2 (ensuring only the current SSH protocol version is accepted). We implement SSH certificates (using an internal SSH Certificate Authority) for environments where managing individual authorized_keys files across many servers is impractical, enabling centralized SSH access control with automatic expiry.
How does vorza360 manage Ubuntu user accounts and sudo privileges for teams?
Ubuntu user and group management for teams requires a systematic approach that enforces least privilege, maintains accountability, and scales without becoming administratively unwieldy. vorza360 manages Ubuntu user accounts by creating individual user accounts for each administrator, never sharing accounts, as shared accounts eliminate the ability to attribute actions to specific individuals in audit logs. We create a system administration group (typically named sysadmin or wheel) and configure sudoers to grant members of this group appropriate elevated privileges rather than granting sudo access to individual users. We use visudo with NOPASSWD directives sparingly and only for specific commands that genuinely require it, requiring password confirmation for general sudo use to prevent accidental or unintended elevated command execution. We configure password aging policies using chage for any remaining password-authenticated accounts. We maintain a user access register documenting every account, its purpose, and its authorized owner, conducting quarterly reviews to identify and remove accounts for team members who have left.
How does vorza360 set up SSH jump hosts for secure access to Ubuntu servers in private networks?
Servers in private networks, database servers, application servers, internal systems, should not be directly accessible via SSH from the internet. A jump host (also called a bastion host) is a hardened, minimally provisioned server with a public IP that serves as the single secure entry point through which administrators connect to reach servers in the private network. vorza360 configures SSH jump host infrastructure by deploying a dedicated jump host instance with a minimal Ubuntu Server installation (no additional services, no web server, no database), configuring it with strict firewall rules that permit only SSH inbound from authorized administrator IP addresses, enforcing SSH certificate or key authentication with MFA where available, enabling comprehensive SSH session logging (all commands typed during sessions logged for audit), and configuring ProxyJump (the SSH client directive that transparently routes connections through the jump host to private servers). We distribute SSH client configuration files (config files with ProxyJump directives) to all administrators so connecting to private servers via the jump host requires a single SSH command.
How does vorza360 implement centralized authentication for Ubuntu servers across a fleet?
Managing individual user accounts and SSH keys on each server independently does not scale when an organization has many Ubuntu servers, adding a new team member requires updating the authorized_keys on every server individually, and revoking access for a departing employee requires the same. vorza360 implements centralized authentication for Ubuntu server fleets using several approaches depending on the environment: for organizations with Active Directory or Azure Active Directory, we configure SSSD (System Security Services Daemon) on each Ubuntu server, joining it to the domain and allowing AD user accounts to log in to Ubuntu with their corporate credentials and MFA. For cloud environments or organizations without Active Directory, we implement SSH Certificate Authority authentication, a centralized CA signs certificates for authorized users, and servers trust the CA rather than individual keys, so adding or revoking a user’s access requires only issuing or revoking their certificate without touching any server’s authorized_keys file. We also implement Teleport or Boundary for privileged access management providing centralized session recording and just-in-time access provisioning.
How does vorza360 audit SSH access and user activity on Ubuntu servers?
Auditing who accessed an Ubuntu server, when, what commands were executed, and what changes were made is both a security requirement and an operational necessity for understanding incidents and demonstrating compliance. vorza360 implements Ubuntu SSH and user activity auditing through multiple mechanisms: we configure auditd with rules that capture all privileged command executions (via sudo), authentication events (successful and failed logins), changes to sensitive files (/etc/passwd, /etc/sudoers, cron tabs), and network connection events. We configure the system’s auth.log to be forwarded to a centralized log management system (ELK stack, Graylog, or a cloud-based SIEM) so logs are preserved even if the server is compromised or the local logs are tampered with. For environments requiring full session recording (every command typed during an SSH session), we implement Teleport’s session recording feature or configure a script-based session logging approach. We provide monthly SSH access reports showing login frequency, source IP addresses, and any failed authentication patterns that might indicate unauthorized access attempts.