Protect your business from cyber threats with vorza360’s expert firewall hardening and security services. We build multi-layered shields to keep your data safe and your servers running securely.
The Challenge: Klaus’s manufacturing company had received a penetration testing report that flagged their Ubuntu servers as having a significant attack surface, open ports that weren’t needed, default SSH configuration, no application firewall, and sysctl settings left at defaults. The auditors gave them 30 days to remediate.
The vorza360 Solution: vorza360 worked through the penetration testing findings systematically: implementing UFW firewall rules to close every unnecessary port, hardening SSH configuration, applying sysctl network and kernel hardening settings, installing and configuring fail2ban, and enabling automatic security updates for OS packages.
The Result: The follow-up penetration test found no remaining open findings from the original report. Klaus’s IT security team received full documentation of every change made and the rationale behind it, giving them a defensible security baseline to maintain and build on.
Sara Al-Zahrani (Saudi Arabia)
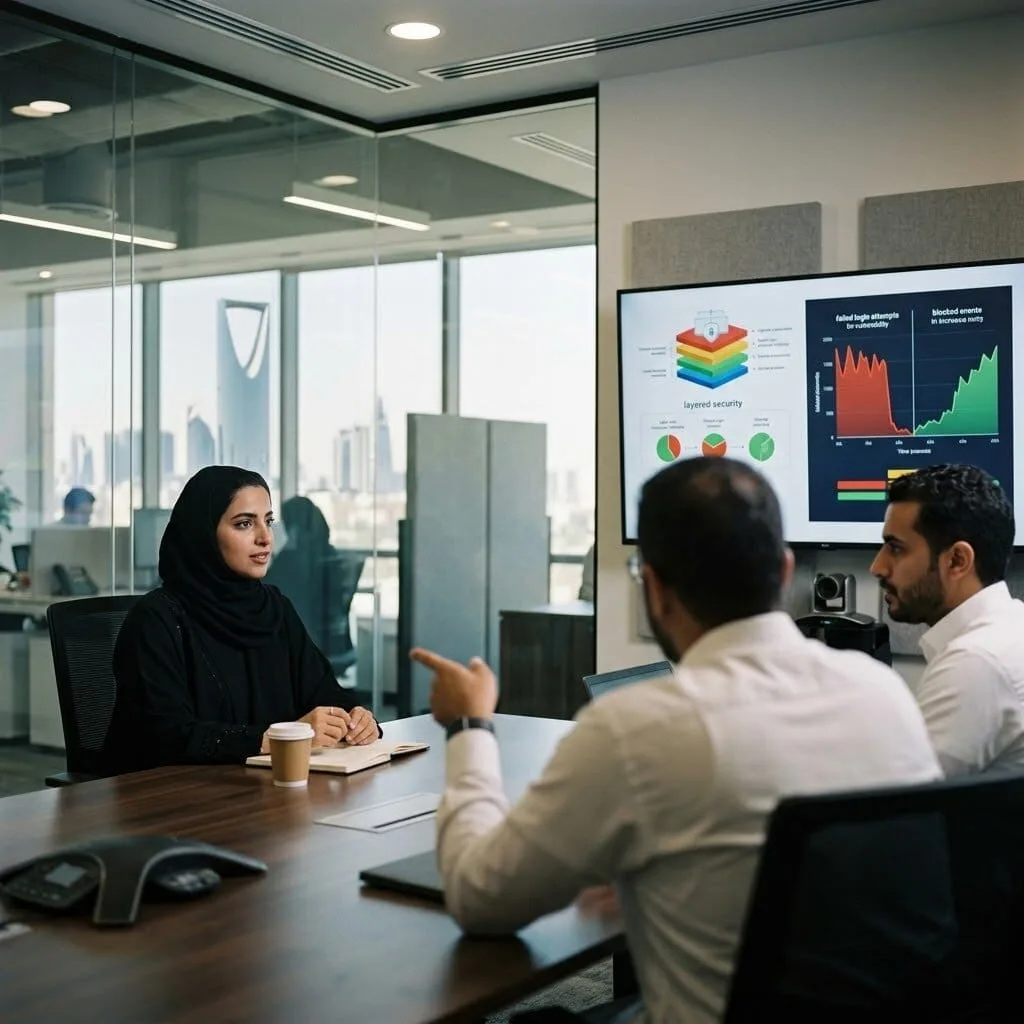
The Challenge: Sara’s fintech startup had been operating with minimal server hardening, their Ubuntu servers were accessible over SSH with password authentication, no firewall was configured, and they had no idea how many failed login attempts they were receiving until they checked the logs for the first time.
The vorza360 Solution: vorza360 implemented a layered security approach: UFW firewall with allow-listing for necessary services only, SSH hardened to key-based authentication with root login disabled, fail2ban configured to block brute-force attempts, and auditd configured to log privileged commands for their compliance requirements.
The Result: The logs immediately showed fail2ban blocking hundreds of automated brute-force attempts that had previously gone unnoticed. Sara’s team had the security posture their banking partners were asking about, documented and demonstrable, within one week of engagement.
Radu Constantin (Romania)
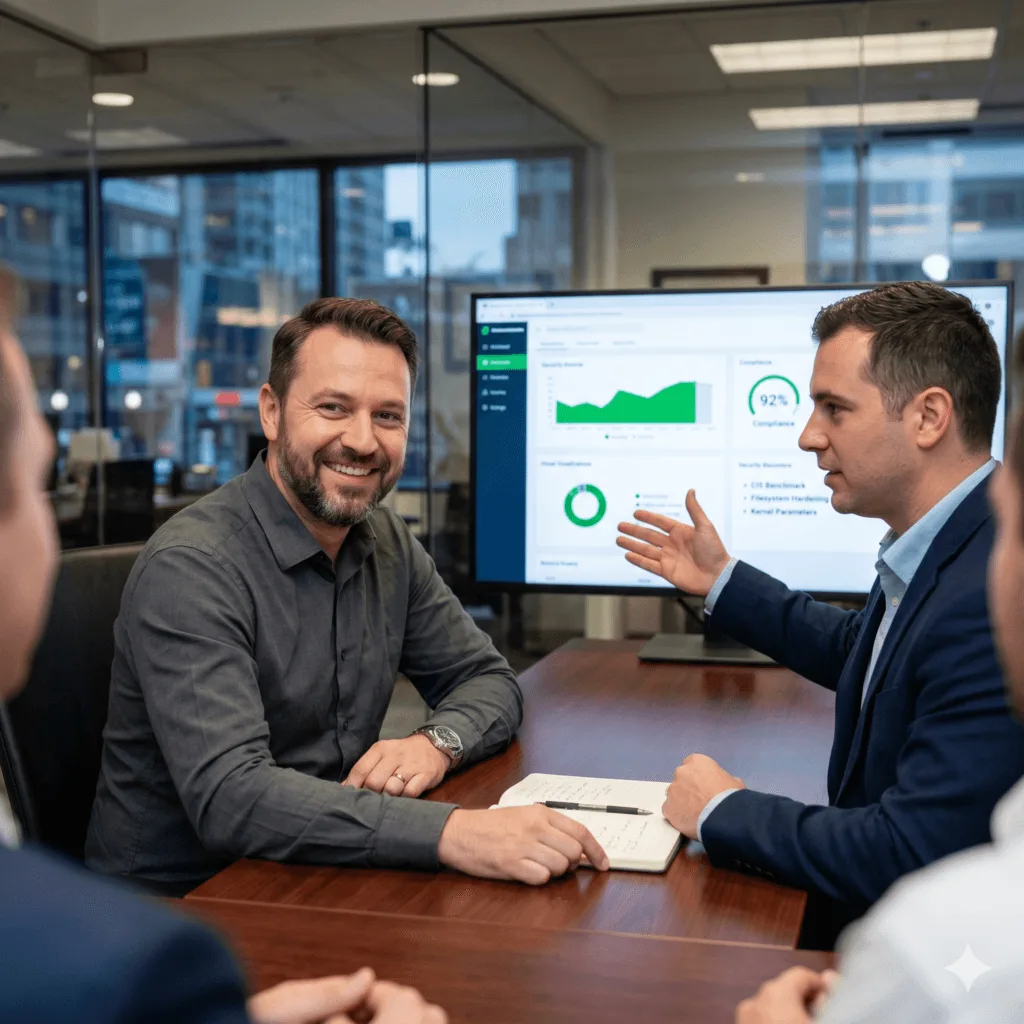
The Challenge: Radu’s company had experienced a security incident where an attacker had gained access to one of their Ubuntu servers through an unpatched vulnerability. The compromised server had been rebuilt, but the rest of the fleet had never been hardened, they were still running the same default configurations.
The vorza360 Solution: vorza360 conducted a security assessment of the entire Ubuntu fleet and applied CIS Benchmark Level 1 hardening across all servers: filesystem hardening, kernel parameter settings, service minimisation, PAM configuration, and SSH hardening. They also implemented centralised security log collection.
The Result: The post-hardening security scan showed the fleet now met the CIS Benchmark at over 90% compliance. More importantly, Radu’s team understood what had been applied and why, meaning they could maintain the security standard as the environment evolved rather than relying on vorza360 indefinitely
Priya Menon (India)
The Challenge: Priya’s company was preparing for an ISO 27001 audit and their server security controls were one of the identified gaps. Their Ubuntu servers had been running for years with no formal security hardening, and their IT team had two months to get the environment to an auditable standard.
The vorza360 Solution: vorza360 aligned the hardening work to the ISO 27001 controls their auditor was examining: implementing firewall rules, SSH hardening, privilege separation for administrative access, automatic security patching for critical vulnerabilities, and file integrity monitoring on sensitive system files.
The Result: The ISO 27001 audit passed the server security controls section without any findings. Priya’s team received an evidence pack documenting every control implemented, exactly the format her auditor needed. The hardening work that had seemed overwhelming two months earlier was completed on time.
Erik Svensson (Sweden)
The Challenge: Erik’s company had a geographically distributed team of administrators who needed SSH access to Ubuntu servers from multiple locations. Security was becoming increasingly important, but tightening access was creating friction for their engineers who were used to connecting from wherever they happened to be working.
The vorza360 Solution: vorza360 implemented a bastion host architecture with SSH certificate-based authentication managed through a central certificate authority. Engineers authenticate once through the bastion with their certificate, accessing internal servers without exposing them directly to the internet. All access was logged centrally.
The Result: Security improved significantly while friction for engineers actually reduced, one authentication mechanism replaced the per-server key management that had previously been a headache. The central access log gave management visibility into who accessed which server and when, something they had never had before.
Amara Diallo (Senegal)
The Challenge: Amara’s media organisation had recently had a server probed by automated scanners, and whilst no breach had occurred, the incident made it clear that their Ubuntu servers were more exposed than they had realised. They wanted basic hardening applied without disrupting their small team’s ability to manage the servers.
The vorza360 Solution: vorza360 applied practical security hardening focused on the highest-impact improvements: UFW firewall restricting inbound access to only necessary services, SSH key-only authentication, fail2ban to block automated attacks, and automatic security updates for the OS. Every change was tested before being applied to production.
The Result: The automated scanner that had previously found open ports and default SSH configuration found nothing of concern in a follow-up scan. Amara’s team experienced no disruption to their work; the hardening had been applied carefully, with their workflows considered throughout.
vorza360’s Tech Edge
UFW Firewall Rule Design
Port Exposure Minimization
Brute-Force Protection Setup
+ 2
More
Kernel Security Parameters
Security Compliance Baselines
vorza360’s Tech Edge
UFW Firewall Rule Design
We use the “Uncomplicated Firewall” to create precise rules that allow your team in while keeping everyone else out.
Port Exposure Minimization
Our team closes every unnecessary “digital door” on your server, leaving only the essential paths open for your work.
Brute-Force Protection Setup
We install smart tools like Fail2Ban that act as security guards, blocking anyone who tries to guess your passwords.
Kernel Security Parameters
We tune the very “brain” of your Linux system to resist advanced attacks and improve overall stability.
Security Compliance Baselines
We set up your systems to follow firewall hardening standards, ensuring you meet the safety requirements for your industry.
How we do it
At vorza360, we treat cyber security hardening as a continuous service, not a one-time task.
Creative Approaches
We go beyond a simple firewall hardening guide by using creative “stealth” methods. This includes moving important services to non-standard ports and using “port knocking,” where a door only opens if you know the secret digital handshake. This makes your server nearly invisible to automated hackers.
Insightful Strategies
Our strategy involves “thinking like a defender.” We use security hardening strategies that assume a breach could happen, so we build internal walls (segmentation) to stop a threat from moving. We don’t just follow a firewall hardening checklist; we build a strategy that protects your most valuable data first.
Tailored Solutions
Whether you are hardening Windows firewalls for an office team or need deep Linux security hardening for a cloud server, we customize the rules. We tailor our defenses to match the exact apps you use, ensuring your security is tight but never gets in the way of your team’s productivity.
Creative Approaches
We go beyond a simple firewall hardening guide by using creative “stealth” methods. This includes moving important services to non-standard ports and using “port knocking,” where a door only opens if you know the secret digital handshake. This makes your server nearly invisible to automated hackers.
Insightful Strategies
Our strategy involves “thinking like a defender.” We use security hardening strategies that assume a breach could happen, so we build internal walls (segmentation) to stop a threat from moving. We don’t just follow a firewall hardening checklist; we build a strategy that protects your most valuable data first.
Tailored Solutions
Whether you are hardening Windows firewalls for an office team or need deep Linux security hardening for a cloud server, we customize the rules. We tailor our defenses to match the exact apps you use, ensuring your security is tight but never gets in the way of your team’s productivity.
Our Service Cycle
vorza360 provides a professional, step-by-step path to achieving total security hardening for your business.
Step 1
Vulnerability Audit
Step 2
Rule Design
Step 3
Active Defense Setup
Step 4
System Hardening
Step 5
Compliance Verification
Step 6
Continuous Monitoring
Step 1
Vulnerability Audit
We scan your systems to find any open doors or weak spots in your current setup.
Step 2
Rule Design
Our team creates a custom firewall hardening plan based on your specific business needs.
Step 3
Active Defense Setup
We install brute-force protection and log-monitoring tools to watch your server 24/7.
Step 4
System Hardening
We apply Linux security hardening settings to the core system to block advanced exploits.
Step 5
Compliance Verification
We check our work against firewall hardening standards to ensure you are fully protected.
Step 6
Continuous Monitoring
vorza360 stays by your side, updating your rules as new digital threats appear in the world.
Why Choose vorza360 for This Service?
In a world of constant digital threats, you need a partner who takes your safety personally.
Expert Oversight
We don’t just give you a tool; we provide a service. We manage your firewall hardening daily so you don’t have to be a security expert.
Proven Standards
We use industry-leading firewall hardening standards to ensure your business stays ahead of modern hackers and safe from data loss.
Human-Centered Support
Security can be complex, but we make it simple. We explain our IT security hardening steps in plain English and are always here to help if you have questions.
Here is what our Clients are saying About us
Mikkel Andersen (Denmark)
A security audit flagged our Ubuntu servers as seriously under-hardened. vorza360 came in, worked through the findings methodically, applied UFW rules, disabled unused services, and gave us a detailed report of every change made. Our compliance score improved dramatically.
Fatou Diallo (Senegal)
vorza360 applied a thorough security hardening process to our Ubuntu servers and explained every step in plain terms. No jargon, no black box, just transparent, methodical work. The ‘understand-everything’ approach they took gave our team real ownership of our security posture.
Bogdan Petrescu (Romania)
We thought our servers were reasonably secure until vorza360 ran a hardening assessment. They found open ports we didn’t know about, weak SSH configs, and services running unnecessarily. Every issue was fixed cleanly with a clear explanation of why it mattered.
Sana Malik (Pakistan)
vorza360 hardened our entire Ubuntu server fleet ahead of a compliance audit. They implemented CIS benchmarks, configured fail2ban, enforced key-based SSH authentication, and documented everything. We passed the audit without a single finding related to server security.
Luís Ferreira (Portugal)
Security had always been an afterthought for our small team. vorza360 changed that by implementing a proper firewall setup and hardening our Ubuntu servers in a way that was thorough without being disruptive. Our systems have been running securely and stably ever since.
Adaeze Eze (Nigeria)
vorza360 reviewed our Ubuntu environment after a suspicious login attempt and found several misconfigurations that had been there since the initial setup. They locked everything down, set up intrusion detection, and gave our team a clear checklist of what to monitor going forward.
More about Ubuntu
Ubuntu Server Setup & Configuration
Get your business online quickly and securely with vorza360’s expert Ubuntu server setup…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
How does vorza360 configure Ubuntu firewall security using UFW?
UFW (Uncomplicated Firewall) is Ubuntu’s built-in firewall management tool that provides a simplified interface to the underlying iptables or nftables framework. vorza360 configures UFW with a security-first baseline: we start with ufw default deny incoming (blocking all inbound connections by default) and ufw default allow outgoing (permitting all server-initiated outbound connections unless specific egress filtering is required). We then add permit rules only for the specific ports and protocols the server legitimately needs to receive, SSH (on a non-standard port), HTTP and HTTPS for web servers, database ports accessible only from specific application server IPs (never the internet). We enable UFW logging to capture blocked connection attempts for security monitoring. For servers with multiple network interfaces, we configure interface-specific rules where appropriate. We validate the ruleset by testing from both inside and outside the network before considering the firewall configuration complete, and document every rule with its business justification for future review.
What additional security hardening does vorza360 apply to Ubuntu servers beyond UFW?
Comprehensive Ubuntu server security hardening addresses multiple attack surfaces beyond the firewall. vorza360 applies a layered hardening approach: we install and configure fail2ban with jails for SSH, and for web application login endpoints where applicable, implementing progressive IP banning after repeated failed authentication attempts. We configure AppArmor, Ubuntu’s built-in mandatory access control system, to enforce application-level security profiles that limit what files and network resources each service can access, containing the blast radius of a compromised application. We implement auditd for comprehensive system call auditing, capturing privileged account usage, file access to sensitive paths, and network connection events. We configure rkhunter or AIDE for file integrity monitoring, establishing a baseline of critical system files and alerting on any unauthorized modification. We harden the kernel’s network parameters via sysctl, disabling IP forwarding where not required, enabling TCP SYN cookies against SYN flood attacks, and disabling ICMP redirects.
How does vorza360 protect Ubuntu servers from brute-force and automated attacks?
Automated scanners continuously probe internet-accessible Ubuntu servers, attempting to discover default credentials, known vulnerability paths, and authentication endpoints. vorza360 protects Ubuntu servers from automated attacks through multiple defensive layers: we change the SSH port from the default 22 to a non-standard port number, dramatically reducing automated SSH attack noise since the vast majority of scanners only target port 22. We configure fail2ban SSH jail with aggressive settings, locking out an IP after 3 failed attempts within 10 minutes for 24 hours, combined with Cloudflare or a CDN’s bot protection at the network edge for public-facing servers. We implement SSH key-only authentication (disabling password authentication), making brute-force attacks against SSH irrelevant since guessing a cryptographic key is computationally infeasible. For web servers, we configure Nginx or Apache rate limiting rules, implement ModSecurity Web Application Firewall rules, and configure HTTP/S authentication on any admin interfaces that should not be publicly accessible.
How does vorza360 configure Ubuntu server security for compliance with GDPR, PCI-DSS, or similar regulations?
Regulatory compliance on Ubuntu servers requires implementing specific security controls beyond general hardening, and documenting them in a way that satisfies auditors. vorza360 configures Ubuntu servers for regulatory compliance environments through: implementing full disk encryption (LUKS) for servers storing regulated data at rest, configuring TLS encryption for all data in transit (database connections, API calls, file transfers) with current cipher suites, implementing comprehensive audit logging using auditd configured to capture all privileged user actions, data access events, and administrative changes with tamper-evident log forwarding to an external SIEM. We configure automatic security patching for critical CVEs within 48 hours of disclosure. We implement access control based on need-to-know with quarterly access reviews documented for audit evidence. We configure password policies for any remaining password-authenticated accounts, implement MFA for administrative access where available. We produce compliance documentation mapping the Ubuntu server configuration to specific control requirements for your applicable framework, supporting internal and external audit processes.
How does vorza360 perform Ubuntu server security audits?
Security audits provide an objective assessment of an Ubuntu server’s security posture at a point in time, identifying vulnerabilities, misconfigurations, and gaps against security best practices before they are exploited. vorza360 conducts Ubuntu server security audits using a combination of automated tools and manual review: we run Lynis, an open-source security auditing tool for Linux, which performs a comprehensive automated assessment of the server’s hardening status across hundreds of checks covering authentication configuration, file permissions, network settings, installed packages, and running services, producing a prioritized findings report. We run OpenVAS or Nessus for vulnerability scanning that identifies known CVEs in installed software versions. We manually review critical configuration files (sshd_config, UFW rules, cron jobs, sudoers configuration, web server configuration) for security weaknesses not captured by automated tools. We review the auditd and auth.log logs for indicators of past unauthorized access attempts. We produce a structured findings report with each issue rated by severity and accompanied by specific remediation commands or steps.