vorza360 delivers essential firewall configuration and management services to build a strong digital wall around your business. We handle the entire process, from secure firewall installation configuration and management to continuous monitoring, giving you peace of mind and letting you focus on your business.
The Challenge: Marcus’s financial services firm had a perimeter firewall that had been in place for six years with rules that had accumulated without any regular review. A security assessment had identified that over 40% of the firewall rules were either unused or overly permissive, and that the rule set had no logical structure that would allow an auditor to assess its effectiveness. A forthcoming regulatory audit made this an urgent problem.
The vorza360 Solution: We performed a complete firewall rule audit: identifying every unused rule, every overly permissive rule, and every rule that lacked a documented business justification. We rebuilt the rule set from a documented requirements baseline, removing everything that couldn’t be justified, tightening the rules that were genuinely needed, and establishing a rule review and change management process to prevent the same accumulation from recurring.
The Result: The regulatory audit reviewed the firewall configuration and raised no findings. The auditor specifically noted the documented rule justifications and the change management process as evidence of mature network security governance. Marcus’s IT team found ongoing firewall management significantly more straightforward once they understood the logic of the rule set, which the previous accumulated rules had completely obscured.
Yemi Adeleke (Nigeria)
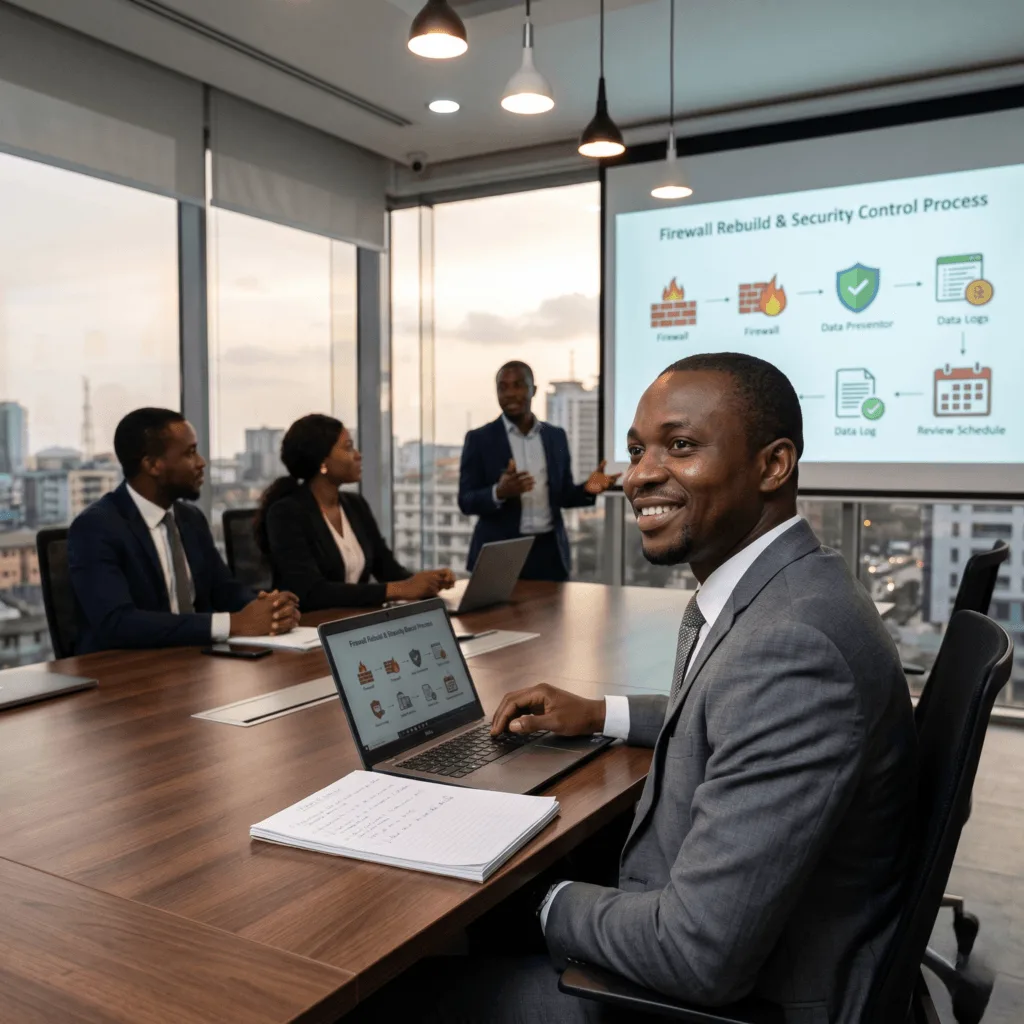
The Challenge: Yemi’s e-commerce company had experienced a successful cyberattack that had originated through a firewall misconfiguration allowing unnecessary inbound access to a development server. The incident had caused data exposure and significant reputational damage. He needed the firewall rebuilt correctly and a process in place to ensure that configuration drift wouldn’t create the same vulnerability again.
The vorza360 Solution: We rebuilt the firewall configuration from scratch using a deny-by-default policy with only explicitly justified allow rules. We implemented intrusion prevention system rules appropriate for their threat profile, set up centralised firewall logging with alerting on suspicious patterns, and established a change management process requiring peer review for any firewall rule modification. We also implemented quarterly configuration reviews as an ongoing control.
The Result: The rebuilt firewall configuration closed the vulnerability that had caused the incident and addressed several other weaknesses identified during the rebuild process. The quarterly configuration reviews over the following year didn’t find any drift back toward the permissive state that had preceded the incident. Yemi’s IT security team described the combination of the correct configuration and the ongoing review process as genuinely changing their confidence in the perimeter.
Hana Svobodová (Czech Republic)
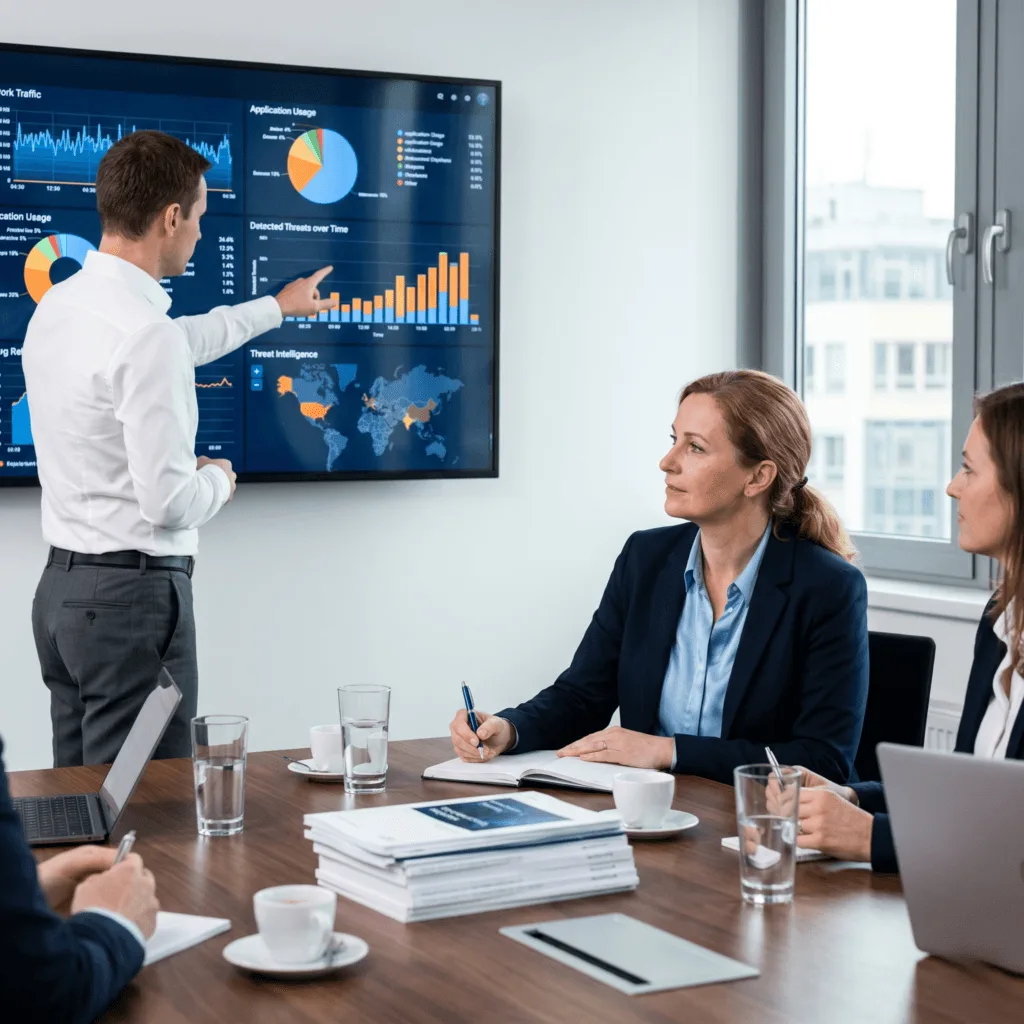
The Challenge: Hana’s healthcare organisation had a next-generation firewall that was configured essentially as a basic packet filter, using none of the application awareness, user identity integration, or threat intelligence features the device was licensed for. She was paying for a capable platform but receiving basic perimeter protection, and lacked the in-house expertise to configure the advanced features correctly.
The vorza360 Solution: We reviewed the existing configuration and designed a phased approach to activating the advanced capabilities: application-layer inspection and control, user identity integration with Active Directory for policy enforcement, SSL inspection for encrypted traffic visibility, and threat intelligence feed integration. We implemented each capability in monitoring mode before enforcing it, to validate the impact before any blocking occurred.
The Result: Hana’s organisation began receiving actionable threat intelligence from the firewall that had previously been invisible. The application-layer visibility identified several applications in use that weren’t sanctioned by IT policy, and the SSL inspection revealed encrypted threat activity that the previous packet-filter approach would never have detected. She described the experience as discovering the firewall had capabilities she didn’t know she owned.
Santiago Reyes (Colombia)
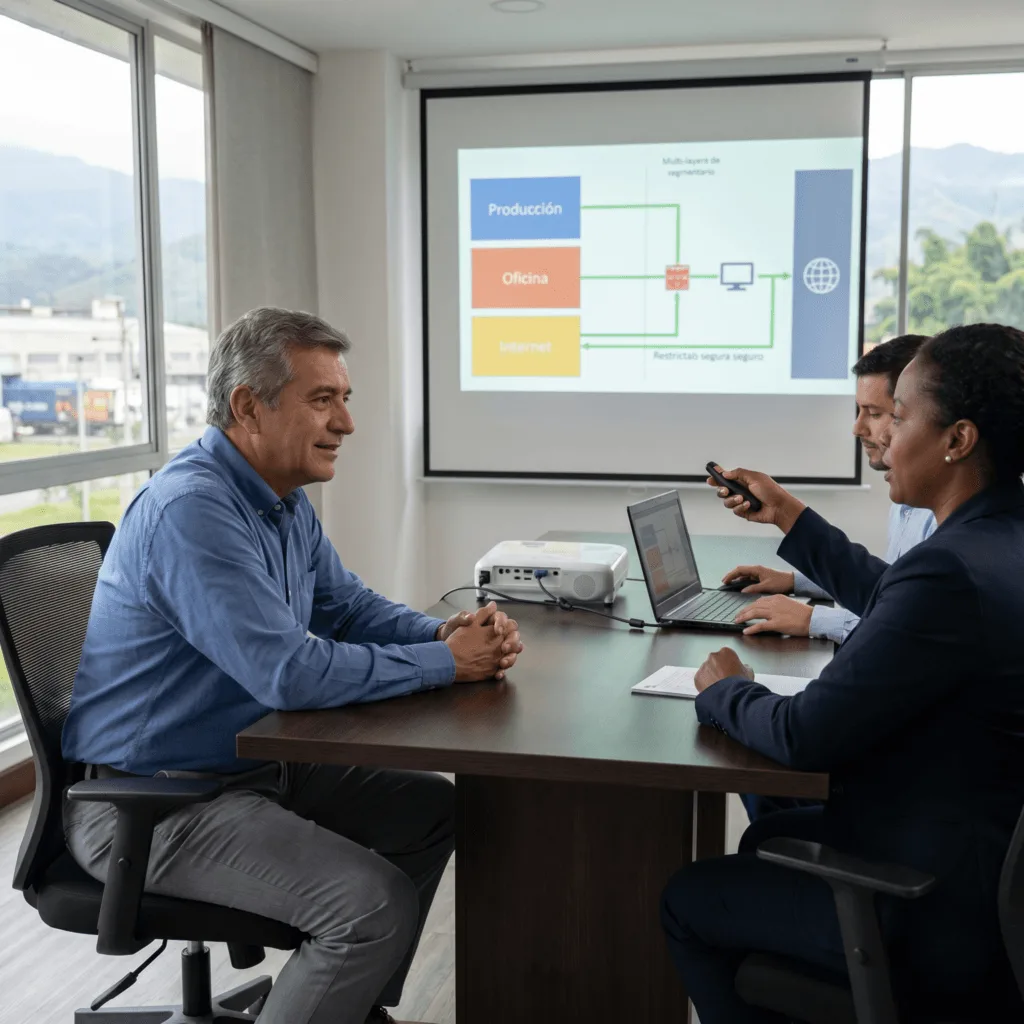
The Challenge: Santiago’s manufacturing company had a single firewall protecting the entire network, with production control systems, office systems, and internet access all passing through the same device with no internal segmentation. A security consultant had warned that a compromise of the office network could potentially reach production control systems, and he needed to address the risk without disrupting the factory.
The vorza360 Solution: We designed a segmentation architecture that placed the production control systems on an isolated network segment behind their own firewall policy, restricting access to only the specific communications that the production systems genuinely required. We implemented the change in stages during planned maintenance Windows, validating production system connectivity before and after each stage to ensure the manufacturing operation was not affected.
The Result: Santiago’s production control systems were properly isolated without any disruption to the manufacturing operation. The security consultant who had raised the original concern re-assessed the architecture after the change and confirmed the risk had been addressed. Santiago’s operations director, who had been the most concerned stakeholder about potential disruption during the change, commented that the process had been handled with far more care than he had expected.
Mia Larsson (Sweden)
The Challenge: Mia’s software development company had grown to the point where their firewall management was taking disproportionate time from their one-person IT team, who was fielding constant requests for rule changes from developers needing to reach specific external services. The ad-hoc rule additions were creating exactly the kind of accumulated permissiveness that would cause problems in future.
The vorza360 Solution: We implemented a managed firewall service that took over the day-to-day rule management, established a formal change request process that evaluated each request against a security policy before implementation, and moved the developer-facing connectivity requirements to an application-aware policy that allowed the classes of traffic developers needed without requiring individual rule additions for each new service.
The Result: Mia’s IT team member recovered significant time previously spent on firewall change requests. The development team found the application-aware policy approach gave them the connectivity they needed without the back-and-forth of individual rule requests. The firewall rule count, which had been growing weekly, stabilised as the structured approach replaced ad-hoc additions.
Kwesi Mensah (Ghana)
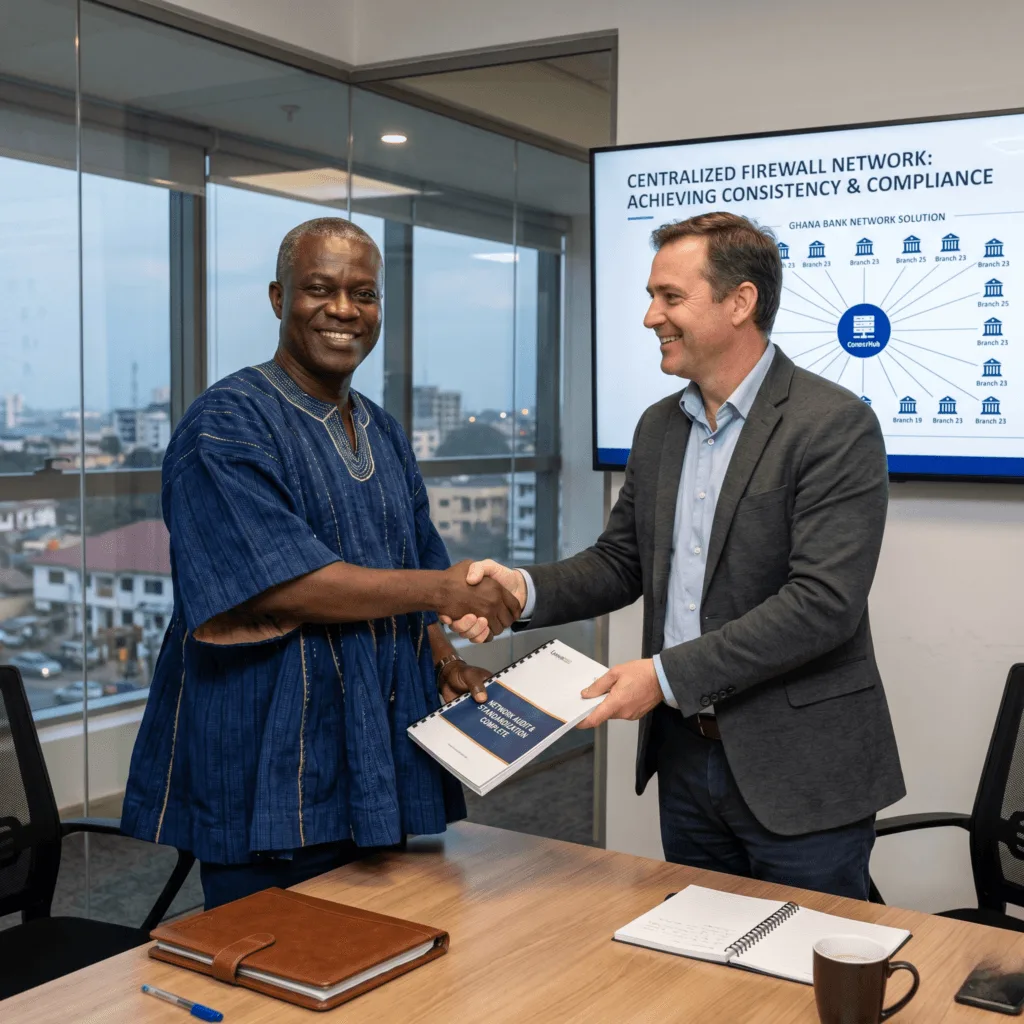
The Challenge: Kwesi’s bank branch network had identical firewalls at each of its twenty-three branches, but each had been configured slightly differently over time as different administrators had responded to local issues with local fixes. The inconsistency made compliance auditing difficult and meant that a security hardening change had to be applied individually to each branch, consuming IT team time every time a policy change was needed.
The vorza360 Solution: We audited the firewall configuration at all twenty-three branches, documented the differences, and built a standardised configuration template that represented the correct baseline for a branch firewall at Kwesi’s bank. We then deployed the standardised configuration to all branches systematically and implemented centralised management that allowed policy changes to be deployed to all branches simultaneously from a single point.
The Result: Kwesi’s compliance audits became significantly simpler once the configurations were standardised, because the auditor could assess one configuration and have confidence it applied to all branches rather than needing to sample multiple. Policy changes that had previously required individual branch maintenance Windows were deployed to all twenty-three branches simultaneously in a single managed change, reducing the administrative burden dramatically.
vorza360’s Tech Edge
Next-Generation Firewall Policies
Stateful Packet Inspection
Intrusion Prevention Systems (IPS)
+ 2
More
Application-Level Traffic Control
Firewall Logging & Reporting
vorza360’s Tech Edge
Next-Generation Firewall Policies
We provide a “digital security gate” for your business, creating custom rules that check every piece of data entering your office to block modern threats and hackers.
Stateful Packet Inspection
Our team uses a “smart filter” service that tracks the state of active connections, ensuring only safe and requested data is allowed to pass through your network.
Intrusion Prevention Systems (IPS)
We provide a 24/7 “active guard” that identifies suspicious behavior on your network and automatically stops attacks before they can reach your computers.
Application-Level Traffic Control
Our team sets up a “smart manager” that lets you decide which apps can use your internet, ensuring your work tools stay fast while blocking risky or distracting software.
Firewall Logging & Reporting
We provide a professional “security diary” that records every blocked threat, giving you clear reports so you can see exactly how your business is being protected.
How we do it
At vorza360, we simplify complex security to ensure your business is protected by a strong, smart firewall.
Simple, Smart Technology
We use advanced firewall hardware and firewall configuration management software that is fast and very reliable. This ensures our setup is strong against new threats while still being easy to update and manage.
Clever Planning
We look closely at your business traffic, user needs, and the data you need to protect. Then we create the exact firewall basic configuration and management plan that locks down your system without blocking your team’s essential work.
Made Just For You
Our service is built around your unique risks. We act as your managed firewall service provider, customizing rules and settings to fit your exact security policies and industry compliance needs perfectly.
Simple, Smart Technology
We use advanced firewall hardware and firewall configuration management software that is fast and very reliable. This ensures our setup is strong against new threats while still being easy to update and manage.
Clever Planning
We look closely at your business traffic, user needs, and the data you need to protect. Then we create the exact firewall basic configuration and management plan that locks down your system without blocking your team’s essential work.
Made Just For You
Our service is built around your unique risks. We act as your managed firewall service provider, customizing rules and settings to fit your exact security policies and industry compliance needs perfectly.
Our Security Deployment Cycle
We follow a clear cycle to install, configure, and continuously manage your firewall for maximum security
Step 1
Security Audit & Planning
Step 2
Hardware/Software Installation
Step 3
Initial Configuration & Ruleset
Step 4
Testing & Validation
Step 5
Go-Live & Baseline Monitoring
Step 6
Optimize & Report
Step 1
Security Audit & Planning
We check your current network and security risks. We define the clear rules needed for your new firewall based on best practices.
Step 2
Hardware/Software Installation
We handle the firewall installation configuration and management, physically installing the device or setting up the software instance.
Step 3
Initial Configuration & Ruleset
We set up the firewall configuration management by creating the first layer of access, traffic, and security policies tailored to your network.
Step 4
Testing & Validation
We thoroughly test the new firewall to ensure it blocks threats and allows necessary business traffic without issues.
Step 5
Go-Live & Baseline Monitoring
The firewall goes live, and we establish continuous monitoring to check performance, look for unusual activity, and provide managed firewall services.
Step 6
Optimize & Report
We constantly check logs, adjust rules as needed, and provide regular reports to keep your security high and prove compliance.
Why Choose vorza360 for Firewall Services
Choosing vorza360 means getting expert, non-stop security management from a dedicated provider.
Expert, Hands-Off Security
We handle all the complex configuration and updating, so you benefit from top-tier security without needing an in-house expert.
Continuous Threat Protection
Our managed firewall services mean your firewall is always monitored, constantly updated, and instantly ready to fight new digital threats.
Guaranteed Compliance
We ensure your firewall policies are set up to meet strict industry and government data security regulations.
Here is what our Clients are saying About us
James Harrington (United Kingdom)
Our firewall rule set had accumulated years of additions with no removals and our security team had no confidence in what it was actually allowing. vorza360 audited every rule, removed the redundant and conflicting ones, and documented the remainder. Our policy is now understood and defensible.
Hana Al-Sayed (Kuwait)
vorza360 manages our firewall infrastructure on an ongoing basis with policy reviews, firmware updates, and change management that ensures our rules reflect our current business requirements. Firewall management as a managed service rather than a task our team fits around everything else.
Mihai Stancu (Romania)
After a security incident exposed gaps in our perimeter defence, vorza360 rebuilt our firewall architecture with next-generation firewall capabilities including application awareness and intrusion prevention. Our security posture improved substantially.
Rahul Kumar (Pakistan)
vorza360 implemented application-aware firewall policies for our organisation that control traffic based on application identity rather than just port and protocol. The granularity of control has improved our security and helped us identify applications our policy should not allow.
Charlotte Nielsen (Denmark)
vorza360 migrated our ageing firewall platform to a modern next-generation firewall with minimal disruption to our users. The migration planning they did, including a parallel run period, meant the cutover was risk-free.
Amara Balde (Guinea)
vorza360 configured and manages our firewall infrastructure with the responsiveness our business requires. Security policy changes that used to take days now happen within hours of a request.
More about Networking
SD-WAN Solutions
vorza360 delivers modern SD-WAN solutions that completely change how your wide…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What does vorza360's firewall configuration and management service include?
vorza360’s firewall service covers the complete security lifecycle: Security Audit & Planning (understanding your network, risks, and compliance requirements before designing firewall policy), Hardware/Software Installation (deploying the firewall appliance or virtual instance), Initial Configuration & Ruleset (creating access policies, traffic control rules, and intrusion prevention settings tailored to your environment), Testing & Validation (verifying the firewall blocks threats and permits legitimate business traffic correctly), Go-Live & Baseline Monitoring (activating continuous security monitoring from day one), and Optimize & Report (ongoing rule refinement, threat intelligence updates, and regular compliance reports). vorza360 acts as your fully managed firewall service provider, handling all the complexity so your team never needs to.
What is a Next-Generation Firewall (NGFW) and why does vorza360 recommend it?
A Next-Generation Firewall goes far beyond traditional firewalls that simply block traffic based on port numbers and IP addresses. NGFWs inspect traffic at the application layer, they can identify and control specific applications (blocking TikTok while allowing Zoom, for example), detect and block sophisticated threats like encrypted malware and zero-day exploits using deep packet inspection and threat intelligence feeds, integrate Intrusion Prevention Systems (IPS) that actively block attacks in real time, and enforce user-based policies rather than just IP-based rules (so the same device has different access rights depending on who is logged in). vorza360 recommends NGFW for all business environments because modern threats require modern defenses, basic port-filtering firewalls leave significant gaps that attackers routinely exploit.
How does vorza360 keep firewall rules current and effective over time?
Firewall rules that are not actively maintained become a security liability, outdated rules accumulate, legitimate-seeming exceptions get added without proper review, and the policy drifts from its original intent over time. vorza360’s managed firewall service includes a structured rule lifecycle management program: quarterly rule audits to identify and remove obsolete or overly permissive rules, application of vendor security patches and firmware updates through a tested change management process, continuous threat intelligence feed updates so the firewall recognizes the latest known malicious IPs and domains, and a formal change request process for all new rules to prevent unauthorized or poorly-scoped policy additions. Firewall Logging & Reporting provides clear monthly evidence of threats blocked, rules triggered, and any anomalous patterns that warrant investigation.
How does vorza360 ensure firewall management meets compliance requirements?
Many regulatory frameworks (PCI DSS, HIPAA, ISO 27001, GDPR) have specific requirements for firewall configuration, documentation, and auditing. vorza360 configures firewalls with compliance as a design constraint, not as an afterthought, ensuring network segmentation isolates regulated data environments (cardholder data, protected health information) from general network traffic, inbound and outbound traffic rules are documented with business justification, all firewall rule changes are logged with timestamps and approver identity, unauthorized access attempts are logged and reviewed regularly, and formal compliance reports are generated on the schedule required by your auditors. We provide the evidence package your auditors need, connection logs, rule lists, change records, and policy documentation, saving significant time and cost at audit time.
What should I do if my business currently has no firewall or an outdated one?
Operating without a properly configured firewall, or with an outdated one running obsolete firmware, exposes your business to serious and easily exploitable vulnerabilities. vorza360 recommends starting with an immediate Security Audit & Planning engagement to assess your current exposure and define the right firewall solution for your network size, traffic profile, and compliance requirements. We can typically have a new Next-Generation Firewall designed, deployed, and actively monitoring your network within 1-2 weeks for most business environments. For organizations with an existing but outdated firewall, we offer a Firewall Configuration Review service that assesses the current ruleset, identifies critical misconfigurations and gaps, and implements hardening improvements without requiring a full replacement.