vorza360 delivers immediate, expert network troubleshooting and robust incident response to minimize downtime and quickly fix security threats. We use continuous network performance monitoring and systematic procedures to find the root cause of network issues, from slow speed to major outages, ensuring your business is always stable and secure.
The Challenge: Erik’s manufacturing company had been experiencing intermittent network outages affecting the production line for three months. His internal IT team had investigated repeatedly, replaced several suspected components, and engaged the network equipment vendor without finding the root cause. The outages were occurring roughly every two to three weeks, lasted between twenty minutes and two hours, and were costing the business real production time each occurrence.
The vorza360 Solution: We deployed persistent network monitoring capturing packet-level data at the key network segments, with logging retained over a long enough window to capture the next incident. When the outage occurred, the captured data showed a spanning tree topology change event triggered by a specific switch port, caused by an intermittent fault in a patch cable connecting two distribution switches that the visual inspection had missed. The cable was replaced and the fault did not recur.
The Result: The three-month recurring outage problem was resolved within two weeks of our deployment. The root cause, a physically marginal patch cable, was something that could only be identified by observing the exact sequence of events during an actual outage with sufficient logging in place. Erik’s team had done exactly the right things in their investigation; they had simply lacked the persistent, low-level visibility that the fault required to be caught.
Amina Diallo (Guinea)
The Challenge: Amina’s telecommunications company had a customer-facing service disruption that occurred without warning during a business day, taking multiple services offline simultaneously. The incident lasted four hours and affected hundreds of customers. The post-incident review identified that the impact had been extended significantly by the time it took to diagnose and isolate the fault, and that the response had been uncoordinated.
The vorza360 Solution: We conducted a post-incident analysis of the network fault and the response, identifying both the technical root cause, a misconfigured routing policy change that had caused a BGP route withdrawal, and the response process failures: no runbook for this type of incident, no clear ownership once it escalated beyond the first responder, and insufficient diagnostic tooling for the on-call engineer. We addressed both dimensions: implementing the technical fix and establishing incident response procedures and tooling.
The Result: The routing policy misconfiguration was corrected and a change management process was implemented to prevent similar errors. More importantly, the incident response procedures meant that the next significant network incident was handled with coordinated ownership, clear escalation paths, and diagnostic tools that gave the responder actionable information rather than requiring extended investigation under pressure. The mean time to resolution for subsequent incidents halved compared to the pre-incident baseline.
Lorenzo Ferrari (Italy)
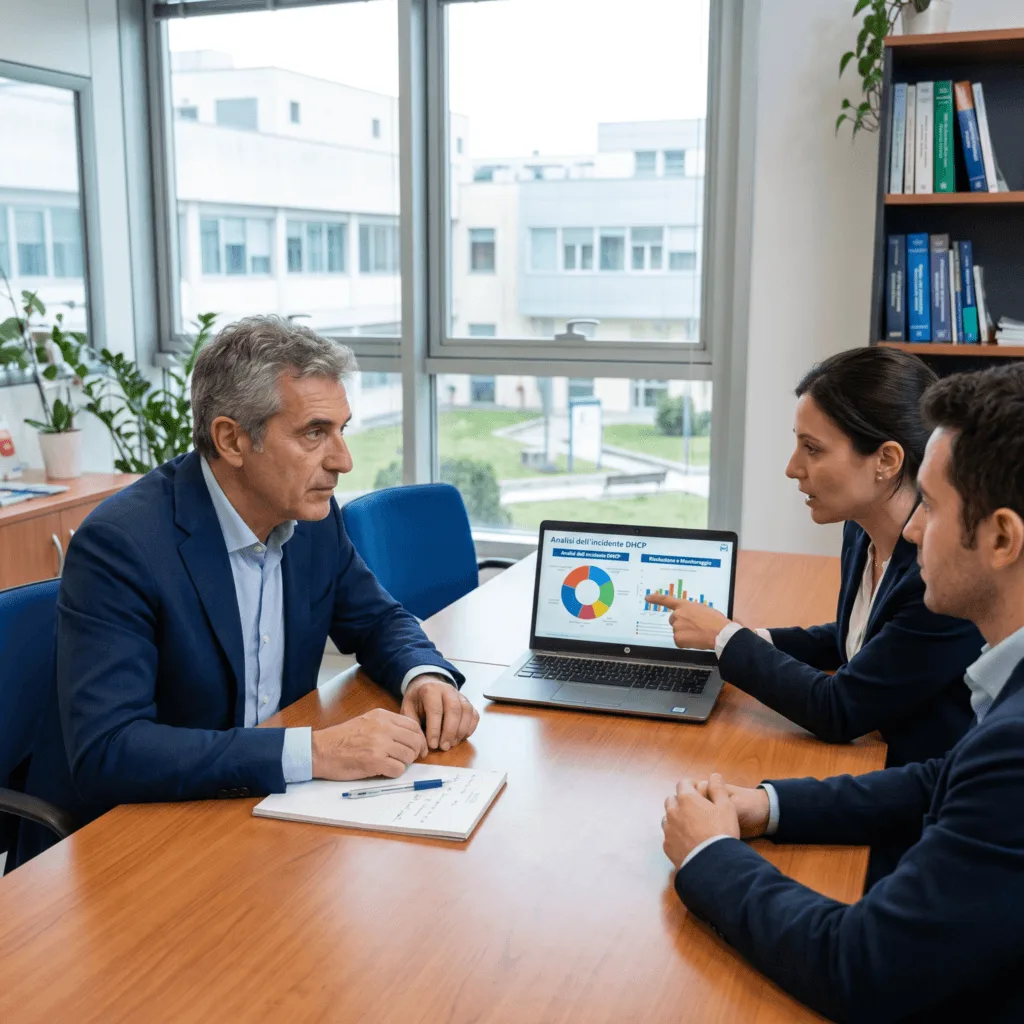
The Challenge: Lorenzo’s hospital had a network incident during overnight hours that affected clinical system access. The on-call IT team had resolved the immediate symptoms by rebooting network equipment but without understanding the root cause, and when clinical staff arrived for the morning shift, the same issue recurred. The incident then extended through the early morning clinical period, affecting patient care coordination.
The vorza360 Solution: We were engaged to conduct a forensic analysis of the incident and provide emergency troubleshooting support. We reviewed the available logs, identified that the root cause was a DHCP scope exhaustion rather than a hardware fault, and resolved the underlying issue permanently. We also implemented DHCP monitoring with alerting so the team would have warning of approaching scope exhaustion in future, and produced an incident report detailing the root cause and the corrective actions.
The Result: The DHCP exhaustion was resolved and clinical system access was restored. The monitoring implementation ensured the same issue would generate an alert well in advance of causing an outage in future. Lorenzo’s IT director used the incident report to drive investment in network monitoring capabilities that had been approved in principle but not prioritised, the incident provided the concrete evidence of consequences that moved it to urgent priority.
Damilola Adekunle (Nigeria)
The Challenge: Damilola’s financial services firm had a network security incident where unusual outbound traffic was detected by a third party and reported to the firm. The internal team had no network security monitoring in place and no established incident response process. The absence of monitoring data meant they couldn’t determine how long the suspicious activity had been occurring or what data might have been exfiltrated.
The vorza360 Solution: We provided emergency incident response support: deploying network traffic capture to characterise the ongoing suspicious activity, identifying the compromised endpoint that was the source, isolating it from the network, and conducting forensic analysis of available network logs to establish a timeline as far as the limited logging allowed. We simultaneously helped the team establish immediate monitoring capabilities so they had visibility into the remainder of the investigation.
The Result: The incident was contained and the compromised endpoint was isolated within hours of our engagement. The forensic analysis established the extent of the suspicious activity as far as the available evidence allowed, which was sufficient for the regulatory notification Damilola’s compliance team needed to make. The monitoring capability deployed during the response remained in place and became the foundation of the firm’s ongoing network security monitoring programme.
Sophie Martin (France)
The Challenge: Sophie’s retail company had a recurring network performance problem that manifested as slow POS transaction times at unpredictable intervals. The problem had been reported by store staff for over a year, investigated multiple times by the internal IT team and the POS vendor support team, and attributed to various causes without resolution. The intermittent nature and the multiple parties involved had allowed it to remain unresolved.
The vorza360 Solution: We took ownership of the troubleshooting with a methodology focused on capturing data during the actual problem rather than investigating afterwards. We deployed monitoring probes at the affected stores that captured network performance metrics at the POS terminal level continuously, and established a reporting mechanism for store staff to log incidents with timestamps. This approach captured the next occurrence in full, revealing a DNS resolution delay that affected POS transactions whenever the primary DNS server was briefly overloaded.
The Result: A problem that had persisted for over a year was resolved within three weeks of our engagement. The DNS issue was straightforward to fix once it was correctly identified; the challenge had been capturing it precisely while it was occurring rather than investigating a system that appeared normal between incidents. Sophie’s retail operations team described the resolution as a significant relief, the issue had affected staff and customer experience repeatedly and the inability to resolve it had been a source of ongoing frustration.
Arjun Nair (India)
The Challenge: Arjun’s technology company had a network incident during a product launch event where connectivity to the cloud infrastructure serving the launch dropped intermittently, causing the demo environment to become unreliable at the worst possible moment. The incident was resolved by rebooting a router, but without understanding the root cause, he had no confidence the same thing wouldn’t happen again at the next critical moment.
The vorza360 Solution: We conducted a post-incident analysis using the available device logs, traffic data, and the timeline of the incident as reported by the team. We identified that the router’s NAT table had been exhausted by the unusually high connection rate from the launch event traffic, which had not been anticipated in the network design. We resolved the root cause by reconfiguring the NAT settings and implementing connection rate monitoring to alert before the threshold was reached.
The Result: Arjun’s team understood the root cause for the first time and had a permanent fix rather than a symptom treatment. The connection rate monitoring meant that if a future event generated similar traffic patterns, they would have advance warning rather than a failure. He described having a root cause explanation he could act on as significantly better than the unresolved uncertainty that the incident had created.
The vorza360 Difference in Network Stability
Your network is the most important tool you have. When it stops, everything stops.
vorza360 makes sure your network never stops for long. We use the best network monitoring tools to watch your system all day and night. We are always looking for problems, so we can start network troubleshooting on small issues before they slow you down. If a hack or major crash happens, our quick incident response plan starts right away. We stop the threat, clean up the damage, and keep your business safe. With vorza360, you get guaranteed stability and experts who are always ready to jump in instantly.
How we do it
We follow a structured and proactive approach to find problems fast and manage security incidents effectively.
Constant Monitoring
We use the best network monitoring tools to watch your system 24/7. This helps us spot very small issues (like a slow connection or a tiny hiccup) before they turn into big problems, allowing us to fix them proactively.
Clear Security Plan
When a problem happens, our engineers don’t guess. We follow a clear, smart network troubleshooting process using diagnostic tools to quickly find the exact root cause of the issue, isolate it, and make sure we fix it the right way, the first time.
Fast Crisis Recovery
We have a clear incident response plan ready for any hack or major crash. If a security threat hits, we follow defined steps to stop the attack right away, clean up the network completely, and restore your business operations fast and safely.
Constant Monitoring
We use the best network monitoring tools to watch your system 24/7. This helps us spot very small issues (like a slow connection or a tiny hiccup) before they turn into big problems, allowing us to fix them proactively.
Clear Security Plan
When a problem happens, our engineers don’t guess. We follow a clear, smart network troubleshooting process using diagnostic tools to quickly find the exact root cause of the issue, isolate it, and make sure we fix it the right way, the first time.
Fast Crisis Recovery
We have a clear incident response plan ready for any hack or major crash. If a security threat hits, we follow defined steps to stop the attack right away, clean up the network completely, and restore your business operations fast and safely.
Here is what our Clients are saying About us
Tomasz Wiśniewski (Poland)
A network incident took our production systems offline at the worst possible time. vorza360 responded quickly, diagnosed the root cause accurately, and restored service in a fraction of the time our internal team would have taken. Having expert help available made a critical difference.
Hessa Al-Rashidi (Qatar)
vorza360 resolved a persistent intermittent connectivity issue that had defeated our internal team for three months. Their systematic diagnostic approach identified a subtle routing problem that had been overlooked. Resolved in one day what we had been working around for months.
Cătălin Gheorghe (Romania)
vorza360 responded to a network security incident, contained the affected systems, preserved forensic evidence, and produced a clear incident report. Their incident response process was professional and the documentation they produced satisfied our auditors.
Pooja Nair (India)
vorza360 troubleshot a complex network performance issue affecting our trading systems where every millisecond matters. Their network analysis tools and expertise identified latency introduced by a misconfigured switch that our monitoring had not detected.
Anisa Putri (Indonesia)
vorza360 provides network incident response under a retainer agreement. Knowing that expert help is available within the hour gives our IT management team confidence that network problems will be resolved quickly regardless of when they occur.
Chioma Adeyemi (Nigeria)
vorza360 investigated and resolved a network issue that had been causing intermittent application timeouts for weeks. The root cause, a failing switch port generating excessive error frames, had been invisible to our monitoring. vorza360 found it and fixed it.
More about Networking
SD-WAN Solutions
vorza360 delivers modern SD-WAN solutions that completely change how your wide…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What network troubleshooting and incident response services does vorza360 provide?
vorza360 provides a proactive and reactive network troubleshooting and incident response service built on three pillars: Constant Monitoring (using best-in-class network monitoring tools to watch every device and connection 24/7, spotting early warning signs before they escalate), Clear Security Plan (following a structured diagnostic process using professional tools to identify the exact root cause of any issue and fix it correctly the first time), and Fast Crisis Recovery (executing a pre-defined incident response plan the moment a security breach, major outage, or critical failure is declared, containing the threat, cleaning the environment, and restoring operations as rapidly as possible while minimizing data loss and business impact).
How quickly does vorza360 respond to a network outage or incident?
vorza360’s response times are defined by incident severity in the managed service agreement. Critical incidents, network outages, security breaches, or failures affecting all users, trigger an immediate response with engineers engaged within 15 minutes of detection, 24 hours a day, 7 days a week, including weekends and public holidays. High-severity issues (significant performance degradation or partial outages affecting multiple users) receive a response within 1 hour. Medium and low-severity issues are addressed within agreed business-hours Windows. Because vorza360’s Network Performance Monitoring detects most issues automatically before they reach outage severity, many incidents are resolved proactively, without users ever experiencing an impact, which is the highest form of incident response.
What is vorza360's process for diagnosing the root cause of a network problem?
vorza360 follows a structured network troubleshooting process that eliminates guesswork and ensures permanent rather than temporary fixes. The process begins with Symptom Collection & Scope Definition (understanding exactly what is failing, who is affected, and when it started), followed by Isolation (systematically narrowing the problem to a specific network layer, device, or path using tools like ping, traceroute, packet capture, and log analysis), Root Cause Identification (determining whether the failure is hardware, software, configuration, or external), Resolution & Verification (implementing the fix and confirming the issue is fully resolved, not just symptom-masked), and Post-Incident Documentation (recording the root cause, resolution, and any preventive actions to avoid recurrence). This methodology ensures issues are genuinely fixed rather than temporarily suppressed.
How does vorza360 handle a cybersecurity incident on the network?
When a cybersecurity incident is detected or reported, vorza360 activates a formal Incident Response Plan: Identification (confirming the nature and scope of the threat, what systems are affected and what data may be at risk), Containment (immediately isolating affected network segments, revoking compromised credentials, and blocking attacker communication channels to prevent the threat from spreading), Eradication (removing malware, closing exploited vulnerabilities, and cleaning affected systems to eliminate the attacker’s presence from the environment), Recovery (restoring systems from clean backups, validating integrity, and carefully reintroducing them to the production network with enhanced monitoring), and Post-Incident Review (documenting a full timeline of events, root cause analysis, and specific remediation actions to prevent recurrence). Forensic evidence is preserved throughout for potential legal or insurance purposes.
Can vorza360 help with network troubleshooting for businesses without dedicated IT staff?
Yes. vorza360 is specifically designed to serve as the external networking team for businesses that do not have dedicated in-house network engineers. Our managed monitoring service means network issues are detected and triaged by vorza360’s engineers, not by end users noticing problems and calling a helpdesk. When an issue occurs, your contact at vorza360 communicates in plain business language, not technical jargon, explaining what happened, what was done, and what the impact was. For recurring issues, we escalate to root cause resolution rather than band-aid fixes. Our goal is to make your network completely invisible to your business, reliable, secure, and fast enough that your team simply never thinks about it.