
Network Security Audits &
Penetration Testing
vorza360 delivers essential network security audit services to find weak spots and fully protect your business network. We perform a detailed network security audit to check your defenses and then conduct network penetration testing to safely test your system like a real hacker would.

Shopify

WordPress

Figma

PHP

Flutter

React Js

Node Js

Python

Swift

Java

Vue.js

Kotlin

CSS

HTML
JavaScript
Customer Success Story
Sebastian Richter (Germany)
The Challenge: Sebastian’s fintech startup was preparing for a Series B funding round where institutional investors had requested evidence of a third-party security assessment. His internal team believed the network was reasonably secure but had never had it tested by an external assessor. He needed a credible penetration test with documented findings before the investor due diligence process began.
The vorza360 Solution: We conducted an external and internal network penetration test covering the perimeter, internal network segmentation, wireless infrastructure, and remote access systems. We exploited the vulnerabilities we identified, including an exposed management interface and weak internal segmentation, to demonstrate actual attack paths, then provided a detailed findings report with prioritised remediation recommendations and evidence for each finding.
The Result: Sebastian’s team had a clear picture of their actual security posture rather than their assumed one, and the penetration test report provided the third-party security assessment evidence the investors required. The critical findings were remediated before the due diligence process began, and the investors’ security review was completed without the findings that would have caused concern at that stage of funding.
Chioma Okafor (Nigeria)
The Challenge: Chioma’s bank had a compliance requirement for annual network penetration testing but had been using the same testing firm for six years, with assessments that her security team privately questioned were genuinely rigorous. After the compliance team flagged that the annual test might not be meeting regulatory expectations, she needed a genuinely independent assessment.
The vorza360 Solution: We conducted a comprehensive network security audit and penetration test using a methodology aligned to the banking sector regulatory requirements: external perimeter testing, internal network penetration from a simulated compromise, Active Directory attack path analysis, and wireless security assessment. We found and demonstrated exploitation of several vulnerabilities that the previous assessments had not identified.
The Result: The independent assessment found genuine issues that the previous annual tests had missed. Chioma’s security team had the evidence they needed to drive remediation of real vulnerabilities rather than managing a compliance process around a test they suspected was inadequate. The regulator, when informed of the independent assessment findings and the remediation programme, responded positively to the bank’s initiative in seeking more rigorous testing.
Lars Andersen (Denmark)
The Challenge: Lars’s logistics company had recently completed a major network infrastructure upgrade and wanted an independent assessment of the security posture of the new environment before relying on it for operations. His internal team had designed and built the new network but acknowledged that having the same team assess their own work was not independent validation.
The vorza360 Solution: We performed a post-deployment security audit of the new network infrastructure, reviewing the firewall configurations against the design intent, testing the network segmentation between operational zones, assessing the wireless security configuration, and validating the remote access controls. We also conducted targeted penetration testing of the access paths between the different network segments.
The Result: The security audit identified several configuration gaps between the designed security architecture and the implemented one, not intentional weaknesses but implementation errors that had crept in during the complex build process. Lars’s team addressed every finding before the new environment was placed into full production use. He described having an independent pair of eyes on the implementation as exactly the validation process a high-stakes network build needed.
Zara Ahmed (Pakistan)
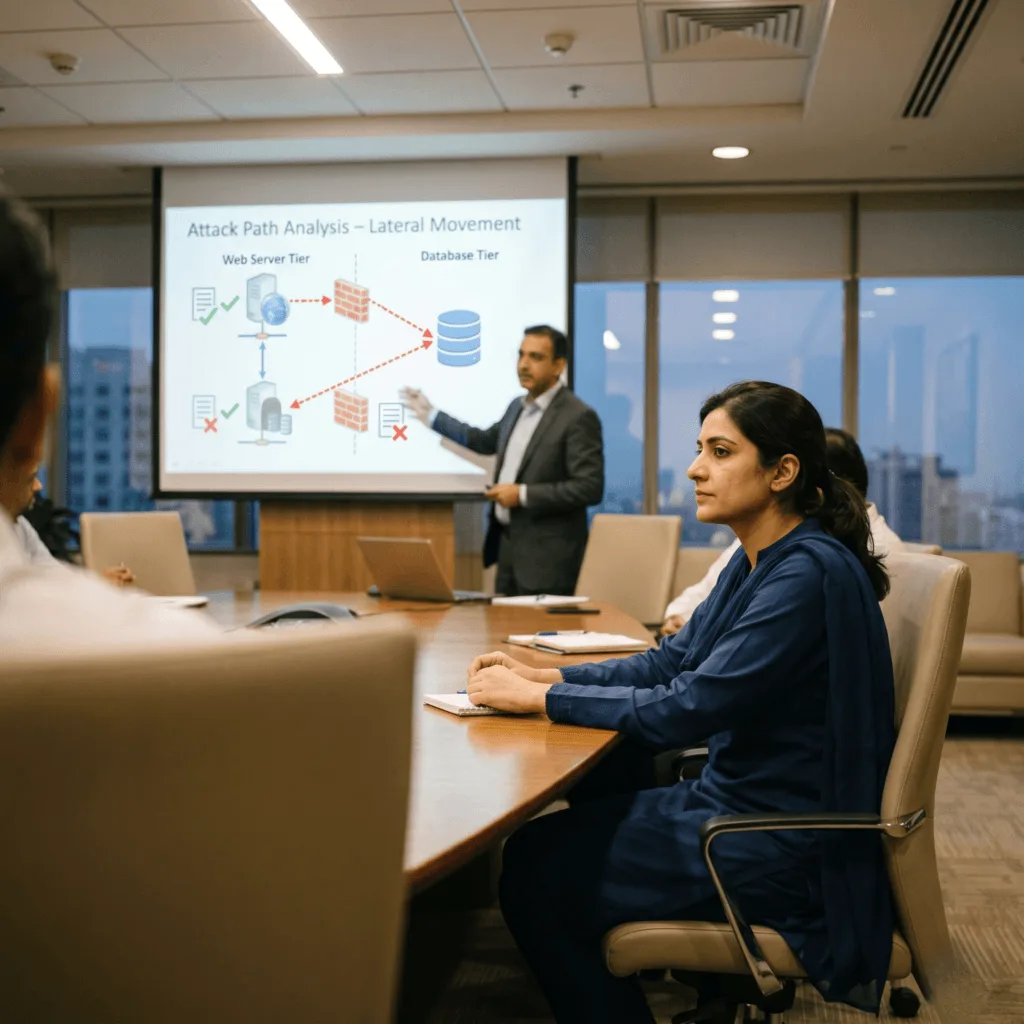
The Challenge: Zara’s e-commerce company had experienced a data breach where customer payment data had been exfiltrated. The forensic investigation had identified that attackers had moved laterally from a compromised web server to the database layer, but the investigation hadn’t provided enough detail about the network attack path to drive effective remediation. She needed a post-incident assessment to understand and close the specific vulnerabilities exploited.
The vorza360 Solution: We conducted a post-incident network security audit focused on the attack path that the breach had used: assessing the segmentation between the web tier and database tier, reviewing the firewall rules between those segments, testing whether the lateral movement would still be possible in the current configuration, and examining the logging and detection capabilities that had failed to alert on the attack in progress.
The Result: The post-incident audit identified the specific segmentation gap and the logging deficiency that had allowed the breach to succeed and go undetected. Zara’s team addressed both, and a follow-up penetration test confirmed that the specific attack path used in the breach was no longer viable. Her security team used the audit findings to drive a broader set of improvements, with the breach as concrete evidence of why the investment was necessary.
Ivan Petrov (Bulgaria)
The Challenge: Ivan’s healthcare organisation had never had a network security assessment conducted. A recent healthcare sector breach at another organisation had prompted his board to ask for assurance about their own network security posture, and he needed a credible response that was based on evidence rather than assumptions.
The vorza360 Solution: We conducted a network security audit and penetration test covering the external perimeter, internal network, clinical system network segments, and the interface between clinical and administrative networks. We presented findings in both technical detail for the IT team and an executive summary for the board that communicated risk in business terms rather than technical ones.
The Result: Ivan’s board received a credible, evidence-based picture of the organisation’s network security posture. The executive summary gave them the governance visibility they had asked for, and the technical findings gave the IT team a clear remediation programme. Several of the findings required prompt attention, and the board described having concrete evidence of what needed to be done as more useful than the vague reassurance they had received previously.
Ana Ferreira (Brazil)
The Challenge: Ana’s insurance company was required by industry regulation to conduct network penetration testing annually, but the scope and methodology requirements in the regulation were detailed, and her previous testing provider had been using a methodology that her internal auditor questioned was fully compliant. She needed testing that would withstand scrutiny from both the regulator and internal audit.
The vorza360 Solution: We conducted penetration testing using a methodology explicitly aligned to the regulatory requirements, documenting the scope, approach, tools, and evidence at the level of detail the regulation specified. We produced findings reports in the format required for regulatory submission, including the exploit demonstration evidence and remediation validation testing that the regulation required to be documented.
The Result: Ana’s annual regulatory submission was accepted without challenge. Her internal auditor reviewed the testing methodology documentation and confirmed it met the compliance standard they had questioned with the previous provider. She described the value of having a testing partner who understood the regulatory requirements as significant, the actual penetration testing capabilities were comparable, but the compliance credibility made the difference.
vorza360’s Tech Edge
Network Vulnerability Assessment
Firewall Rule Audits
Internal & External Network Testing
+ 2
More
Risk & Compliance Reporting
Security Hardening Recommendations
vorza360’s Tech Edge
Network Vulnerability Assessment
We provide a professional “digital scan” that searches your office network for any weak spots or open doors that hackers might try to use.
Firewall Rule Audits
Our team performs a “security check-up” on your digital gates, making sure your rules are up-to-date and only letting the right people into your system.
Internal & External Network Testing
We provide a “friendly hack” service, testing your defenses from both inside your office and outside on the internet to ensure you are fully protected.
Risk & Compliance Reporting
Our team delivers a clear “safety report card” that explains your security levels in simple words, helping you meet official industry standards and rules.
Security Hardening Recommendations
We provide a “strength-building” plan for your network, giving you expert advice on how to lock down your systems and make them much harder to break into.
Full Network Security Audit
We deliver comprehensive analysis of your network infrastructure, policies, and controls to identify risks.
Advantages
- Deep review using industry-leading network security audit software.
- Checking firewalls, routers, and server configurations for flaws.
- Policy analysis to ensure user access and password rules are strong.
- Identifying compliance gaps against standards like ISO 27001 or HIPAA.
Network Penetration Testing Services
We simulate real-world attacks against your network to expose vulnerabilities in a safe environment.
Advantages
- External network penetration testing services to check defenses from the outside (like a remote hacker).
- Internal testing to check what damage a compromised insider could do.
- Detailed exploitation attempts on found vulnerabilities to prove the risk.
- Delivering clear, actionable steps for fixing every security flaw found.
Wireless and Remote Access Security
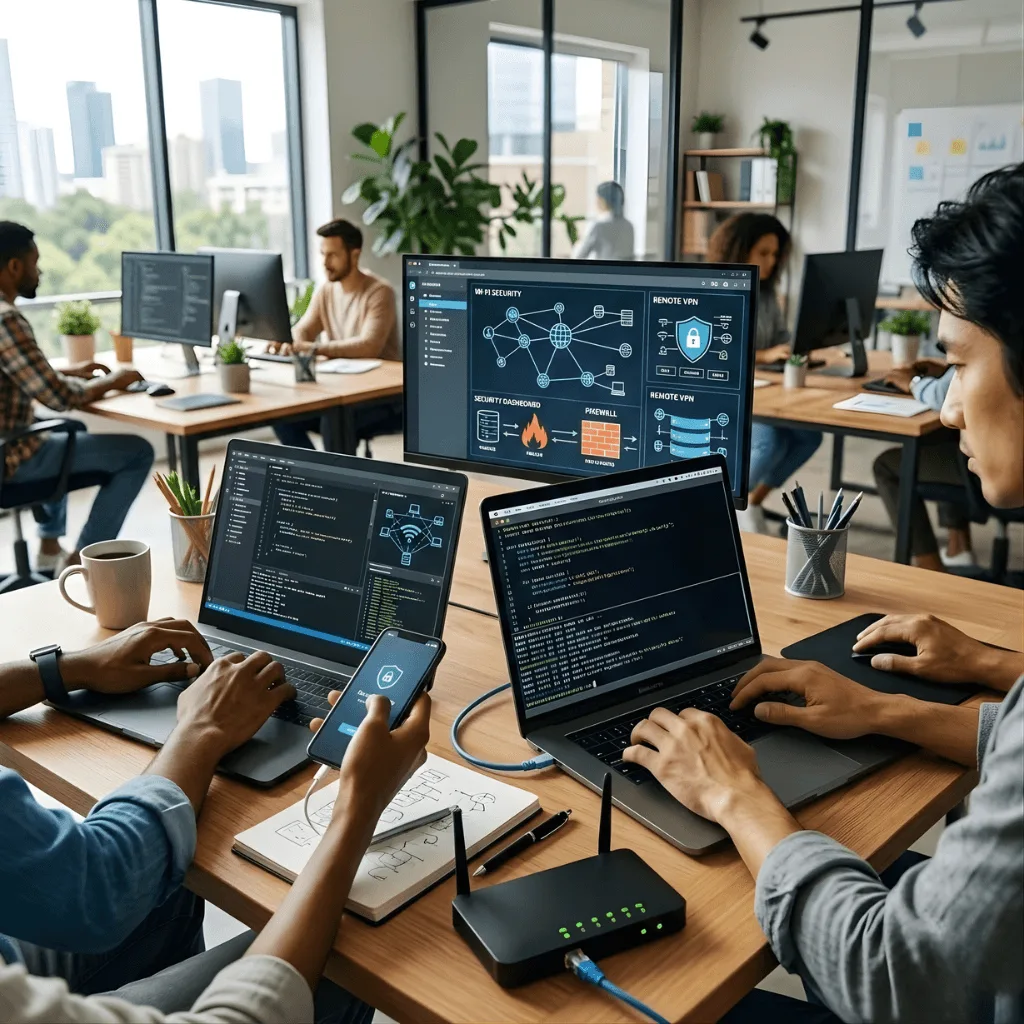
We focus on the often-overlooked entry points provided by Wi-Fi and remote worker connections.
Advantages
- Wireless network penetration testing and security auditing of Wi-Fi encryption and access controls.
- Testing VPN setups for weaknesses that could allow unauthorized remote access.
- Reviewing mobile device security policies and controls.
- Ensuring remote access is fully secure and isolated from internal systems.
Remediation Planning and Support
We don’t just find problems; we help you fix them efficiently and permanently.
Advantages
- Prioritizing vulnerabilities based on real-world risk and impact.
- Creating a step-by-step plan for fixing all identified flaws.
- After-fix verification testing to confirm the issue is completely resolved.
- Ongoing network security audit services support and advice.
Security Tool and Policy Review
We ensure your existing security investments are working as hard as they should be.
Advantages
- Reviewing the effectiveness of your current antivirus, detection, and response tools.
- Advising on the proper use of network security audit software for continuous monitoring.
- Updating security policies to cover new technologies and remote work requirements.
- Maximizing the value of your existing security infrastructure.
Full Network Security Audit
We deliver comprehensive analysis of your network infrastructure, policies, and controls to identify risks.
Advantages
- Deep review using industry-leading network security audit software.
- Checking firewalls, routers, and server configurations for flaws.
- Policy analysis to ensure user access and password rules are strong.
- Identifying compliance gaps against standards like ISO 27001 or HIPAA.
ADVANTAGES
- Deep review using industry-leading network security audit software.
- Checking firewalls, routers, and server configurations for flaws.
- Policy analysis to ensure user access and password rules are strong.
- Identifying compliance gaps against standards like ISO 27001 or HIPAA.
Network Penetration Testing Services
We simulate real-world attacks against your network to expose vulnerabilities in a safe environment.
Advantages
- External network penetration testing services to check defenses from the outside (like a remote hacker).
- Internal testing to check what damage a compromised insider could do.
- Detailed exploitation attempts on found vulnerabilities to prove the risk.
- Delivering clear, actionable steps for fixing every security flaw found.
ADVANTAGES
- External network penetration testing services to check defenses from the outside (like a remote hacker).
- Internal testing to check what damage a compromised insider could do.
- Detailed exploitation attempts on found vulnerabilities to prove the risk.
- Delivering clear, actionable steps for fixing every security flaw found.
Wireless and Remote Access Security
We focus on the often-overlooked entry points provided by Wi-Fi and remote worker connections.
Advantages
- Wireless network penetration testing and security auditing of Wi-Fi encryption and access controls.
- Testing VPN setups for weaknesses that could allow unauthorized remote access.
- Reviewing mobile device security policies and controls.
- Ensuring remote access is fully secure and isolated from internal systems.
ADVANTAGES
- Wireless network penetration testing and security auditing of Wi-Fi encryption and access controls.
- Testing VPN setups for weaknesses that could allow unauthorized remote access.
- Reviewing mobile device security policies and controls.
- Ensuring remote access is fully secure and isolated from internal systems.
Remediation Planning and Support
We don’t just find problems; we help you fix them efficiently and permanently.
Advantages
- Prioritizing vulnerabilities based on real-world risk and impact.
- Creating a step-by-step plan for fixing all identified flaws.
- After-fix verification testing to confirm the issue is completely resolved.
- Ongoing network security audit services support and advice.
ADVANTAGES
- Prioritizing vulnerabilities based on real-world risk and impact.
- After-fix verification testing to confirm the issue is completely resolved.
- Creating a step-by-step plan for fixing all identified flaws.
- Ongoing network security audit services support and advice.
Security Tool and Policy Review
We ensure your existing security investments are working as hard as they should be.
Advantages
- Reviewing the effectiveness of your current antivirus, detection, and response tools.
- Advising on the proper use of network security audit software for continuous monitoring.
- Updating security policies to cover new technologies and remote work requirements.
- Maximizing the value of your existing security infrastructure.
ADVANTAGES
- Reviewing the effectiveness of your current antivirus, detection, and response tools.
- Advising on the proper use of network security audit software for continuous monitoring.
- Updating security policies to cover new technologies and remote work requirements.
- Maximizing the value of your existing security infrastructure.
Here is what our Clients are saying About us

Henrik Larsson (Sweden)
vorza360 conducted a network security audit that found vulnerabilities our internal team had not identified, some of which had been present for years. The detailed findings report and remediation guidance gave us a clear programme to work through.
Noura Al-Ali (UAE)
vorza360 performed network penetration testing for our organisation before our annual security certification. The issues they found were fixed before our auditors saw them. A cost-effective investment that protected our certification.
Bogdan Constantin (Romania)
vorza360 conducted a wireless security audit that found our guest network had a misconfiguration allowing access to internal resources. A finding that would have been embarrassing if discovered by anyone else first.
Sneha Kapoor (India)
vorza360 performed a comprehensive network security assessment covering our perimeter, internal segmentation, and wireless security. The assessment covered the attack surfaces our team had been focused on and the ones we had not considered.
Kasper Andersen (Denmark)
vorza360 conducted red team network testing that demonstrated how an attacker would move laterally through our network after an initial compromise. Seeing the attack path clearly was more persuasive for our board than any audit report.
Fatima Al-Sayed (Nigeria)
vorza360 performed a network security audit for our bank that assessed our controls against our central bank’s cybersecurity framework requirements. The findings were specific, the remediation guidance was practical, and our next regulatory review was cleaner.
More about Networking
SD-WAN Solutions
vorza360 delivers modern SD-WAN solutions that completely change how your wide…
Data Center Networking & Virtualization
vorza360 delivers essential data center networking and network virtualization in data…
VoIP & Unified Communication Solutions
vorza360 delivers modern VoIP and unified communications solutions that combine your…
Network Troubleshooting & Incident Response
vorza360 delivers immediate, expert network troubleshooting and robust incident response…
IoT & Smart Device Network Integration
vorza360 delivers full IoT and smart device network integration services to connect all your…
Network Design & Architecture
vorza360 offers network design & architecture service to help businesses build strong, safe…
+ 5
More
LAN/WAN Setup & Management
vorza360 offers LAN/WAN setup and management services to build, connect, and manage…
Wireless Network Deployment & Optimization
vorza360 delivers full wireless network deployment and optimization services to give…
Firewall Configuration & Management
vorza360 delivers essential firewall configuration and management services to build a…
More about Networking
SD-WAN Solutions
Data Center Networking & Virtualization
VoIP & Unified Communication Solutions
+ 12
More
Network Troubleshooting & Incident Response
IoT & Smart Device Network Integration
Network Design & Architecture
LAN/WAN Setup & Management
Wireless Network Deployment & Optimization
Frequently Asked Questions
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is included in vorza360's network security audit service?
vorza360’s full network security audit covers five areas: Full Network Security Audit (deep review of all network infrastructure, firewall rules, server configurations, access controls, and security policies using professional audit tools), Network Penetration Testing Services (simulated real-world attacks from both external internet-facing positions and internal perspectives to expose exploitable vulnerabilities), Wireless & Remote Access Security (targeted testing of Wi-Fi encryption, rogue access points, and VPN configurations), Remediation Planning & Support (prioritized fix plans with after-fix verification testing), and Security Tool & Policy Review (assessing the effectiveness of your existing security investments and updating policies for current threats and technology). Every engagement concludes with a clear, actionable report in plain language, not just a list of CVE numbers.
What is the difference between a network security audit and penetration testing?
A Network Security Audit is a systematic review and analysis of your network’s security posture, examining configurations, policies, access controls, patch levels, and compliance against known best practices and frameworks. It identifies what is misconfigured or missing. Network Penetration Testing goes further: our certified ethical hackers actively attempt to exploit the vulnerabilities found (and others not yet discovered) using the same tools and techniques a real attacker would use, proving whether theoretical vulnerabilities are actually exploitable and demonstrating the real-world business impact. vorza360 recommends both: the audit provides a comprehensive inventory of security issues, and penetration testing validates which ones represent genuine, immediate risk that warrants urgent remediation priority.
How does vorza360 conduct penetration testing safely without disrupting production systems?
vorza360 follows a carefully controlled penetration testing methodology that protects production systems throughout the engagement. Before testing begins, we establish a clear Rules of Engagement document that defines the scope (which systems can be tested), testing hours (to avoid peak business periods), out-of-scope systems (critical production infrastructure that must not be touched), and escalation procedures if a critical vulnerability is discovered that requires immediate remediation. Our testers use professional tools and manual techniques that are designed to identify vulnerabilities without triggering system instability. All testing activity is logged in detail so any unexpected behavior during the testing window can be attributed and investigated. Critical vulnerabilities are reported immediately, not held until the final report.
How often should a business conduct network security audits and penetration tests?
The appropriate frequency depends on your industry, compliance requirements, and rate of change in your environment. vorza360’s general recommendations: annual full network security audits for all businesses (as a minimum baseline), with additional audits triggered by significant infrastructure changes (major cloud migrations, new office openings, merger/acquisition IT integration); annual penetration tests for organizations without specific compliance requirements, increasing to semi-annual or quarterly for regulated industries (PCI DSS, HIPAA, SOC 2) or high-value targets (financial services, healthcare, critical infrastructure). After any major security incident, an emergency audit should be conducted regardless of the regular schedule. Many compliance frameworks specify minimum testing frequencies, and vorza360’s compliance team ensures your testing cadence meets all applicable regulatory obligations.
What happens after a network security audit or penetration test, how does vorza360 help with remediation?
vorza360 treats remediation support as an integral part of the audit and penetration testing service, not a separate engagement. After testing is complete, we deliver a comprehensive report with findings categorized by severity (Critical, High, Medium, Low), a plain-language explanation of each vulnerability and its potential business impact, and a prioritized, step-by-step remediation plan. For clients on a managed services agreement, vorza360 implements the high and critical remediation actions directly. For other clients, we provide detailed technical guidance and remain available for questions during the remediation process. After the remediation is complete, we conduct After-Fix Verification Testing, retesting the specific vulnerabilities that were addressed to confirm they have been fully resolved and have not introduced new issues.