Take control of your office network with vorza360’s active directory and group policy services. We organize your users and automate security rules so your team stays productive and your data stays locked tight.
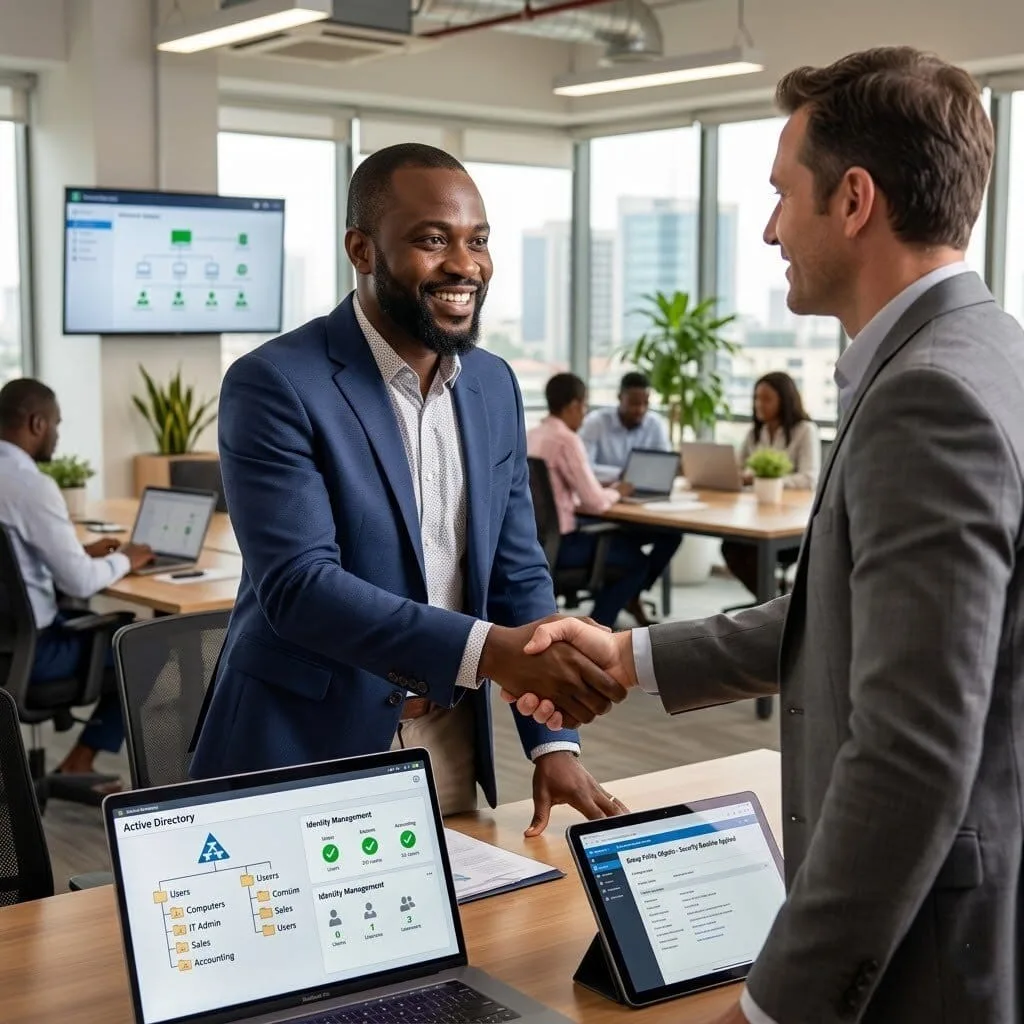
The Challenge: Thomas’s company had Active Directory deployed but had never applied Group Policy consistently. Different departments had different local security settings, software was installed inconsistently across machines, and the helpdesk spent significant time on configuration issues that Group Policy should have prevented.
The vorza360 Solution: vorza360 audited the existing AD structure and Group Policy Objects, cleaned up the accumulated conflicting GPOs, designed a clean GPO structure by organisational unit, and implemented policies covering security settings, software deployment, desktop configuration, and network drive mapping. Each policy was tested in a pilot OU before broad deployment.
The Result: Helpdesk tickets related to software and configuration inconsistencies dropped by over 50% in the month after the Group Policy rollout. Thomas’s IT team spent less time firefighting individual machine configurations and more time on work that required their expertise. The consistent environment also made security audits significantly simpler.
Hana Al-Rashid (Kuwait)
The Challenge: Hana’s organisation was preparing for a cyber insurance renewal and the insurer required evidence of specific Active Directory security controls, MFA for privileged accounts, admin tiering, and privileged access workstations. None of these were in place, and the renewal was six weeks away.
The vorza360 Solution: vorza360 implemented the required AD security controls within the timeline: tiered administration model separating Tier 0 domain admin accounts from Tier 1 server admin and Tier 2 workstation admin accounts, Protected Users security group for privileged accounts, and fine-grained password policies with stronger requirements for admin accounts.
The Result: The cyber insurance renewal was completed with all required controls evidenced. Hana’s organisation received a favourable premium because of the security improvements, and the tiered admin model reduced the risk of credential theft attacks that had been the insurer’s primary concern.
Vlad Ionescu (Romania)
The Challenge: Vlad’s company had grown through acquisition and had three separate Active Directory forests that needed to be consolidated. Users were confused by different login credentials for different systems, and IT was managing three separate identity environments with significant overhead.
The vorza360 Solution: vorza360 planned and executed a phased AD consolidation: forest trust establishment to allow cross-forest resource access, user and group migration using ADMT, application re-authentication testing for each system, and a communications plan so users knew when their credentials would change.
The Result: The three-forest environment was consolidated into a single forest over four months with no user-visible service disruptions. Vlad’s IT overhead for identity management reduced substantially, and users had the single-credential experience they’d been requesting since the acquisitions.
Priya Rajgopal (India)
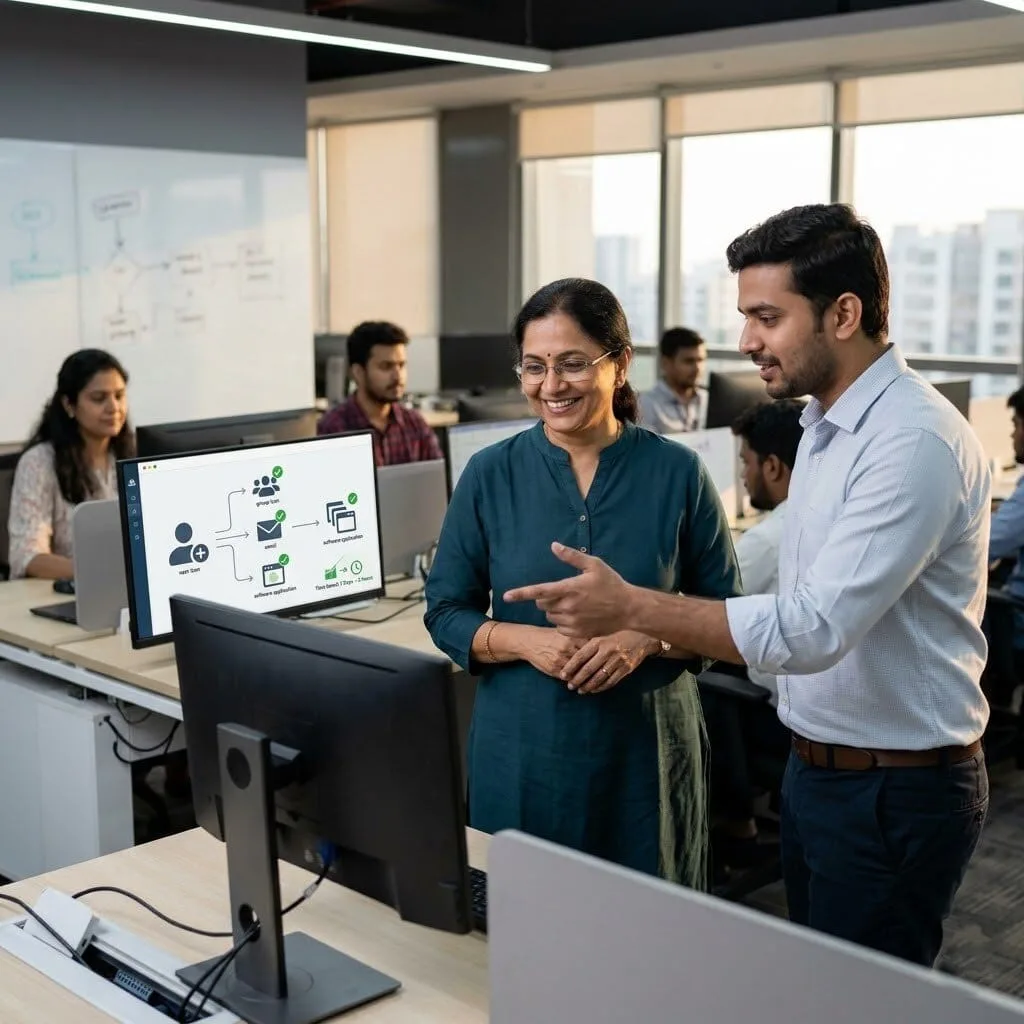
The Challenge: Priya’s IT team was spending days onboarding each new employee because there was no automation, account creation, group memberships, mailbox provisioning, and software access all required manual steps across multiple systems, and mistakes were common.
The vorza360 Solution: vorza360 designed and implemented an AD-based onboarding workflow using PowerShell automation: new user accounts created from a standard template based on department and role, group memberships assigned automatically, email notification sent to the manager with credentials, and an offboarding counterpart that disabled and moved accounts when staff left.
The Result: Onboarding time reduced from two days to two hours. Priya’s helpdesk team handled the same volume of new starters with significantly less effort, and the consistency of automated provisioning meant fewer errors and fewer access-related tickets in the first week of each new employee’s tenure.
Erik Andersen (Norway)
The Challenge: Erik’s company had suffered a security incident where an attacker with a compromised standard user account had elevated privileges to domain admin through a misconfigured delegation. The security review that followed found significant AD hygiene problems, stale accounts, overprivileged service accounts, and unnecessary domain admin membership.
The vorza360 Solution: vorza360 conducted a full Active Directory security assessment, identified and resolved every significant finding: stale accounts disabled and eventually removed, service accounts created with minimum required permissions using Managed Service Accounts where possible, domain admin group membership reduced to only the accounts and humans that genuinely required it, and Protected Users group applied to all privileged accounts.
The Result: The post-remediation security assessment found no remaining significant AD security findings. Erik’s security team had a clean, documented AD environment and a process for ongoing AD hygiene that would prevent the accumulation of the same problems over time.
Femi Adebayo (Nigeria)
The Challenge: Femi’s organisation had Active Directory but was not using it to its potential, users still logged into workstations with local accounts, there was no centralised password policy, and the domain existed primarily because it had come with their server, not because anyone had designed it for their needs.
The vorza360 Solution: vorza360 redesigned their AD structure with an appropriate OU hierarchy for their organisation, migrated workstations from local accounts to domain accounts, implemented Group Policy for security baseline and software management, and trained their IT team on AD administration concepts and common tasks.
The Result: Femi’s organisation started using AD as the central identity and management platform it was designed to be. Password resets that had required physical workstation access could now be done centrally, software could be deployed across the organisation in hours rather than days, and the security baseline was consistent across every domain-joined device.
The Central Brain of Your Office
Managing a growing team can feel like a puzzle when everyone has different needs. Active directory and group policy act as the central brain of your business, keeping track of who is who and what they are allowed to do. Instead of walking to every desk to update a password or install a printer, we use these tools to handle it all from one place. It’s about creating a professional, organized digital workspace where new employees can get to work in minutes, not hours.
By setting up active directory group policy objects, we build a “rulebook” that your computers follow automatically. Whether it’s ensuring everyone has the company wallpaper or blocking dangerous websites, our service ensures that your business standards are met across every laptop and server you own. We focus on making your daily IT management invisible and effortless, so you can spend your time on what really matters, that is growing your company.
vorza360’s Tech Edge
Domain Controller Architecture
Organizational Unit (OU) Design
Group Policy Object (GPO) Management
+ 2
More
Domain Trust Configuration
Authentication & Authorization Flow
vorza360’s Tech Edge
Domain Controller Architecture
We build the “command center” of your network, ensuring your Windows active directory group policy is always available and lightning-fast.
Organizational Unit (OU) Design
Our team neatly categorizes your staff like “Accounting” or “Sales” so we can give each group exactly what they need without clutter.
Group Policy Object (GPO) Management
We create custom active directory group policy objects to automate everything from security locks to software updates.
Domain Trust Configuration
If your business has multiple branches, we build “digital bridges” so your teams can share files safely between offices.
Authentication & Authorization Flow
We manage the “check-in” process, using active directory and group policy management to verify every login and protect your most private data.
Tools
Tools & Plugins We Use
GPMC (Group Policy Management Console)
The primary dashboard our team uses to build and link your active directory group policy.
ADManager Plus
A specialized tool for active directory and group policy management that helps us handle bulk user changes in seconds.
RSAT (Remote Server Administration Tools)
A professional plugin that allows us to manage your Windows active directory group policy safely from our support center.
Netwrix Auditor
A security tool we use to watch over your active directory group policy objects and alert us if any unauthorized changes are made.
Here is what our Clients are saying About us
Sigrid Ólafsdóttir (Iceland)
Our Active Directory had grown without any structure, OUs were a mess, group policies were conflicting, and nobody was sure what was applied where. vorza360 redesigned the entire AD structure, cleaned up GPOs, and documented everything. Our IT team can finally manage the environment with confidence.
Bilal Nawaz (Pakistan)
vorza360 implemented a proper Group Policy framework for our organisation that enforced security baselines across all workstations automatically. Before this, we were relying on users to follow security guidelines themselves. The ‘policy-enforced’ approach they built removed that dependency entirely.
Cristian Mureșan (Romania)
We’d accumulated years of orphaned user accounts, stale computer objects, and redundant security groups in Active Directory. vorza360 came in, ran a full audit, cleaned up everything unnecessary, and restructured the OU hierarchy logically. Our AD is now something we’re not embarrassed to show an auditor.
Kavya Reddy (India)
vorza360 designed and implemented a fine-grained password policy structure in our AD that enforces different requirements for different user roles. Privileged accounts now have stricter controls while standard users get a sensible policy that doesn’t generate constant helpdesk tickets. A well-balanced solution.
Tobias Stein (Germany)
Our Group Policy setup had become a source of mysterious issues, things applying that shouldn’t, settings not applying that should. vorza360 untangled the entire GPO structure, resolved every conflict, and set up a testing process so new policies get validated before they reach production. Real order restored.
Yetunde Ogundimu (Nigeria)
vorza360 integrated our Windows Active Directory with our cloud identity provider so users have a single set of credentials for both on-premises and cloud resources. The ‘one-identity’ model they implemented has simplified access management enormously and our helpdesk ticket volume dropped noticeably.
More about Windows Server
Windows Server Installation & Setup
Get a rock-solid foundation for your business with vorza360’s professional Windows Server…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is Active Directory and why is it essential for managing a business network?
Active Directory (AD) is Microsoft’s centralized directory service that acts as the authoritative identity database for your entire organization, managing user accounts, computers, groups, and access permissions from a single location. Without Active Directory, each computer on your network manages its own users independently, creating separate login credentials for every machine, making password resets and account lockouts a machine-by-machine operation, and making it impossible to enforce consistent security policies across the organization. With AD, every user has a single domain account that logs them into any computer on the network, permissions to shared folders and applications are managed centrally, security policies are enforced automatically on every device through Group Policy, and IT administrators can manage the entire environment from one interface.
How does vorza360 design and implement an Active Directory structure for a business?
Active Directory structure design has long-term consequences, a poorly designed AD environment accumulates complexity that becomes increasingly difficult to manage. vorza360 designs AD structures based on your organization’s size, geographic distribution, and administrative model. We design the Organizational Unit (OU) hierarchy to reflect your organization’s structure, typically by department or location, enabling efficient Group Policy application and delegation of administrative rights. We establish naming conventions for user accounts, computer accounts, and groups that are consistent and meaningful. We configure the appropriate number of Domain Controllers for resilience (a minimum of two in any production environment). We implement AD Sites and Services configuration for organizations with multiple physical locations to control authentication traffic. We document the complete design and provide ongoing AD administration support.
How does vorza360 use Group Policy to enforce security settings across an organization?
Group Policy is one of the most powerful IT management tools in the Windows ecosystem, it allows vorza360 to configure and enforce hundreds of settings across every computer and user in your domain from a single location. We create Group Policy Objects (GPOs) linked to appropriate OUs that enforce: password complexity, length, and expiration requirements; account lockout policies that protect against brute-force attacks; Windows Firewall profiles and rules; USB device restrictions preventing unauthorized data transfer; desktop restrictions preventing users from installing unapproved software; browser security settings and proxy configuration; software deployment and removal; mapped drive and printer assignments that appear automatically when users log in; and Windows Update configuration. GPOs apply automatically whenever a user logs in or the Group Policy refresh cycle runs, ensuring consistent enforcement without any manual work.
How does vorza360 troubleshoot Active Directory issues such as login failures and replication problems?
Active Directory issues can range from individual user login failures to domain-wide authentication outages, and diagnosing them requires systematic investigation rather than trial-and-error. vorza360 troubleshoots AD issues using a structured approach: for user login failures, we check account status, password expiry, account lockout status (using the Lockout and Management Tools), event logs on the relevant Domain Controllers for authentication error codes, and Group Policy application issues. For replication problems between Domain Controllers, we use repadmin /showrepl and repadmin /replsummary to identify which DCs are failing to replicate and dcdiag to identify the root cause, DNS resolution issues, network connectivity problems, or time synchronization failures are the most common causes. We resolve replication failures before they impact authentication and document the root cause and resolution.
How does vorza360 manage Active Directory for organizations with multiple office locations?
Multi-site Active Directory environments require careful design of AD Sites and Services to ensure that authentication traffic stays local (users authenticate against a Domain Controller in their own physical location rather than traversing a WAN link to a DC in another office), replication between sites is controlled and scheduled appropriately to avoid consuming WAN bandwidth during business hours, and each site has at least one Domain Controller for resilience against WAN link failures. vorza360 configures AD Sites and Services by creating a Site object for each physical location, defining site link objects that define the cost and replication schedule between sites, placing the appropriate number of Domain Controllers in each site (considering the size of the location and its WAN link reliability), configuring the KCC (Knowledge Consistency Checker) for optimal replication topology, and implementing Read-Only Domain Controllers (RODCs) for branch offices with lower physical security.