
User & Permission Management
Keep your business data safe and organized with vorza360’s professional user permission management services. We ensure the right people have the right access, making your team’s workflow smooth and secure.

Shopify

WordPress

Figma

PHP

Flutter

React Js

Node Js

Python

Swift

Java

Vue.js

Kotlin

CSS

HTML
JavaScript
Customer Success Story
Bernhard Koch (Germany)
The Challenge: Bernhard’s company had a growing database, but as they added more staff, the system became painfully slow. They assumed they needed expensive new hardware. However, the real bottleneck was Database & Technical Access Management, the system was struggling because service accounts and user permissions weren’t tuned to handle the high volume of simultaneous data requests.
The vorza360 Solution: We performed a deep audit of their SQL Management Studio user permissions. We optimized the “Service Accounts” that the database uses to talk to the server and cleaned up “ghost” permissions from former employees that were cluttering the system. We also applied a Privilege Delegation Model, ensuring the database only used the exact amount of “power” needed for each task.
The Result: Query performance improved instantly without spending a cent on new RAM. By correctly managing the technical access layer, Bernhard’s team delivered a faster experience for every user using the hardware they already owned.
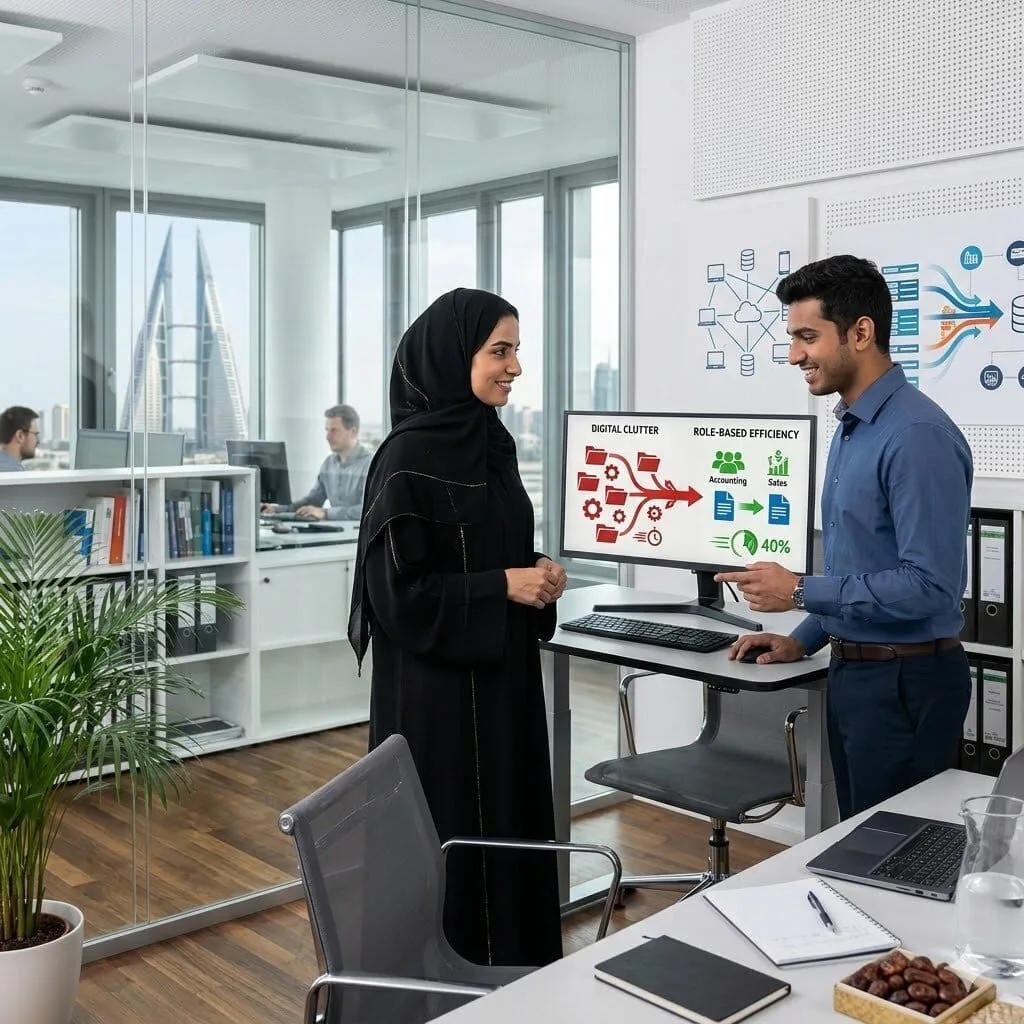
Aisha Al-Farsi (Bahrain)
The Challenge: Aisha’s company had 40 people sharing a remote server, and the “digital clutter” was making it crawl. Profiles took minutes to load because every user had “Full Edit” rights to massive shared folders, causing the server to sync too much data every time someone logged in.
The vorza360 Solution: We implemented Role-Based Access Control (RBAC). We organized users into logical groups (like “Accounting” and “Sales”) and moved them to a “Read-Only” default for non-essential folders. By using NTFS Permission Structuring, we ensured that when a user logs in, the server only loads the specific files they actually need for their job.
The Result: Application launch times dropped by 40%. The “helpdesk headache” disappeared because users no longer had to wait for the server to sort through thousands of unnecessary file permissions. The environment is now organized, lean, and ready for more growth.
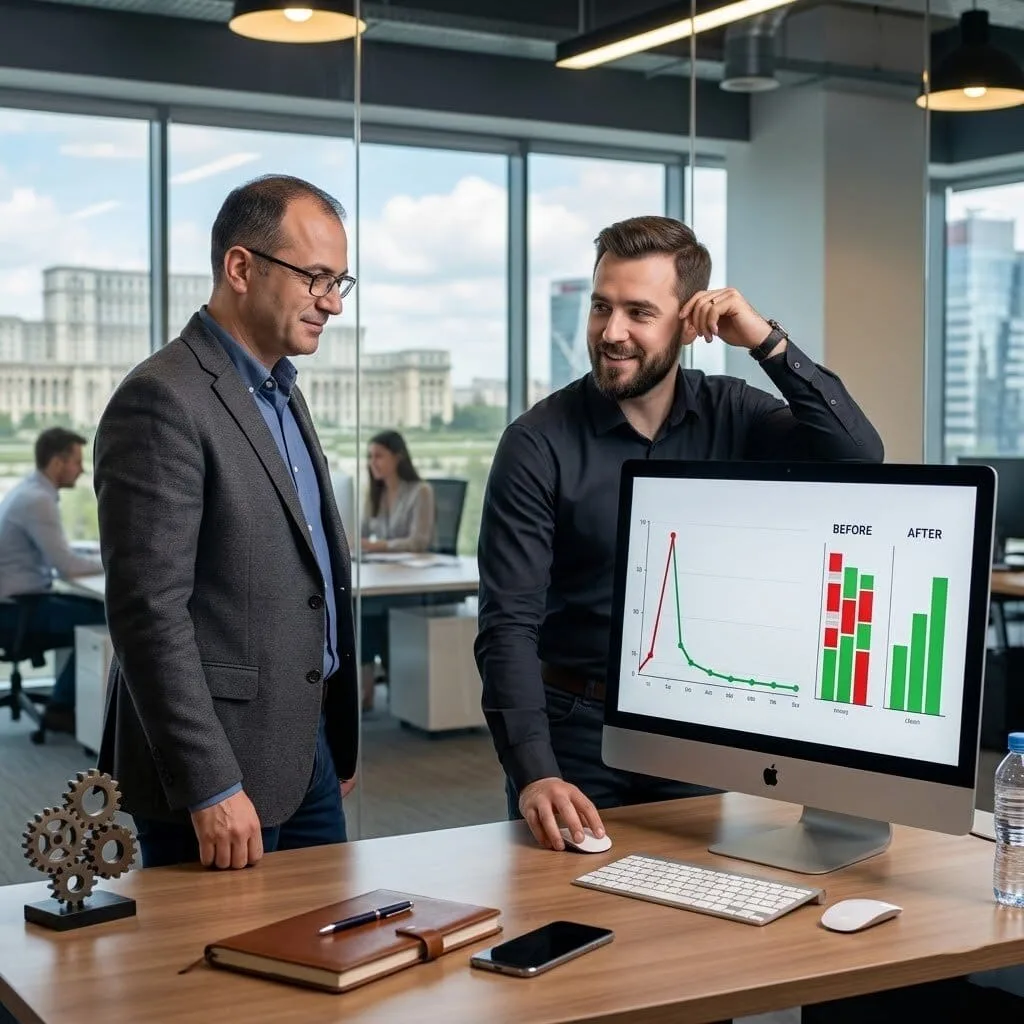
Cosmin Barbu (Romania)
The Challenge: Cosmin’s file server was lagging, with simple “save” operations taking several seconds. The server was physically fast, but the User & Permission Management was a mess, folders were accidentally left open to “Everyone,” and the server was working overtime checking complex, overlapping permission rules for 150 users.
The vorza360 Solution: We performed a Security & Compliance Audit to find and fix “access leaks.” We simplified the permission tree, removing the “Everyone” tags and replacing them with clean, department-based groups. We also set up Standard vs. Admin levels to prevent regular users from accidentally changing system-wide folder settings.
The Result: File response times became near-instant again. By cleaning up the “logic” of who can see what, we reduced the server’s workload. Cosmin’s users stopped noticing the server, which, in the world of IT, is the ultimate success.
Rohit Gupta (India)
The Challenge: Rohit’s server was occasionally “freezing” for no clear reason. While the hardware looked fine, an audit revealed that an old external contractor’s account was still active and running a heavy, unmonitored data sync in the background that was saturating the system.
The vorza360 Solution: We implemented External User & Guest Access Support. We identified all “Guest” keys and set up automatic expiry dates so they turn off the moment a job is done. We also established a Human-in-the-loop verification process to track exactly what outside contractors are doing while they are inside the network.
The Result: The intermittent freezing stopped immediately. Rohit’s team now has the diagnostic tools to see exactly who is accessing the server in real-time, ensuring no “stray” accounts ever slow down their business again.
Gunnar Eriksson (Sweden)
The Challenge: A software vendor told Gunnar he needed a total server upgrade to fix his app’s performance. Gunnar was skeptical and wanted a second opinion on whether the “slowness” was actually just a User Role and Permission Management issue.
The vorza360 Solution: We performed an independent assessment and found the server hardware was perfect. The “lag” was actually caused by poorly configured User Management Roles. Every time an employee opened the app, it was trying to verify hundreds of individual permission sets instead of using a streamlined “Role” model.
The Result: Gunnar avoided an unnecessary hardware purchase. We moved his team to a Role-Based Access system, and the “slowness” vanished. We gave him the evidence to show the vendor that the fix was in the settings, not the hardware.
Yetunde Adeyemi (Nigeria)
The Challenge: Yetunde’s server was years old and running slowly, but the company couldn’t afford a replacement. They needed to know if they could “clean up” their Professional User Permission Management to squeeze more life out of their current equipment.
The vorza360 Solution: We performed a “Permission Deep Clean.” We found that the server was bogged down by thousands of redundant permissions and “shared password” risks. We implemented Account Lockout & Password Policies to protect the server and moved all staff to unique, grouped accounts that use less “processing power” to verify.
The Result: The server felt “new” again. By optimizing how the server handles user identities and access requests, we extended the hardware’s useful life by two years, saving the company a significant capital expense.
vorza360’s Tech Edge
Local & Domain User Administration
NTFS Permission Structuring
Role-Based Access Control (RBAC)
+ 2
More
Privilege Delegation Models
Account Lockout & Password Policies
vorza360’s Tech Edge
Local & Domain User Administration
We handle the daily tasks of adding new team members and managing their digital IDs across your entire network.
NTFS Permission Structuring
Our team organizes your files so that sensitive folders stay private while shared folders remain easy for the right groups to access.
Role-Based Access Control (RBAC)
We set up user management roles and permissions based on job titles, ensuring your “Accounting” and “Sales” teams have exactly what they need.
Privilege Delegation Models
We give your managers the power to handle simple tasks without giving away “master” keys to your whole system.
Account Lockout & Password Policies
We build a digital shield that automatically blocks hackers who try to guess your passwords, keeping your user management permissions airtight.
Professional User Permission Management
We provide a hands-on service to oversee every “digital key” in your company, from simple logins to complex file access.
Advantages
- Organizing users into logical groups for faster and more accurate management.
- Creating unique user accounts for every staff member to prevent shared password risks.
- Regularly auditing your lists to remove old accounts from former employees.
- Providing a friendly partner to handle all your user permission management needs in easy words.
- Setting up "Standard" vs "Admin" levels to prevent accidental system changes.
Advanced User Role and Permission Management
We build a smart structure for your business software, ensuring your user management roles and permissions match your real-world team.
Advantages
- Designing clear "Roles" so new hires get the right access on their first day.
- Managing "Read-Only" vs "Full Edit" rights for your critical business files.
- Setting up timed access for temporary staff or contractors.
- Customizing your user role and permission management to follow your specific office rules.
- Delivering a managed service that grows and changes as your team does.
External User & Guest Access Support
We help you manage external users permission settings so you can collaborate with partners safely.
Advantages
- Creating secure "Guest" zones that keep your core business data hidden.
- Using specialized rules to manage external users Salesforce permission sets for your consultants.
- Setting up expiry dates for external keys so they turn off automatically when the job is done.
- Tracking exactly what external visitors do while they are inside your network.
- Providing expert guidance on how to manage users' permission for outside contractors.
Database & Technical Access Management
We act as your technical experts to manage user permission in Salesforce and other complex database platforms.
Advantages
- Configuring SQL management studio user permissions so your developers can work without breaking the database.
- Managing the background "Service Accounts" that your apps use to talk to each other.
- Setting up secure "tunnels" for remote tech support and maintenance.
- Providing a professional "Human-in-the-loop" to verify all high-level technical access.
- Ensuring that sensitive customer data is only visible to authorized managers.
Security & Compliance Auditing
Our team performs a deep review of your user management permissions to find and fix “access leaks.”
Advantages
- Finding folders that were accidentally left open to "Everyone" and locking them down.
- Testing your password rules to ensure they meet modern security standards.
- Providing a clear report on who has access to your most important files.
- Updating your user permission management to stay compliant with privacy laws.
- Offering an ongoing service to keep your permissions clean, lean, and secure.
Professional User Permission Management
We provide a hands-on service to oversee every “digital key” in your company, from simple logins to complex file access.
ADVANTAGES
- Creating unique user accounts for every staff member to prevent shared password risks.
- Organizing users into logical groups for faster and more accurate management.
- Regularly auditing your lists to remove old accounts from former employees.
- Setting up "Standard" vs "Admin" levels to prevent accidental system changes.
- Providing a friendly partner to handle all your user permission management needs in easy words.
Advanced User Role and Permission Management
We build a smart structure for your business software, ensuring your user management roles and permissions match your real-world team.
ADVANTAGES
- Designing clear "Roles" so new hires get the right access on their first day.
- Managing "Read-Only" vs "Full Edit" rights for your critical business files.
- Setting up timed access for temporary staff or contractors.
- Customizing your user role and permission management to follow your specific office rules.
- Delivering a managed service that grows and changes as your team does.
External User & Guest Access Support
We help you manage external users permission settings so you can collaborate with partners safely.
ADVANTAGES
- Creating secure "Guest" zones that keep your core business data hidden.
- Using specialized rules to manage external users Salesforce permission sets for your consultants.
- Setting up expiry dates for external keys so they turn off automatically when the job is done.
- Tracking exactly what external visitors do while they are inside your network.
- Providing expert guidance on how to manage users' permission for outside contractors.
Database & Technical Access Management
We act as your technical experts to manage user permission in Salesforce and other complex database platforms.
ADVANTAGES
- Configuring SQL management studio user permissions so your developers can work without breaking the database.
- Setting up secure "tunnels" for remote tech support and maintenance.
- Managing the background "Service Accounts" that your apps use to talk to each other.
- Ensuring that sensitive customer data is only visible to authorized managers.
- Providing a professional "Human-in-the-loop" to verify all high-level technical access.
Security & Compliance Auditing
Our team performs a deep review of your user management permissions to find and fix “access leaks.”
ADVANTAGES
- Finding folders that were accidentally left open to "Everyone" and locking them down.
- Testing your password rules to ensure they meet modern security standards.
- Providing a clear report on who has access to your most important files.
- Updating your user permission management to stay compliant with privacy laws.
- Offering an ongoing service to keep your permissions clean, lean, and secure.
Here is what our Clients are saying About us

Antti Korhonen (Finland)
Permissions across our Windows Server environment had accumulated into an unmanageable tangle, users with access they didn’t need, shared accounts, no clear ownership. vorza360 audited everything, restructured our permission model, and implemented a role-based approach that finally makes sense.
Sara Al-Mutawa (Kuwait)
vorza360 implemented a least-privilege permission model across our Windows Server file shares and applications. Every user now has exactly the access their role requires. The audit report we ran three months later showed zero excess permissions, a result we’d never have achieved with our previous ad-hoc approach.
Ionuț Dumitrescu (Romania)
We needed to onboard forty new staff quickly following an acquisition without compromising our permission structure. vorza360 set up a streamlined provisioning workflow using AD groups and role templates that got each new employee correctly configured in minutes. The ‘role-based onboarding’ they built saved days of manual work.
Rohit Malhotra (India)
After several departures from our IT team, nobody had a complete picture of who had access to what on our Windows Servers. vorza360 conducted a full permissions audit, produced a clear access matrix, removed everything unnecessary, and documented the approved permission model going forward.
Maja Andreasen (Denmark)
vorza360 implemented privileged access management on our Windows Server environment, separating standard user accounts from admin accounts, requiring explicit elevation for administrative tasks, and logging all privileged activity. Our security team finally has the visibility into admin actions they’d been asking for.
Chukwudi Eze (Nigeria)
vorza360 restructured the home folder and shared drive permissions on our Windows Server that had been allowing far too broad access for years. The ‘clean-permission-model’ they implemented means each team accesses only their data. Our data governance posture improved overnight.
More about Windows Server
Windows Server Installation & Setup
Get a rock-solid foundation for your business with vorza360’s professional Windows Server…
Active Directory & Group Policy
Take control of your office network with vorza360’s active directory and group policy…
Windows Firewall & Security Settings
Secure your business network with vorza360’s expert Windows firewall management.
Backup & Restore Solutions
Protect your business from data loss with vorza360’s professional backup and restore…
DNS & DHCP Configuration
Keep your office network fast and organized with vorza360’s professional dns and dhcp…
Hyper-V Virtualization
Maximize your hardware with vorza360’s expert hyper-V virtualization services. We help you…
+ 5
More
Remote Desktop Services Setup
Empower your team to work from anywhere with vorza360’s professional remote desktop…
Server Monitoring & Performance Tuning
Keep your business running at peak speed with vorza360’s server monitoring service.
Software Deployment & Patch Management
Keep your business secure and up-to-date with vorza360’s professional software…
More about Windows Server
Windows Server Installation & Setup
Active Directory & Group Policy
Windows Firewall & Security Settings
+ 12
More
Backup & Restore Solutions
DNS & DHCP Configuration
Hyper-V Virtualization
Remote Desktop Services Setup
Server Monitoring & Performance Tuning
Frequently Asked Questions
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
How does vorza360 manage Windows Server user accounts and permissions following security best practices?
User account and permission management on Windows Server is built on the principle of least privilege, every user and service account has only the access it needs to perform its function, and nothing more. vorza360 implements this through a structured approach: we create user accounts in Active Directory with appropriate group memberships that grant access to the specific resources each role requires. We use security groups (rather than assigning permissions directly to individual users) so that access changes as people join, leave, or change roles, the group membership changes, not the file system permissions. We implement a tiered administrative model where day-to-day work uses standard user accounts and privileged administrative tasks use separate administrator accounts accessed deliberately. We configure NTFS permissions on file shares using the principle of least access, verifying that inherited permissions align with intended access and removing any overly permissive inherited permissions.
How does vorza360 set up and manage shared folder permissions on Windows Server?
Shared folder permissions on Windows Server have two layers that must both be configured correctly: the Share permissions (which control access through the network share) and NTFS permissions (which control access at the file system level and apply both locally and through the network). vorza360 configures shared folder permissions using the recommended best practice of setting the Share permission to Full Control for the Authenticated Users group (or Everyone) and relying exclusively on NTFS permissions for granular access control. NTFS permissions are configured on the folder structure using security groups, a Read access group, a Read/Write access group, and a Modify access group, rather than individual users, ensuring that permission management scales with the organization. We disable inheritance on top-level shared folders and define explicit permissions, preventing unintended access propagation from parent directories.
How does vorza360 manage service accounts on Windows Server?
Service accounts are the identities under which Windows services and applications run, and they are frequently overlooked security risks, particularly when they are configured with excessive privileges or shared across multiple services. vorza360 manages service accounts using Microsoft’s Group Managed Service Accounts (gMSA) wherever possible, gMSAs have their passwords automatically managed by Active Directory (rotating every 30 days), eliminating the human management burden and the security risk of passwords being shared in documentation or reused. For applications that cannot use gMSAs, we create dedicated service accounts with strong passwords, minimum necessary privileges (typically local service rights or specific domain permissions rather than Domain Admin), and password change schedules. We audit all service accounts regularly to identify those that are no longer needed, have accumulated excessive privileges over time, or are using stale credentials.
How does vorza360 audit and review Windows Server user permissions?
Permission audits are essential for maintaining access hygiene as organizations grow and change, over time, users accumulate access rights from previous roles, and folders that were once restricted become accessible through permission inheritance or group membership changes. vorza360 conducts periodic permission audits using a combination of Active Directory reports (group memberships, user accounts, and their associated privileges), file system permission exports using PowerShell to enumerate NTFS permissions across shared directories, and review of local groups (especially the Administrators group) on all servers. We identify and remediate common permission issues: users with excessive rights accumulated from previous roles (stale access), service accounts with Domain Admin or other unnecessary elevated privileges, shared folders accessible by Everyone or Authenticated Users without business justification, and local administrator group memberships not controlled through Group Policy. We present audit findings in a clear report and implement remediation with your approval.
How does vorza360 handle user provisioning and deprovisioning in a Windows Server environment?
Efficient user provisioning and deprovisioning processes are both a security requirement and an operational necessity. Stale accounts from employees who have left the organization are one of the most commonly exploited attack vectors in real-world security incidents. vorza360 implements user lifecycle management processes for Windows environments: for provisioning, we create user accounts from a standardized template that assigns appropriate group memberships based on department and role, ensuring users have the correct access on their first day. For deprovisioning, we implement an immediate-action procedure for account disabling when a user leaves, we disable the account (not delete, to preserve audit history), remove them from all security groups immediately, log them out of active sessions, and change passwords on any shared accounts the user had access to. For clients without a formal HR-to-IT notification process, we provide a monthly Joiners-Movers-Leavers (JML) review service that audits AD accounts against current employee records.