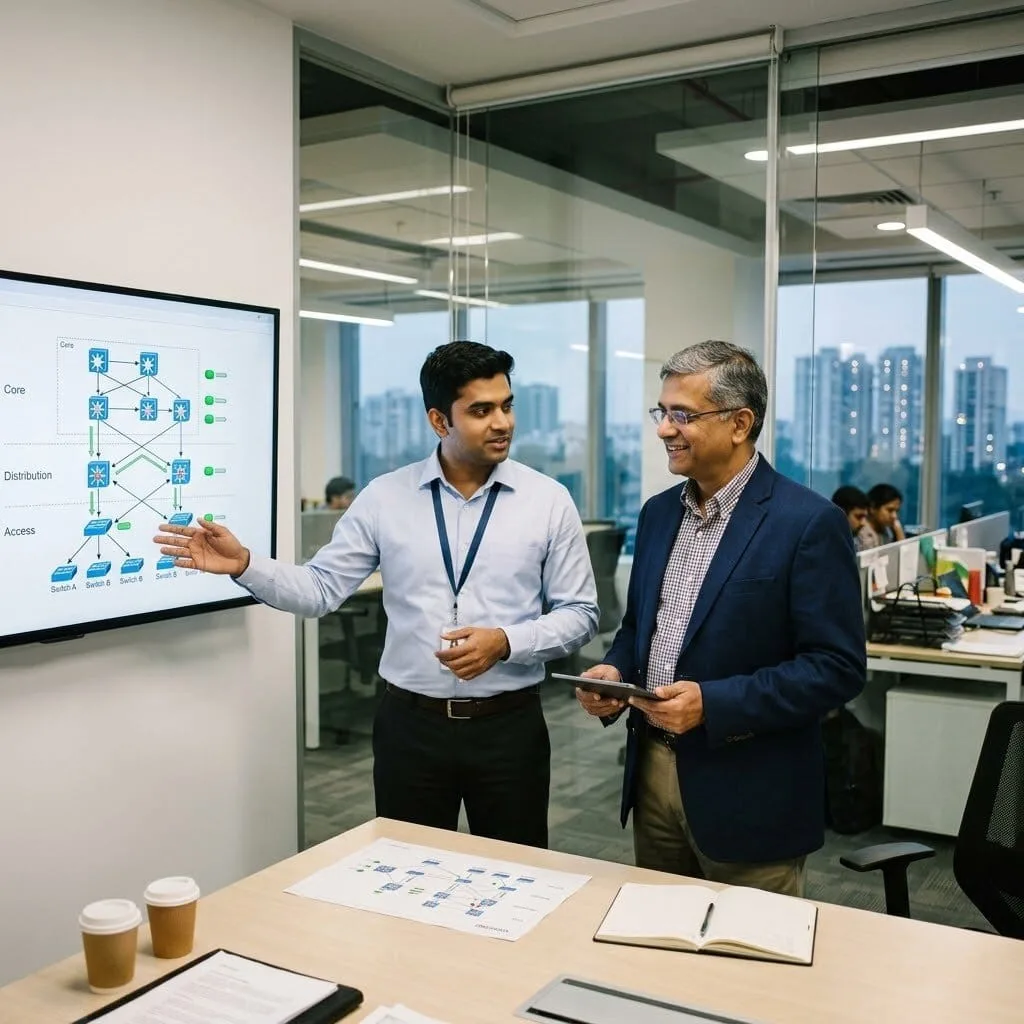
Keep your office devices connected and organized with vorza360’s professional Cisco switch setup. We provide expert management to ensure your data flows smoothly and your network stays secure.
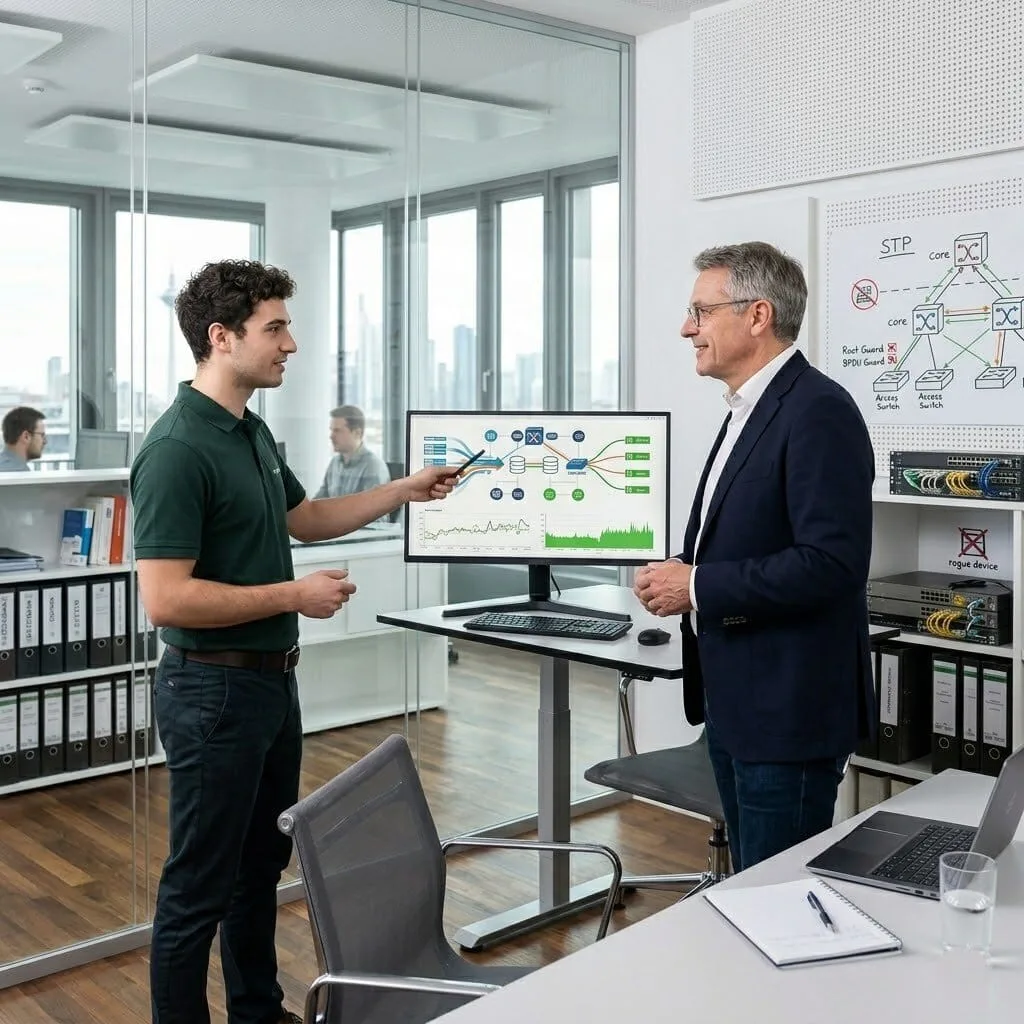
The Challenge: Hans’s company was experiencing intermittent network outages that had been traced to spanning tree topology changes but the root cause couldn’t be identified. The outages lasted 30-60 seconds and occurred several times per week, affecting productivity across the entire office.
The vorza360 Solution: vorza360 analysed the spanning tree topology, identified that automatic configuration had placed the spanning tree root on an access switch rather than the core, and that a rogue device on the network was occasionally sending BPDUs that triggered topology changes. Root bridge configuration was corrected, BPDU guard was enabled on access ports, and Root Guard was configured on uplink ports.
The Result: The intermittent outages stopped completely after the spanning tree corrections were applied. Hans’s team had an explanation for the months-long problem and a correctly configured spanning tree topology that was resilient to the rogue device events that had previously been causing the disruptions.
Fatima Al-Hamdan (Saudi Arabia)
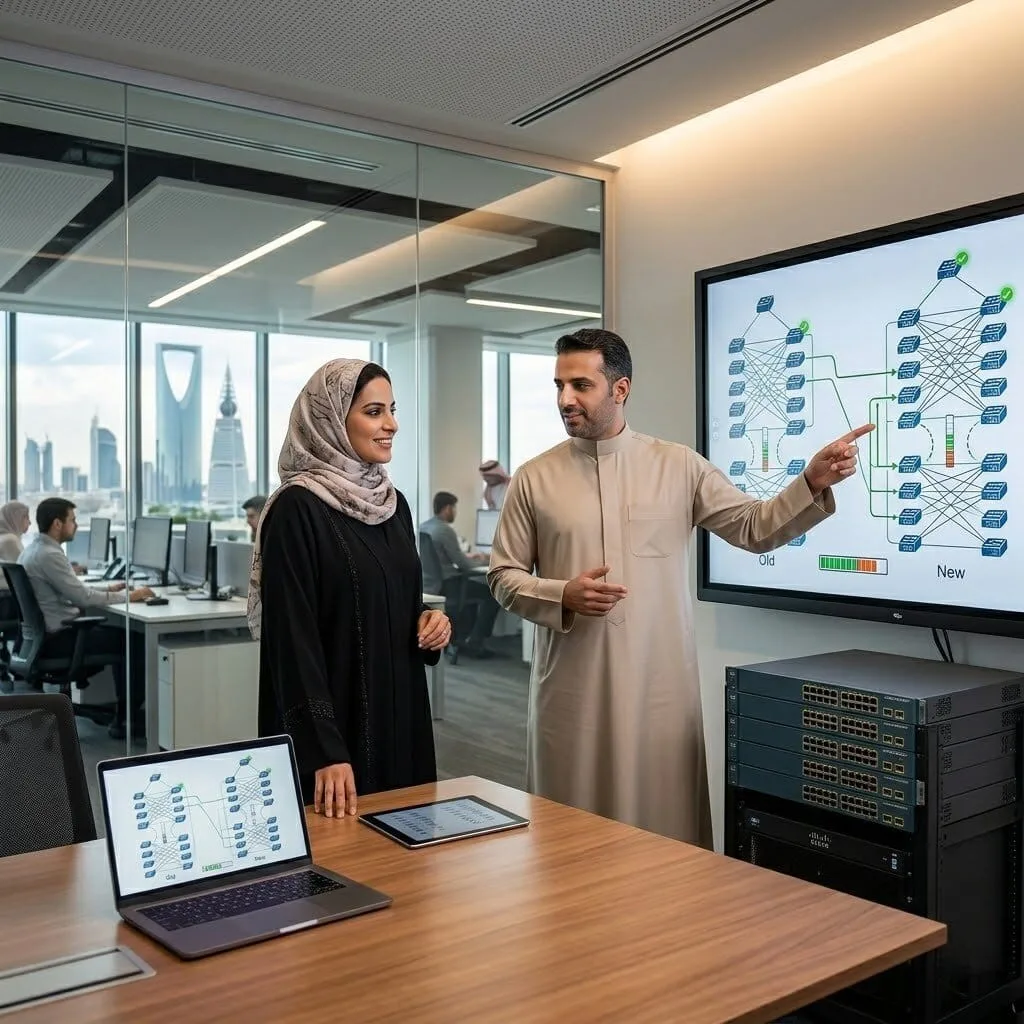
The Challenge: Fatima’s company was migrating to a new data centre and needed to migrate 40 Cisco Catalyst switches worth of VLANs, port configurations, and routing to the new environment without disrupting their production systems during business hours.
The vorza360 Solution: vorza360 planned the migration with a parallel-run approach: the new switch stack was configured and tested in parallel with production, each workload was migrated segment by segment in planned maintenance Windows, and rollback configurations were maintained for each migration step until the new environment was validated.
The Result: The 40-switch migration was completed across eight planned maintenance Windows with zero unplanned downtime. Fatima’s IT team managed the most complex network migration their organisation had undertaken, supported by the methodical approach and per-step rollback plans that vorza360 brought to the engagement.
Radu Marin (Romania)
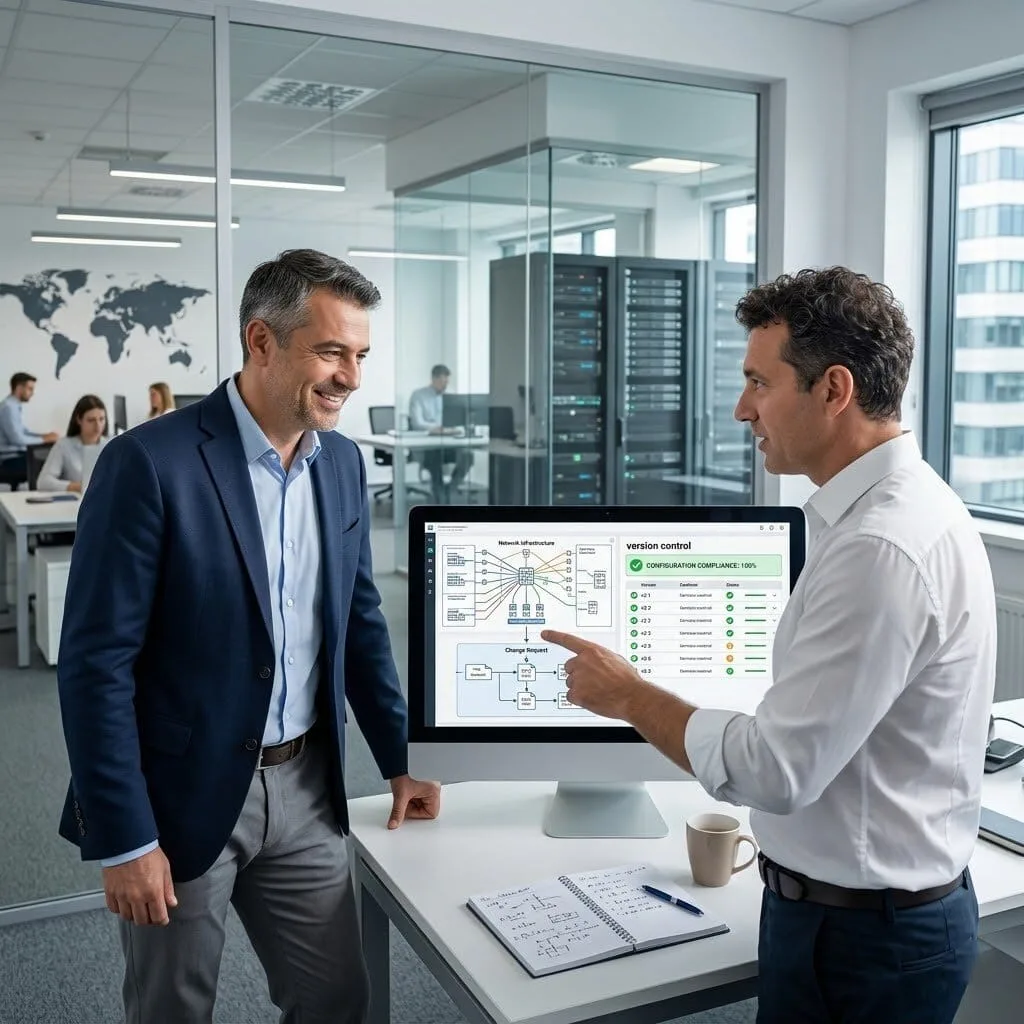
The Challenge: Radu’s company had a Cisco Nexus data centre fabric that their team managed reactively, changes were made as needed, no change management process, and the running configuration had diverged significantly from any documented baseline. A planned audit had flagged this as a critical governance gap.
The vorza360 Solution: vorza360 performed a full configuration audit of the Nexus environment, documented the current state, identified every deviation from intended configuration, and implemented a configuration management process: baseline configurations version-controlled, a change management workflow for all future changes, and automated compliance checking against the baseline.
The Result: The audit gap was resolved. Radu’s team had a documented baseline and a change management process that meant future changes were tracked and intentional. The configuration drift that had accumulated over years was addressed, and the automated compliance checking meant drift would be detected immediately rather than accumulating again.
Arjun Bose (India)
The Challenge: Arjun’s company needed to upgrade their Cisco Catalyst campus switches from an end-of-support platform to current hardware. The upgrade affected 25 switches across three buildings and needed to be executed without disrupting their operations that ran during extended business hours.
The vorza360 Solution: vorza360 planned a rolling upgrade: one building at a time, each switch pre-staged with the production configuration before the maintenance window, with the physical swap taking under 20 minutes per switch. Inter-building uplinks were maintained throughout by migrating access switches first and distribution switches last.
The Result: The 25-switch upgrade was completed across three weekends with no business-hours disruption. Arjun’s team decommissioned their end-of-support hardware on schedule and had full manufacturer support for the new platform. The pre-staging approach meant each maintenance window was used efficiently with minimal risk.
Erik Petersen (Norway)
The Challenge: Erik’s company was moving to a leaf-spine Cisco Nexus data centre fabric for their VMware environment but had only managed traditional three-tier campus networks. The team understood the concept of leaf-spine but had no hands-on experience implementing it.
The vorza360 Solution: vorza360 designed and implemented the Nexus leaf-spine fabric with vPC for host-facing connections, BGP EVPN for the overlay, and VXLAN for workload mobility. The implementation included a knowledge transfer programme so Erik’s team could operate the new architecture independently.
The Result: The VMware environment migrated to the new fabric with the east-west throughput and workload mobility the virtualisation team needed. Erik’s network engineers had the hands-on experience and documentation from the knowledge transfer that let them operate the new architecture confidently from day one.
Chidi Okonkwo (Nigeria)
The Challenge: Chidi’s company had a Cisco Catalyst campus network where a configuration error had created a broadcast domain so large that broadcast traffic was consuming 40% of available network capacity. Users on the network experienced constant slowness but the cause had been misidentified as insufficient bandwidth.
The vorza360 Solution: vorza360 performed network traffic analysis, identified the excessive broadcast traffic, traced it to a VLAN design where all 300 devices were in a single broadcast domain, and redesigned the VLAN structure to segment the network appropriately. The reconfiguration was implemented during a planned maintenance window.
The Result: Broadcast traffic dropped from 40% to under 5% of network capacity after the VLAN redesign. The network performance improvement was immediately noticeable to users, the slowness that had been attributed to insufficient bandwidth was resolved entirely through correct VLAN design. Chidi’s team avoided an unnecessary bandwidth upgrade.
The Silent Engine of Your Office
Every device in your office, from computers and printers to security cameras relies on a switch to talk to the rest of the network. A Cisco managed switch acts like a high-speed traffic controller, making sure that data gets to the right place without any collisions. Without a proper setup, your network can become messy and slow, leading to dropped connections and frustrating delays during your busy workday.
At vorza360, we provide a managed service that takes the guesswork out of your hardware. We don’t just plug things in; we carefully setup Cisco switch rules that prioritize your most important tasks. By creating an organized environment, we help your business stay productive. Our team handles all the technical details behind the scenes, so your staff can enjoy a fast, reliable connection that just works every time they log in.
vorza360’s Tech Edge
Cisco Catalyst Switch Series
Layer 2 & Layer 3 Switching
Port Security Configuration
+ 2
More
Spanning Tree Protocol (STP)
Switch StackWise Technology
vorza360’s Tech Edge
Cisco Catalyst Switch Series
We deploy industry-leading hardware known for its incredible speed and “always-on” reliability.
Layer 2 & Layer 3 Switching
Our team handles both basic device connections and advanced routing right inside the switch for lightning-fast performance.
Port Security Configuration
We lock down the physical plugs in your office, ensuring only approved company devices can join the network.
Spanning Tree Protocol (STP)
We configure “loop protection” to prevent accidental network crashes caused by incorrect cabling.
Switch StackWise Technology
We can link multiple switches together so they act as one giant, powerful unit that is easy for us to manage for you.
Tools
Tools & Plugins We Use
Cisco DNA Center
A powerful dashboard we use for centralized Cisco switch management software and automated updates.
Cisco Network Assistant (CNA)
A specialized tool we use to setup Cisco switch layouts and monitor your device health.
PuTTY / Tera Term
Professional utilities our team uses for a secure Cisco switch SSH setup during remote maintenance.
Cisco Prime Infrastructure
A high-level plugin used for deep-level Cisco switch management across large office buildings.
Here is what our Clients are saying About us
Einar Sigurdsson (Iceland)
Our Cisco switch stack had grown over the years with no consistent configuration standards applied. vorza360 audited every switch, standardised the configurations, cleaned up unused ports, and documented the entire layer two topology. Managing our switching infrastructure has been significantly simpler since.
Rasha Al-Khalidi (Jordan)
vorza360 deployed and configured Cisco switches for our new office build-out, stacking, uplinks, port configurations, and spanning tree all set up correctly before we moved in. We had a fully working switched network on day one without a single port configuration issue to chase down.
Ondřej Blažek (Czech Republic)
We’d been having intermittent connectivity issues that turned out to be a spanning tree misconfiguration causing occasional topology changes. vorza360 diagnosed the problem, reconfigured spanning tree properly across our Cisco switch estate, and the instability we’d been tolerating for months disappeared completely.
Priya Venkatesh (India)
vorza360 configured port security on our Cisco switches to prevent unauthorised devices from connecting to our network. The ‘only-known-devices’ policy they implemented across our access layer has become a core part of our network security posture that our security team has been pushing for since last year.
Kristoffer Lund (Norway)
vorza360 managed a complete Cisco switch refresh for us, configuring the new hardware, migrating all port configurations, and cutting over during a maintenance window without any extended downtime. The cutover plan they prepared was meticulous and the execution matched it.
Adaugo Okafor (Nigeria)
vorza360 set up SNMP monitoring and syslog forwarding on all our Cisco switches so our network management platform has full visibility into switch health and events. We’d been operating blind before, now switch issues show up in our monitoring before users notice anything.
More about Cisco IT Service
Cisco Router Configuration
Build a rock-solid business foundation with vorza360’s professional Cisco router…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What does vorza360's Cisco switch setup and management service cover?
Our Cisco switch setup and management service covers the complete configuration and ongoing administration of Cisco Catalyst switches (the standard for enterprise access and distribution layer switching) and Cisco Nexus switches (for data center environments). Services include initial switch deployment and IOS configuration, VLAN creation and port assignment, trunk port configuration between switches and routers, Spanning Tree Protocol configuration and optimization, PortFast and BPDU Guard configuration for access ports, 802.1X port security and MAC address filtering, inter-VLAN routing configuration on Layer 3 switches, switch stacking configuration, SNMP and Syslog monitoring setup, PoE budget management for IP phones and wireless access points, port channel and EtherChannel configuration for link aggregation, and documentation of the switch configuration and topology. We manage all of this from a clear understanding of how your network is used, not just how it is built.
How does vorza360 configure Spanning Tree Protocol (STP) on Cisco switches to prevent network loops?
Spanning Tree Protocol is the mechanism that prevents broadcast storms caused by loops in switched networks, a network loop without STP will bring down the entire network within seconds as broadcasts circulate indefinitely. vorza360 configures STP on Cisco switches using Rapid PVST+ (Rapid Per-VLAN Spanning Tree Plus) as the standard, it provides fast convergence (seconds rather than minutes for IEEE 802.1D) while maintaining per-VLAN topology control. We explicitly configure the root bridge for each VLAN by setting the bridge priority on the intended root switch rather than relying on default priority values that could result in an unpredictable device becoming root. We configure PortFast on all access ports connected to end-user devices, allowing them to immediately transition to forwarding state without waiting for STP convergence. We enable BPDU Guard on PortFast-enabled ports to immediately disable any port that receives a BPDU, preventing rogue switches from being connected to access ports.
How does vorza360 configure Cisco switch port security to prevent unauthorized device connections?
Switch port security prevents unauthorized devices from connecting to your network by controlling which MAC addresses are permitted on each port. vorza360 implements Cisco switch port security appropriate to your environment: on access ports connected to fixed workstations, we configure MAC address-based port security with a maximum of one allowed MAC address and sticky MAC learning (the switch learns the connected device’s MAC address automatically and saves it in the running config), configured to shut down the port if a different device is connected. For environments using 802.1X, we configure the switch for RADIUS-based authentication that requires every device to present valid credentials before the port transitions to an authorized state, providing identity-based access control rather than just MAC filtering. We also enable DHCP Snooping (which prevents rogue DHCP servers), Dynamic ARP Inspection (which prevents ARP poisoning attacks), and IP Source Guard (which prevents IP spoofing) as the full Layer 2 security suite.
How does vorza360 manage Cisco switch stacking for simplified administration?
Cisco switch stacking (using StackWise or StackWise-480 technology on Catalyst switches) allows multiple physical switches to operate as a single logical unit, managed with one IP address, one configuration, and one management session. This dramatically simplifies administration for organizations with multiple switches in the same location. vorza360 configures Cisco switch stacks by connecting the stack members via StackWise cables, configuring the master switch election (determining which physical switch acts as the active master), verifying that all stack members are running the same IOS version, configuring the stack-wide management IP address and VLAN, and implementing renumbering of stack member switch numbers to reflect their physical position for consistent port identification. We configure NSF/SSO (Non-Stop Forwarding/Stateful Switchover) where supported so that if the active master switch fails, the standby immediately takes over without dropping network connections.
How does vorza360 configure EtherChannel on Cisco switches for link aggregation?
EtherChannel (Link Aggregation Control Protocol, LACP, or Port Aggregation Protocol, PAgP) allows multiple physical network interfaces between two devices to be bundled into a single logical link, providing both increased bandwidth and redundancy. vorza360 configures EtherChannel on Cisco switches for high-bandwidth uplinks between access and distribution layer switches, between switches and servers (particularly for storage and virtualization workloads), and between switches and the core router. We use LACP (the IEEE standard protocol) as the negotiation protocol for EtherChannel configuration, specifying the port channel interface number, configuring the member physical interfaces with the appropriate channel-group command and LACP active mode, verifying that all member interfaces have matching speed, duplex, VLAN membership, and trunk configuration settings (a mismatch on any of these will prevent the EtherChannel from forming), and validating the bundle using show etherchannel summary to confirm all member links are in the bundled state.