Protect your business with vorza360’s expert Cisco firewall security policy services. We build digital shields and smart rules that block threats while keeping your office data moving fast and safely.
The Challenge: Dieter’s company had a Cisco ASA firewall that had been configured years ago with rules that had accumulated without any cleanup. The rule set had grown to over 400 ACL entries, many of which were redundant, contradictory, or permitted traffic that no longer needed to be allowed. A security audit had flagged the rule bloat as a risk.
The vorza360 Solution: vorza360 performed a full ASA rule review, identifying shadowed rules, redundant permits, and access rules that permitted overly broad traffic. The rule set was rationalised from 400 entries to 180 active, documented rules, each with a business justification. The cleanup was staged with testing at each phase to ensure no legitimate traffic was disrupted.
The Result: The ASA rule base was reduced by over 55% without disrupting any legitimate business traffic. Dieter’s security team had a clean, documented rule set where every entry had a documented purpose, and the ongoing change management process vorza360 established meant future rules would be added with justification and reviewed for cleanup regularly.
Sara Al-Zahrani (Kuwait)
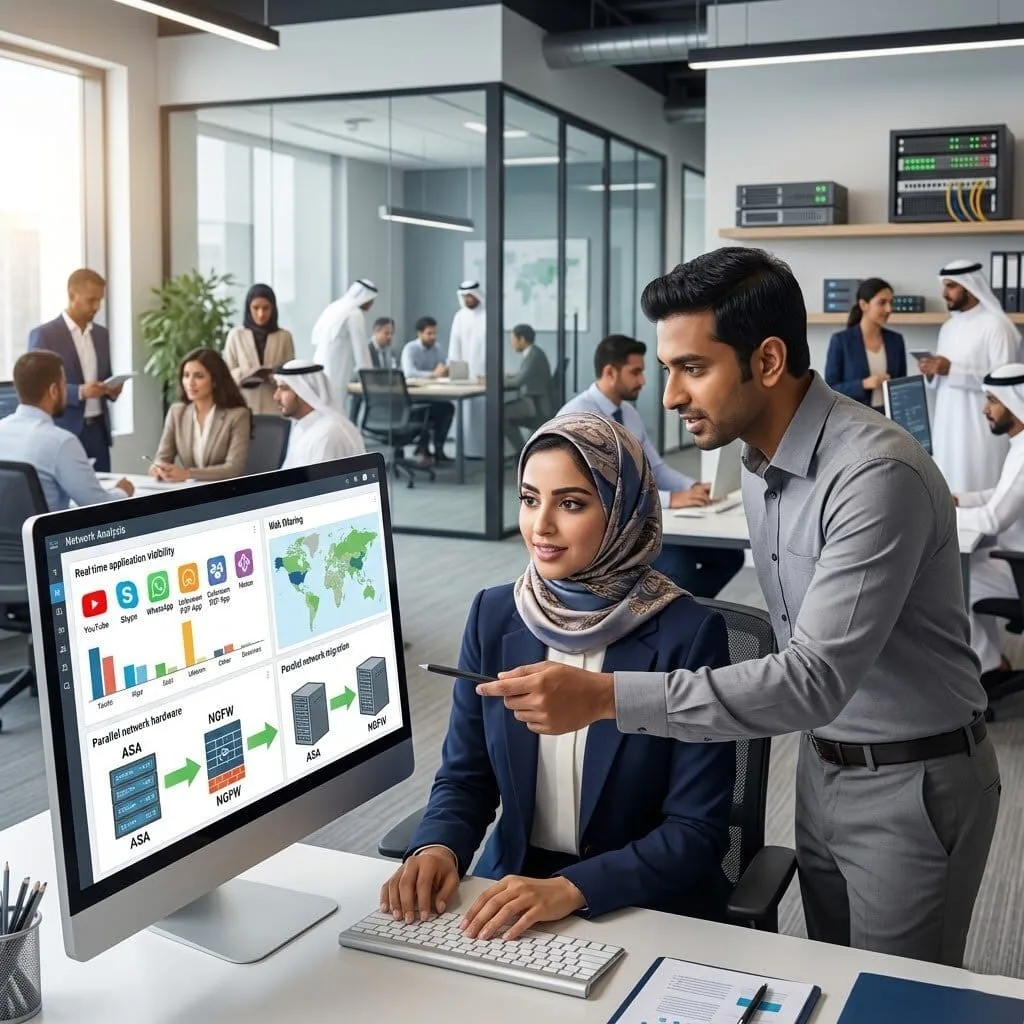
The Challenge: Sara’s company was migrating from Cisco ASA to Cisco Firepower NGFW and needed the migration to preserve all existing security policy while enabling the application visibility and URL filtering capabilities that were the justification for the upgrade. Their team had deep ASA expertise but no Firepower experience.
The vorza360 Solution: vorza360 managed the migration with a parallel-run approach: Firepower deployed alongside the ASA, security policy migrated and validated in the new platform, application control and URL filtering policies configured for their requirements, and the cutover executed with the ASA kept in place as an immediate fallback.
The Result: The Firepower migration completed without any security policy gaps or disruption to business traffic. Sara’s team had hands-on Firepower experience from working alongside vorza360 during the migration, and the application visibility the new platform provided immediately surfaced several applications operating on the network that management had not been aware of.
Marius Dumitrescu (Romania)
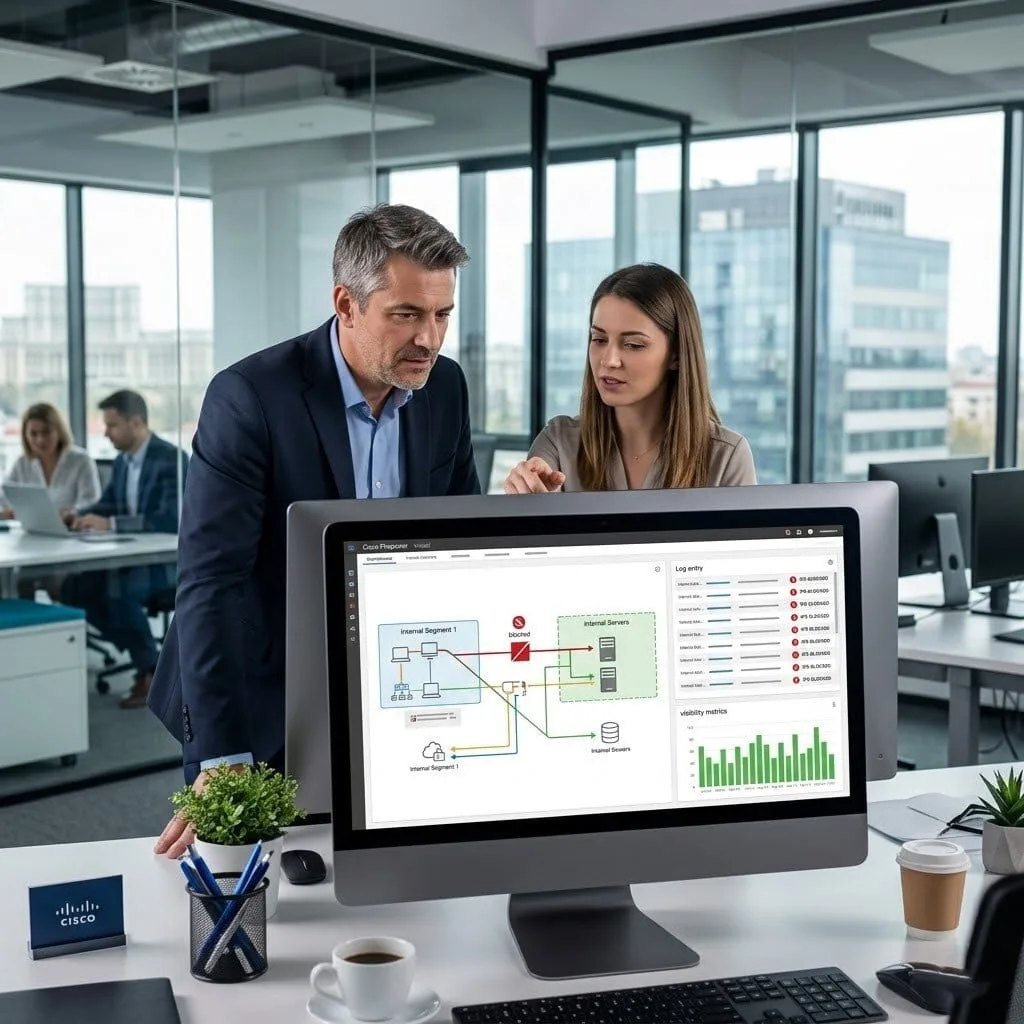
The Challenge: Marius’s company had experienced a security incident where an attacker had exploited a vulnerability in their web application server and used it as a pivot point to reach internal systems. The ASA perimeter firewall hadn’t stopped the lateral movement because there was no inspection between internal segments.
The vorza360 Solution: vorza360 implemented Cisco Firepower as an internal segmentation firewall between network zones, enabling application-layer inspection of east-west traffic that the perimeter-only model had left unprotected. IPS signatures were tuned for their internal traffic patterns, and a security intelligence feed was enabled to block known malicious destinations.
The Result: The internal segmentation prevented the lateral movement vector that had been exploited in the incident. Marius’s security team had visibility into east-west traffic for the first time and could see application-layer traffic between network segments. The IPS caught and blocked several subsequent scanning attempts that would have gone undetected with the previous perimeter-only model.
Anand Sharma (India)
The Challenge: Anand’s company needed to implement SSL inspection on their Cisco Firepower to detect malware hiding in encrypted traffic. Their security policy required inspection but the SSL decryption configuration was technically complex, and a misconfiguration had the potential to break legitimate encrypted business traffic.
The vorza360 Solution: vorza360 configured SSL decryption with a careful exemption list: internal trusted applications, financial sites, and categories where decryption would violate privacy or regulation were explicitly bypassed, while general HTTPS traffic was decrypted for inspection. The configuration was tested in monitor-only mode first before enforcement was enabled.
The Result: SSL inspection was enabled without breaking any legitimate business application. Anand’s security team immediately began seeing threat intelligence in previously opaque encrypted traffic, and the monitor-only testing phase had caught the specific exemptions that would have caused problems if enforcement had been enabled directly.
Mikael Svensson (Sweden)
The Challenge: Mikael’s company had a Cisco ASA managing VPN access for their remote workforce, but the configuration had been built for 20 remote users and now needed to support 200. Authentication was falling back to local accounts rather than Active Directory because the RADIUS configuration had broken during a software upgrade and nobody had noticed.
The vorza360 Solution: vorza360 repaired the RADIUS authentication integration with Active Directory, migrated VPN authentication to SAML with their Azure AD as the identity provider enabling MFA for all VPN sessions, and reconfigured the VPN pool and split-tunnelling policies appropriate for 200 concurrent users.
The Result: VPN authentication was restored to Active Directory, aligned with the access management controls Mikael’s team expected, and MFA was applied to every VPN session for the first time. The capacity configuration supported their 200-user requirement, and the SAML integration simplified authentication management by eliminating the separate VPN credential management that had existed before.
Ngozi Okafor (Nigeria)
The Challenge: Ngozi’s company needed their Cisco ASA configured for site-to-site VPN connectivity with three partner organisations who each had different firewall vendors. The multi-vendor aspect of the VPN configuration had stalled their team, every attempt had ended with one partner’s VPN working and another breaking.
The vorza360 Solution: vorza360 worked through each site-to-site VPN individually, coordinating with each partner’s technical team to agree on compatible IKEv2 parameters, implemented the VPN tunnels in a tested sequence, and diagnosed the interoperability issues that had been causing the stalls, primarily IKE proposal mismatches that were vendor-specific in their default configurations.
The Result: All three site-to-site VPNs were operational simultaneously for the first time. Ngozi’s team had a working multi-vendor VPN configuration and understood the IKE parameter compatibility requirements that had been causing the interoperability failures. The documentation produced covered all three tunnel configurations for future reference.
vorza360’s Tech Edge
Cisco ASA & Firepower Firewalls
Stateful Packet Inspection
Security Zones & Policies
+ 2
More
Intrusion Prevention System (IPS)
Threat Defense Configuration
vorza360’s Tech Edge
Cisco ASA & Firepower Firewalls
We deploy industry-leading hardware that stops modern threats like ransomware before they reach your computers.
Stateful Packet Inspection
Our team ensures your firewall doesn’t just block traffic, but “remembers” safe connections to keep your work flowing smoothly.
Security Zones & Policies
We create Cisco data security policies that divide your network into secure “neighborhoods,” preventing hackers from moving between devices.
Intrusion Prevention System (IPS)
We configure a 24/7 digital guard that automatically identifies and shuts down suspicious behavior in real-time.
Threat Defense Configuration
We use the latest Cisco security policy builder techniques to ensure your defense is always one step ahead of hackers.
How we do it
We provide a managed service that locks down your network using professional Cisco security standards.
Creative Approaches
We use “Trust-Based Zones” to simplify your defense. Using a zone based policy firewall Cisco approach, we group your office into areas like “Private” and “Guest,” ensuring your sensitive files stay shielded from the outside world.
Insightful Strategies
Our strategy focuses on “Intelligent Routing.” We provide Cisco firewall policy based routing that sends your critical work through the safest paths, separating high-risk web traffic from your sensitive business data.
Tailored Solutions
We build “digital checkpoints” that match your specific needs. From a Cisco ASA firewall policy for small offices to full Cisco network security policy management for large companies, we tailor our service to your data’s sensitivity.
Creative Approaches
We use “Trust-Based Zones” to simplify your defense. Using a zone based policy firewall Cisco approach, we group your office into areas like “Private” and “Guest,” ensuring your sensitive files stay shielded from the outside world.
Insightful Strategies
Our strategy focuses on “Intelligent Routing.” We provide Cisco firewall policy based routing that sends your critical work through the safest paths, separating high-risk web traffic from your sensitive business data.
Tailored Solutions
We build “digital checkpoints” that match your specific needs. From a Cisco ASA firewall policy for small offices to full Cisco network security policy management for large companies, we tailor our service to your data’s sensitivity.
Our Service Cycle
vorza360 follows a professional, simple path to secure your business airwaves.
Step 1
Safety Audit
Step 2
Interface Setup
Step 3
Policy Building
Step 4
Zone Lockdown
Step 5
Path Optimization
Step 6
Partner Care
Step 1
Safety Audit
We review your current Cisco security policy to find gaps or old rules that need fixing.
Step 2
Interface Setup
Our team configures the Cisco secure firewall security policy configuration interface for peak efficiency.
Step 3
Policy Building
We use a Cisco security policy builder approach to create custom rules that only allow approved work traffic.
Step 4
Zone Lockdown
We implement a zone based policy firewall Cisco setup to isolate your guest Wi-Fi from your private servers.
Step 5
Path Optimization
We perform Cisco firewall policy based routing to ensure your most secure apps get the fastest speeds.
Step 6
Partner Care
vorza360 provides ongoing Cisco firewall policy managementupdating your defenses every day as new threats appear.
Why Choose vorza360 for This Service?
Security shouldn’t be a headache. We provide the expertise so you can focus on your business goals.
Advanced Policy Enforcement
We use Cisco secure firewall security management policy enforcement capabilities to ensure your rules are followed perfectly. This means your “digital locks” stay locked, and your company data stays where it belongs.
Centralized Management
Forget confusing settings on every device. We provide professional Cisco firewall policy management from a central dashboard, allowing us to update your entire office security with a single click.
Human-First Support
We take the “scary” out of cybersecurity. We explain your Cisco firewall policy in very easy words and act as your dedicated IT partner, ensuring your team stays safe without being slowed down.
Here is what our Clients are saying About us
Anni Korhonen (Finland)
Our Cisco ASA firewall had accumulated years of rule additions with no cleanup and no documentation. vorza360 audited the entire rule set, removed redundant and shadowed rules, reorganised the policy logically, and documented every rule that remained. Our firewall is now something we understand and can maintain confidently.
Walid Al-Sayed (Egypt)
vorza360 migrated our ageing Cisco ASA to a new Firepower platform and rebuilt the security policies from scratch using the opportunity to clean up years of rule accumulation. The new policies are tighter, better documented, and actually enforce what our security policy says they should.
Mihai Constantin (Romania)
After a security incident exposed gaps in our perimeter defences, we brought in vorza360 to review and tighten our Cisco firewall policies. They found several rules that were far too permissive and had been there since initial deployment. Every gap was closed with a clear explanation of what it had been allowing.
Suresh Kumar (India)
vorza360 implemented application-aware firewall policies on our Cisco Firepower that go beyond port-based rules to control traffic based on application identity. The ‘know-what-you-allow’ approach they brought to our firewall policies has significantly improved our security visibility and control.
Anders Petersen (Denmark)
vorza360 configured zone-based security policies on our Cisco firewall that properly separate our internal segments, DMZ, and external networks with appropriate access rules between each zone. The ‘zones-not-interfaces’ model they implemented is more intuitive to manage and more secure than our previous flat policy.
Yetunde Adeyemi (Nigeria)
vorza360 configured Cisco Firepower IPS policies for our environment that detect and block known threat signatures without generating excessive false positives. Finding the right balance between security and operational impact took expertise we didn’t have internally, vorza360 got it right and tuned it carefully.
More about Cisco IT Service
Cisco Router Configuration
Build a rock-solid business foundation with vorza360’s professional Cisco router…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What Cisco firewall platforms does vorza360 work with and how do they differ?
vorza360 works with Cisco’s two primary firewall platforms, each suited to different security requirements. The Cisco ASA (Adaptive Security Appliance) is a mature, widely deployed stateful firewall that provides reliable traffic filtering, VPN termination, and basic intrusion prevention. It is appropriate for organizations that need robust firewall capabilities without the overhead of advanced threat intelligence features. Cisco Firepower (now Cisco Secure Firewall, combining ASA with the Firepower Threat Defense software) is the next-generation platform that adds advanced threat detection including application-aware inspection, URL filtering, malware sandboxing via integration with Cisco Threat Grid, and Intrusion Prevention System (IPS) capabilities powered by Cisco Talos threat intelligence. vorza360 recommends Firepower for organizations facing sophisticated threats, operating in regulated industries, or requiring detailed application-level visibility and control. We configure both platforms to their full capability based on your security requirements.
How does vorza360 implement zone-based security policies on Cisco firewalls?
Zone-based firewall policies divide the network into logical security zones, Inside (trusted internal network), Outside (untrusted internet), DMZ (semi-trusted zone for externally accessible servers), and optionally Guest and Management zones, and define explicit policies for traffic between each pair of zones. This architecture is more secure than traditional interface-based filtering because it requires a policy to be explicitly written for each traffic direction; traffic between zones is denied by default unless explicitly permitted. vorza360 implements zone-based policies on Cisco ASA and Firepower by creating security zone objects, defining interface-to-zone assignments, and writing access policies using Cisco’s Modular Policy Framework (for ASA) or the Firepower Management Center’s access control policy engine. We implement the principle of least-privilege for each zone pair, permitting only the specific application protocols, destination ports, and source addresses required for legitimate business traffic, blocking everything else by default.
How does vorza360 configure Cisco Firepower IPS to detect and block network threats?
Cisco Firepower’s Intrusion Prevention System (IPS) analyzes network traffic in real time against a continuously updated library of attack signatures and behavioral indicators provided by Cisco Talos, one of the world’s largest commercial threat intelligence teams. vorza360 configures Cisco Firepower IPS by creating an intrusion policy based on Cisco’s recommended balanced security/connectivity policy template (which provides strong protection with minimal false positives for typical business traffic) and applying it to the relevant traffic flows in the access control policy. We configure the intrusion event logging and alerting to notify our monitoring team when high or critical severity events are detected. We tune the policy for your specific environment, suppressing known false-positive rules for applications you use, enabling specific rules for technologies you run, to improve detection accuracy. We review intrusion event reports regularly to identify attack patterns targeting your network and adjust policies accordingly.
How does vorza360 implement Cisco firewall ACLs for granular traffic control?
Access Control Lists (ACLs) on Cisco ASA and Firepower firewalls provide granular control over which traffic is permitted or denied between network segments. vorza360 implements Cisco firewall ACLs using a structured, documented approach: we define permit rules only for the specific traffic flows with legitimate business justification, specifying the source network or host, destination network or host, protocol, and destination port(s), and rely on the implicit deny-all at the end of each ACL to block everything not explicitly permitted. We use named ACLs with descriptive names (not generic names like INBOUND-ACL) that identify the purpose of the ACL. We add inline comments using the remark keyword to explain the business justification for each rule, making future reviews and audits straightforward. We order ACL entries correctly, placing more specific rules before less specific ones and the most frequently matched rules early in the list for performance. We review and validate ACL rules regularly to remove rules that are no longer justified.
How does vorza360 manage Cisco firewall security policies as the business evolves?
Cisco firewall policies accumulate technical debt over time, rules are added as new requirements arise but rarely removed when those requirements end, resulting in an increasingly complex and difficult-to-audit policy. vorza360 manages Cisco firewall policy evolution through a structured change management approach: all policy changes are documented with a business justification, the name of the requestor, the date implemented, and the expected review date. We conduct quarterly firewall policy reviews that use Cisco Firepower’s built-in hit count logging to identify rules that have had zero hits in the review period, candidates for removal if the traffic they permitted no longer exists. We test all new rule additions in a controlled way, adding the rule and monitoring logs to confirm it permits the intended traffic before treating it as validated. We use Cisco Firepower Management Center’s policy comparison tool to compare configurations across maintenance Windows and verify that only intended changes were made.