Protect your business data and stay audit-ready with vorza360’s expert Azure security and compliance services. We provide a managed digital fortress that keeps you safe and follows all industry rules.
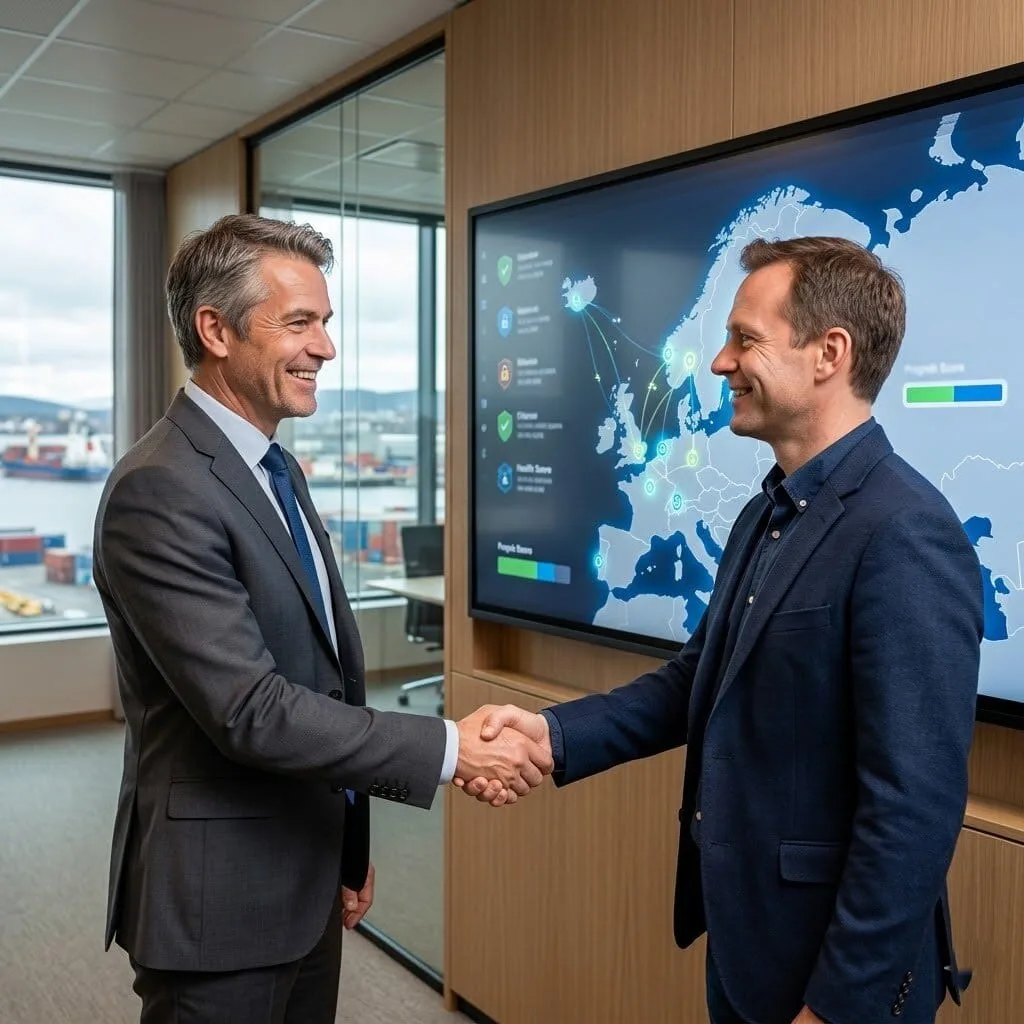
The Challenge Arvid runs a high-tech maritime logistics firm in Oslo. With strict European data laws and massive shipping contracts on the line, he was losing sleep over his “digital reputation.” He knew his cloud setup needed to be iron-clad, but the technical jargon of GDPR and ISO audits felt like a foreign language. He didn’t just need a software fix; he needed a “digital fortress” that would prove to his global partners that their data was in safe hands.
The vorza360 Solution We stepped in as Arvid’s dedicated security marshals. We didn’t just hand him a manual; we built a custom Azure security and compliance blueprint tailored specifically for the shipping industry. We used the Azure security and compliance center to create a live “Health Score” dashboard, allowing Arvid to see his safety level in real-time with simple green and red indicators. It’s like having a high-tech security tower that monitors every gate and corridor of your business 24/7, fixing potential holes before a “digital pirate” even gets close.
The Result Arvid’s firm recently passed a major international audit with flying colors. His partners are impressed by his “secure by design” approach, and Arvid is finally sleeping soundly. He loves that vorza360 handles the heavy lifting of Microsoft Azure security & compliance, leaving him free to focus on navigating his fleet across the globe.
Saskia de Vries (Netherlands)
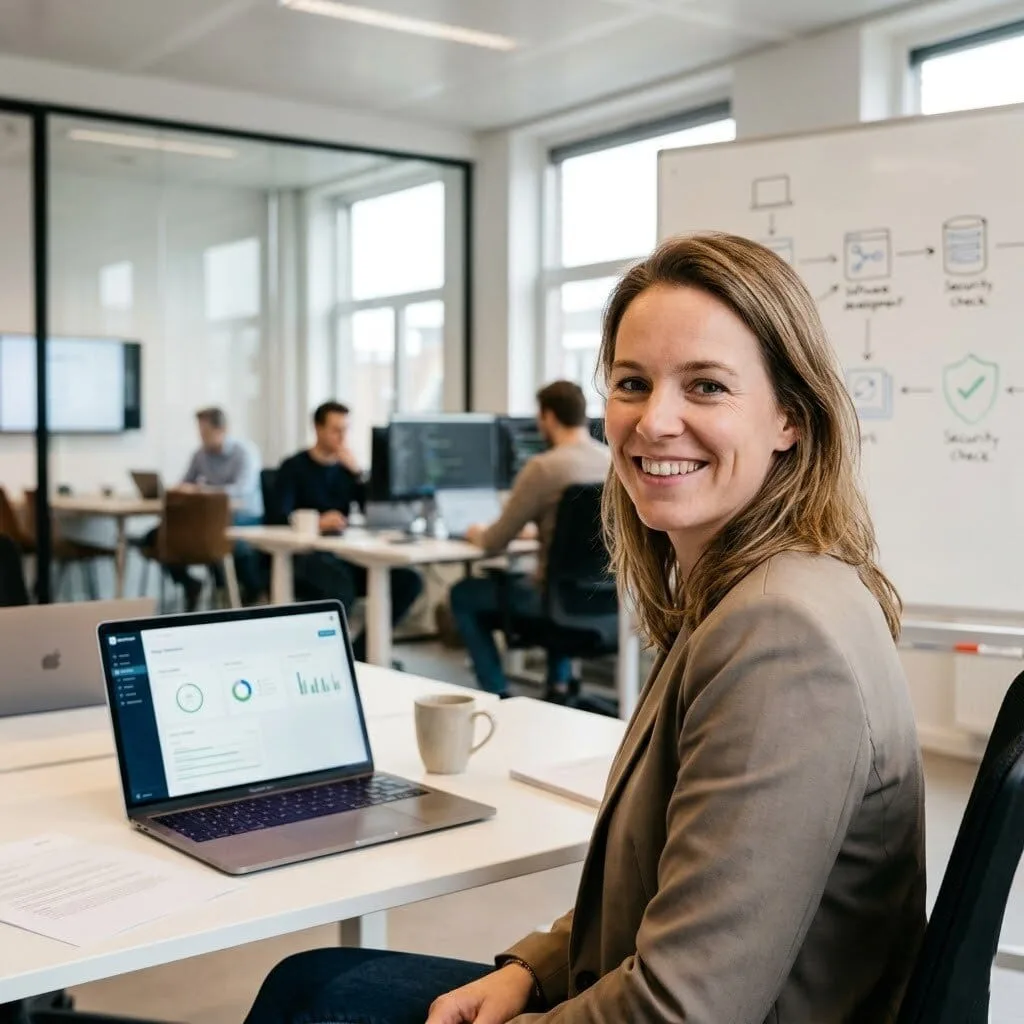
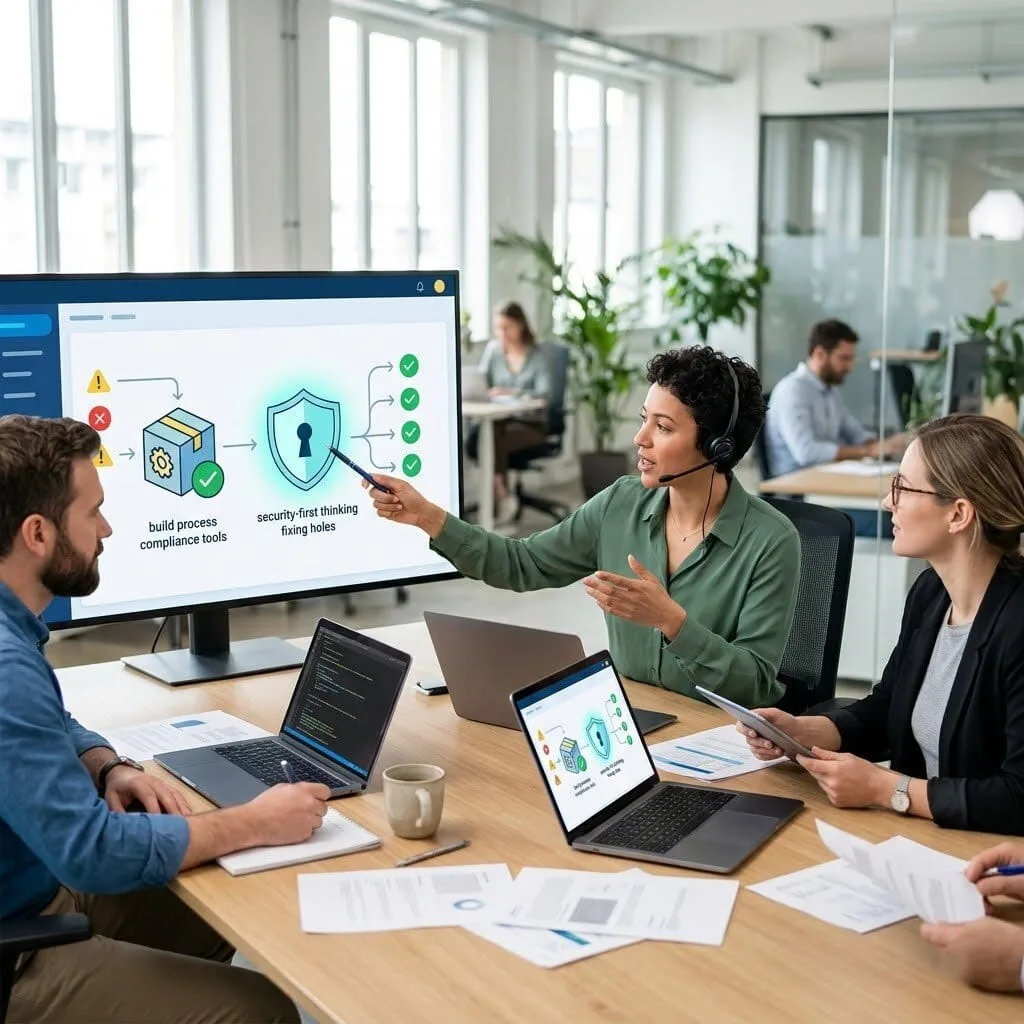
The Challenge Saskia manages a growing fintech startup in Amsterdam. Her developers move fast, constantly pushing out new updates to their payment app. However, she was terrified that in the rush to launch, someone might accidentally leave a “back door” open for hackers. She needed a way to bake safety into her team’s daily work without slowing down their creative spark.
The vorza360 Solution We implemented an insightful strategy using Azure devops security compliance tools. We set up automated “safety gates” that check the code for vulnerabilities every time a developer saves their work. This “security-first” thinking means any mistakes are caught and fixed in the “digital workshop” before they ever reach a customer’s phone. It is like having a professional safety inspector who stands right next to the assembly line, quietly ensuring every bolt is tight without ever stopping the machines.
The Result Saskia’s app is now known as one of the safest in the Dutch market. Her team is more confident because they know they have a “safety net” catching their errors. She appreciates the Azure security compliance service we provide and the easy words we used to turn a complex technical hurdle into a competitive advantage for her business.
Finnian O’Shea (Ireland)
The Challenge Finnian runs a specialized medical recruitment agency in Dublin. Handling sensitive healthcare records means he has to follow incredibly strict privacy rules. He was overwhelmed by the paperwork required to stay “audit-ready” and felt that his current cloud setup was a “black box” he didn’t fully understand. He needed a partner who could simplify the complexity and provide a managed safety net.
The vorza360 Solution We acted as Finnian’s professional guides, providing a tailored Azure security compliance service package built for the healthcare field. We installed “digital locks” on his most sensitive folders and set up automated guardrails that prevent data from being shared accidentally. We also provided a clear roadmap that explains his compliance status in very easy words. It is like having a master locksmith and a legal expert rolled into one, ensuring every cabinet is locked and every record is filed exactly where the auditors want to see it.
The Result Finnian no longer fears the word “audit.” His agency in Ireland is now a model of data privacy, and his clients trust him more than ever with their personal information. He values the human-first approach vorza360 takes and feels like he finally has a technical partner who speaks his language, not just “code.
Mireille Beaumont (France)
The Challenge Mireille manages a high-end luxury brand in Lyon with a massive database of international VIP clients. She knew that a single data leak would destroy her brand’s reputation overnight. She wanted to move her operations to the cloud but was hesitant because she didn’t know how to protect her “crown jewels” from modern cyber threats. She needed more than a tool; she needed a complete Microsoft Azure security & compliance managed service.
The vorza360 Solution We built a “managed digital fortress” for Mireille’s brand. We started by securing her team’s identities with multi-layer “digital keys” and then wrapped her entire network in a protective shield. We use the Azure security and compliance center to monitor her environment every single day, adjusting her defenses as new threats emerge. It is like having an invisible elite guard around her boutique that is always one step ahead of the crowd, ensuring her VIPs always have a safe and private experience.
The Result Mireille’s brand has successfully moved to the cloud with zero security incidents. Her client list is safer than ever, and she has a professional report she can show her board members to prove it. She loves the creative approach we took to match her brand’s high standards and values the “hands-off” peace of mind that vorza360 provides in France.
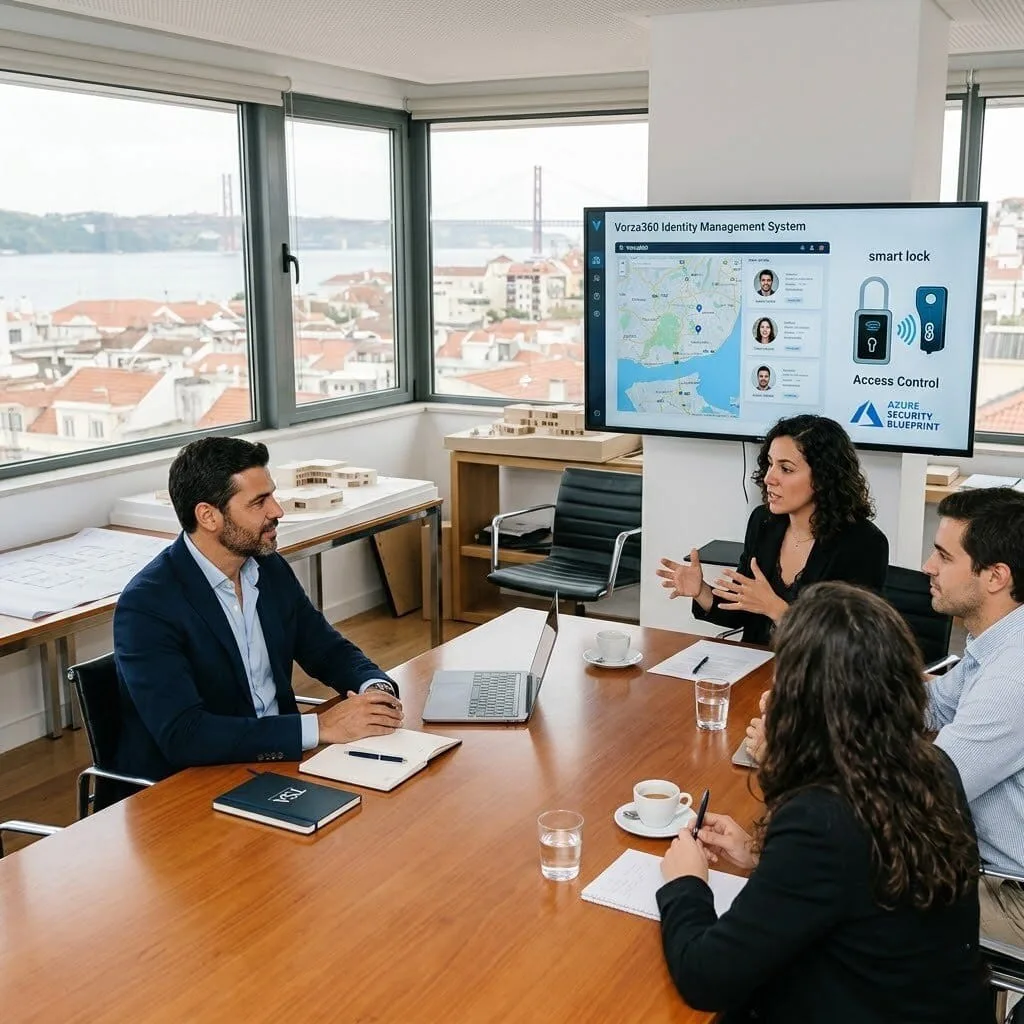
Thiago Silva (Portugal)
The Challenge Thiago runs a busy architecture firm in Lisbon and was struggling to keep track of all the different “digital keys” and passwords his team was using. He was worried that an ex-employee might still have access to his private blueprints or that a weak password could let a hacker in. He needed a way to manage his team’s identities and ensure his business was “secure by design.”
The vorza360 Solution We simplified Thiago’s security by building a custom identity management system within his Azure security and compliance blueprint. We set up “smart locks” that recognize his employees and ensure they only have access to the projects they are currently working on. If someone leaves the firm, their “digital key” vanishes instantly with one click. It is like having a smart building where every door knows exactly who is allowed to enter, keeping the intruders out and the secret plans safe inside.
The Result The “password chaos” at Thiago’s firm is a thing of the past. His team is more productive because they have easy, secure access to their work, and Thiago feels in total control of his firm’s safety. He appreciates the Azure security compliance service we offer and the simple, human-centric way we manage his digital safety net in Portugal.
Protecting Your Business and Your Reputation
In today’s digital world, security isn’t just about blocking hackers; it’s about building trust with your customers. At vorza360, we provide Microsoft Azure security & compliance as a complete service. We don’t just “sell” you security tools, we manage your entire digital safety net. From protecting your identity to securing your network, we ensure every layer of your cloud environment is “secure by design.”
We understand that keeping up with legal rules like GDPR or ISO can be overwhelming. That’s why we use the Azure security and compliance center to monitor your “Health Score” every single day. We take the technical burden of compliance off your shoulders, providing you with a clear roadmap and automated guardrails. With vorza360, you can focus on growing your business while we ensure your cloud is private, safe, and fully compliant.
How we do it
We combine smart technology with a human-first approach to make cloud safety easy.
Creative Approaches
We don’t believe in “one size fits all.” We build a custom Azure security and compliance blueprint for your business, setting up “digital locks” that fit your specific workflow and industry needs perfectly.
Insightful Strategies
Our team uses Azure devops security compliance tools to check for safety issues while your apps are being built. This “security-first” thinking means we find and fix potential holes before they ever go live.
Tailored Solutions
Whether you need to meet medical, financial, or general business standards, we provide Azure security compliance service packages that give you exactly the reports and protection you need for your specific field.
Creative Approaches
We don’t believe in “one size fits all.” We build a custom Azure security and compliance blueprint for your business, setting up “digital locks” that fit your specific workflow and industry needs perfectly.
Insightful Strategies
Our team uses Azure devops security compliance tools to check for safety issues while your apps are being built. This “security-first” thinking means we find and fix potential holes before they ever go live.
Tailored Solutions
Whether you need to meet medical, financial, or general business standards, we provide Azure security compliance service packages that give you exactly the reports and protection you need for your specific field.
Here is what our Clients are saying About us
Olli Virtanen (Finland)
Our Azure environment had no consistent security baseline, different teams had set things up differently and nobody had an overall view of our security posture. vorza360 enabled Microsoft Defender for Cloud, remediated the high-severity findings, and established a governance framework to maintain the posture going forward.
Sara Al-Khalidi (Saudi Arabia)
vorza360 configured Azure Policy initiatives across our subscriptions to enforce our security and compliance requirements automatically. Resources that don’t meet the standard are flagged immediately and in some cases remediated automatically. Our compliance posture is now something we manage proactively rather than discover retrospectively during audits.
Ionuț Marin (Romania)
Our organisation needed to meet ISO 27001 requirements for our Azure environment. vorza360 assessed our current configuration against the standard, identified every gap, and implemented the required controls systematically. The structured approach they took gave our auditors a clear evidence trail for every control.
Meena Subramaniam (India)
vorza360 implemented a comprehensive secrets management strategy for our Azure environment using Key Vault, eliminating hardcoded credentials from our application configurations and code repositories. The ‘no-plaintext-secrets’ policy they implemented and enforced via Azure Policy has closed a category of risk we’d been aware of but hadn’t properly addressed.
Lars Sørensen (Denmark)
vorza360 set up Microsoft Sentinel as our Azure SIEM and built detection rules appropriate for our threat model. The ‘detect-what-matters’ approach they took focused on high-fidelity alerts rather than volume, so our security team reviews meaningful alerts rather than drowning in noise.
Chidinma Adeyemi (Nigeria)
vorza360 built Azure DevOps pipelines for our infrastructure-as-code deployments using Terraform so our Azure environment is provisioned consistently and every change is reviewed, tested, and applied through the pipeline rather than by someone clicking in the portal. Our infrastructure drift problem simply disappeared.
More about Microsoft Azure
Azure Virtual Machines
Scale your business effortlessly with vorza360’s expert Azure virtual machine services.
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is Microsoft Defender for Cloud and how does vorza360 use it for Azure security?
Microsoft Defender for Cloud (formerly Azure Security Center) is a unified cloud security posture management (CSPM) and cloud workload protection platform (CWPP) that provides continuous security assessment, threat protection, and security recommendations across Azure resources, on-premises servers, and other cloud platforms (AWS, GCP). vorza360 uses Defender for Cloud as the primary Azure security management platform: we enable it across all Azure subscriptions and configure the Defender plans appropriate to each workload type (Defender for Servers, Defender for Databases, Defender for Containers, Defender for Storage). We review the Secure Score, a numerical measure of the organization’s security posture calculated from Defender for Cloud’s assessment of all resources, and prioritize remediating the recommendations that have the highest security impact per remediation effort. We configure workflow automation that creates ITSM tickets for critical security recommendations and generates weekly security posture reports for security leadership.
How does vorza360 implement Azure governance through policies and management groups?
Azure governance ensures that resources deployed across an organization comply with security, compliance, and operational standards, preventing individual teams from deploying resources that violate organizational policies. vorza360 implements Azure governance using a structured Management Group hierarchy that organizes Azure subscriptions (production workloads, non-production, sandbox, identity), enabling policy assignments to propagate down to all subscriptions in a management group without configuring each subscription individually. We implement Azure Policy initiatives (collections of related policies) that enforce: allowed resource locations (preventing deployment to non-approved regions), required resource tagging (enforcing cost allocation tags on all resources), allowed VM SKUs (preventing deployment of expensive GPU or large memory VMs unless explicitly approved), diagnostic settings deployment (automatically applying monitoring configuration to new resources), and security baseline configurations (enforcing encryption, network access restrictions). Policies with DeployIfNotExists or Modify effects automatically remediate non-compliant resources without requiring manual action.
How does vorza360 implement Azure Key Vault for secrets and certificate management?
Azure Key Vault is the centralized secrets and cryptographic key management service for Azure, providing secure storage for application secrets (connection strings, API keys, passwords), cryptographic keys (used for encrypting data), and digital certificates (for TLS/SSL), with comprehensive access control, audit logging, and integration with Azure services and application SDKs. vorza360 implements Azure Key Vault as the single source of truth for all secrets in Azure environments: we migrate all secrets from application configuration files, environment variables, and connection strings into Key Vault, replacing hardcoded values with Key Vault references. We configure access policies or Azure RBAC role assignments that grant each application and service account only the specific Get permission on the specific secrets it needs, not blanket access to the entire vault. We enable Key Vault soft-delete and purge protection to prevent accidental or malicious deletion of secrets. We integrate Key Vault with Azure App Service, Azure Functions, AKS, and VMs using Managed Identity, eliminating the need to store any credentials in the application itself.
How does vorza360 help organizations achieve compliance with regulations such as GDPR, HIPAA, and ISO 27001 in Azure?
Microsoft Azure provides a comprehensive compliance framework and Microsoft Defender for Cloud includes built-in regulatory compliance dashboards that map Azure resource configurations to the controls required by major compliance frameworks. vorza360 uses this as a foundation for regulatory compliance implementation: for GDPR, we implement data residency controls (restricting data to EU Azure regions), configure Data Protection Impact Assessment documentation, implement Azure Purview for data discovery and classification of personal data, configure appropriate retention and deletion policies, and implement breach notification automation. For HIPAA, we ensure the Microsoft Business Associate Agreement (BAA) is in place, implement PHI encryption both at rest and in transit, configure comprehensive audit logging using Azure Monitor and Log Analytics, and restrict PHI access to authorized roles. For ISO 27001, we map Azure controls to ISO 27001 Annex A requirements and use Defender for Cloud’s ISO 27001 compliance dashboard to track and remediate gaps. We provide compliance documentation and evidence for audit purposes.
How does vorza360 implement a Zero Trust security model in Microsoft Azure?
Zero Trust is a security framework based on the principle ‘never trust, always verify’, rather than trusting any user or device because they are inside the corporate network, every access request is verified continuously regardless of where it originates. Microsoft Azure provides the building blocks for Zero Trust, and vorza360 implements them in a coordinated architecture: Identity verification using Azure AD Conditional Access that evaluates every authentication attempt against policies requiring MFA, device compliance, and risk signals before granting access. Device health using Microsoft Intune-enforced compliance policies that verify devices are patched, encrypted, and have endpoint protection before allowing access to corporate data. Network micro-segmentation using Azure Virtual Network and NSGs to isolate workloads so a compromised workload cannot laterally access other workloads. Application-level access using Azure AD Application Proxy and Conditional Access App Control for browser-based access to internal applications without VPN. Data protection using Microsoft Purview for data classification and sensitivity labeling. Every layer works together to ensure that even if one defensive layer is breached, the others continue to protect your data.