vorza360 builds specialized ERP risk and compliance systems to help your business follow all rules and manage risks centrally. We provide ERP risk management software that tracks security, ensures regulatory compliance, and automates control monitoring across your enterprise operations.
The Challenge: Victoria was the Chief Compliance Officer of a regional bank holding company subject to SOX, BSA, and OCC examination. Her challenge was that her risk and control documentation lived in a combination of SharePoint folders, Excel workbooks, and a legacy GRC tool that hadn’t been updated in five years. When examiners arrived, her team spent weeks pulling data together, and the last examination had identified three ‘gaps’ in control documentation that resulted in a Management Response Letter she was determined not to repeat.
The vorza360 Solution: We implemented a Risk & Compliance ERP with a Control Automation layer that monitors the bank’s core banking system continuously. The ‘segregation-of-duties’ logic we encoded prevents any single user from performing conflicting tasks, such as creating a vendor and approving their payment, automatically, without relying on manual periodic reviews. The Compliance Reporting Dashboards generate examination-ready documentation in the OCC’s preferred format with a single click, replacing weeks of manual compilation.
The Result: Victoria’s most recent OCC examination produced zero gaps in control documentation, the first clean examination in six years. Ongoing control monitoring that previously required a two-person team reviewing manually now runs automatically, freeing those resources for higher-value risk analysis. She values the SAP GRC/Oracle GRC Connectors we used to integrate with her core banking system, which ensured no compliance data had to be manually re-entered from the banking platform into the GRC system.
Joost Vermeer (Netherlands)
The Challenge: Joost was the head of ERM for a European insurance group subject to Solvency II regulation. His challenge was that capital adequacy calculations required quarterly data pulls from 14 different source systems across three countries, and the manual compilation process introduced enough lag and potential error that his actuarial team never fully trusted the numbers they were working with. A model error discovered in a prior quarter had required a regulatory restatement, an experience he was determined not to repeat.
The vorza360 Solution: We built a Risk & Compliance ERP with automated data ingestion pipelines from all 14 source systems, eliminating every manual data-pull step in the Solvency II capital calculation process. The Continuous Control Monitoring layer runs automated data quality checks on every input, flagging anomalies and requiring sign-off before the data is accepted into the regulatory model. The Audit Trail Framework logs every data input, every model parameter change, and every final calculation, making the regulatory model fully traceable and reproducible.
The Result: Joost’s quarterly Solvency II capital calculation cycle compressed from 22 working days to 9. His actuarial team’s confidence in the input data rose dramatically once they could see the source traceability for every figure. He values the COSO Framework and ISO 31000 compliance mapping we embedded into the system design, which ensured that the ERM approach met both internal audit and external regulator expectations from day one.
Brendan Healy (Ireland)
The Challenge: Brendan was the Head of Risk for a publicly listed Irish pharmaceutical company. His company was subject to a complex web of regulations, FDA (for US exports), EMA (for European sales), and Irish data protection law, each with different documentation and audit requirements. His risk team was maintaining three separate compliance frameworks in three separate tools, and when a new regulatory requirement came in, assessing its impact on all three frameworks simultaneously was taking weeks.
The vorza360 Solution: We implemented a unified Risk & Compliance ERP with a Regulatory Mapping layer that links every control point to the specific regulations it satisfies. When the Irish Data Protection Commission issued a new guidance note, Brendan’s team can run a single query to identify every existing control that requires review, and every new control that needs to be designed, across all three regulatory frameworks simultaneously. The Compliance Reporting Dashboards generate regulation-specific reports for FDA, EMA, and DPC independently from the same underlying control data.
The Result: Brendan’s impact assessment time for new regulatory requirements fell from weeks to days. The Risk Taxonomy we structured into the system gave his team a shared language for discussing risks across regulatory domains for the first time. He values the Security Risk Services Plugins that continuously monitor user access patterns and alert his team to behavior that could indicate an insider risk, a capability that was not possible with his previous fragmented toolset.
Ahmed Al-Rashidi (UAE)
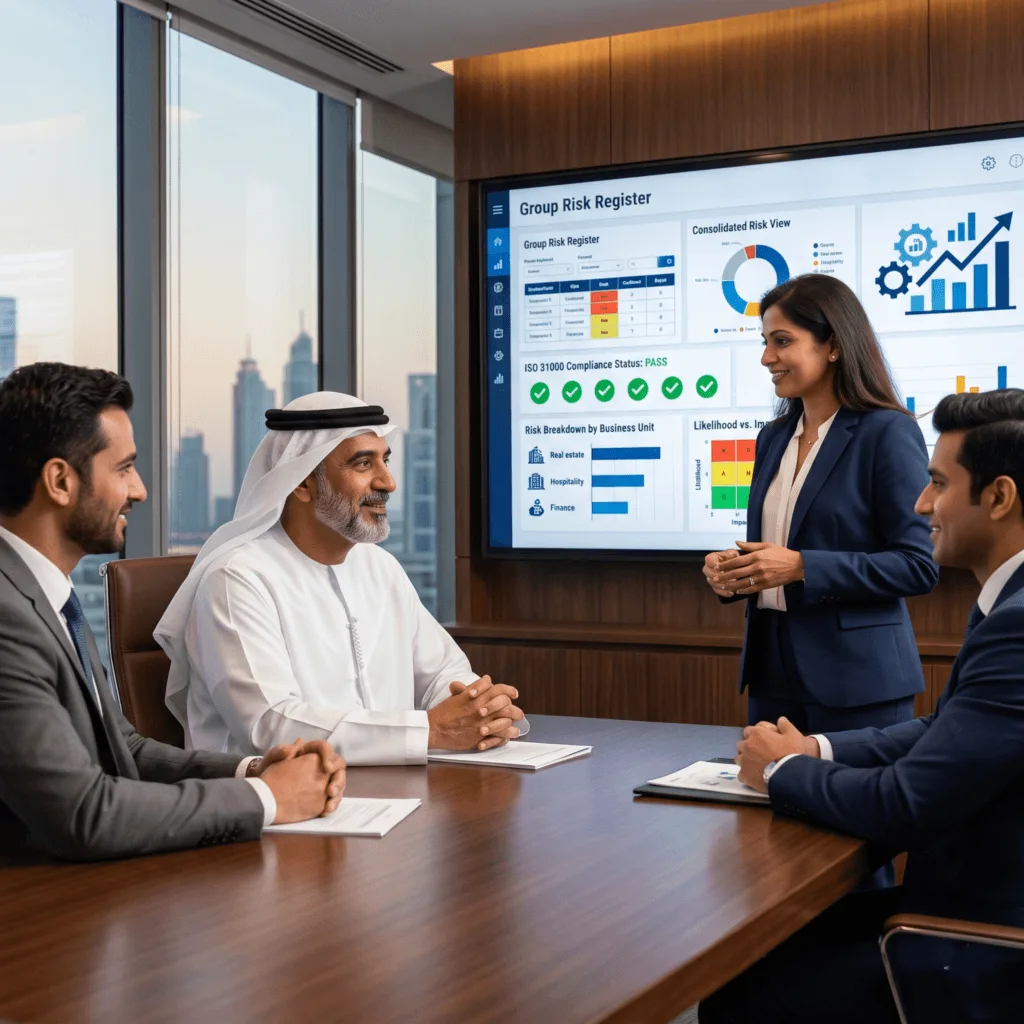
The Challenge: Ahmed was the Group Risk Director for a UAE-based conglomerate with business interests spanning real estate, hospitality, and financial services. Each business unit had its own risk management approach and none of them reported in a consistent format, making board-level risk governance an exercise in informed guessing rather than data-driven decision-making. The group had failed its ISO 31000 certification audit the previous year, citing inadequate risk reporting consistency.
The vorza360 Solution: We implemented a Risk & Compliance ERP that standardizes risk assessment methodology across all business units while allowing each unit to define its own sector-specific risk categories. The Risk Taxonomy we built gives the group a consistent risk language, every risk is rated on the same likelihood and impact scale regardless of which business unit it originates from. The Compliance Reporting Dashboards produce a consolidated Group Risk Register for each board meeting, automatically aggregated from business unit inputs, with drill-down capability for directors who want unit-level detail.
The Result: The group passed its ISO 31000 certification on the subsequent attempt, with the auditors specifically commending the consistency and traceability of the risk reporting framework. Ahmed’s board now receives a risk update they describe as genuinely useful rather than a compliance formality. He values the Microsoft Dynamics 365 integration we built, which pulls financial risk exposure data directly from the group’s ERP into the GRC system without manual data transfer.
Preethi Nair (India)
The Challenge: Preethi was the compliance manager for a listed Indian NBFC (non-banking financial company) regulated by the RBI. Her most pressing challenge was managing the flood of regulatory circulars that the RBI issued, frequently amending reporting timelines, disclosure requirements, and product rules. Each circular had to be assessed for impact, translated into internal policy changes, and tracked through implementation. With no system to manage this, circulars were occasionally missed, leading to avoidable compliance gaps.
The vorza360 Solution: We built a Risk & Compliance ERP with a Regulatory Change Management module. When a new RBI circular is issued, a team member logs it into the system with the effective date, and the Regulatory Mapping Tools automatically identify which internal policies, controls, and reporting templates are potentially affected. Each affected item generates an action item assigned to the responsible team member, with a deadline linked to the circular’s effective date. The Compliance Reporting Dashboard shows Preethi real-time completion status for every regulatory action.
The Result: Preethi’s organization has not missed a regulatory implementation deadline since the system launched. The Audit Trail Framework gives her documentation of every regulatory change assessment, useful during RBI inspections. She values the Continuous Control Monitoring capability, which now gives her automated assurance on key RBI compliance metrics daily rather than monthly.
Daniel Beauregard (Canada)
The Challenge: Daniel was the Chief Risk Officer of a Canadian credit union subject to OSFI oversight. His specific challenge was third-party risk management: the credit union relied on 47 technology vendors and service providers, each of which represented a potential operational or cybersecurity risk. He had no systematic way to assess and monitor those vendor risks, assessments were done ad hoc when vendor contracts came up for renewal, missing the risks that emerged in the months between renewals.
The vorza360 Solution: We implemented a Risk & Compliance ERP with a Third-Party Risk Management module. Every vendor is assessed against a standardized risk questionnaire on initial onboarding, and the system schedules annual re-assessments automatically. The Security Risk Services Plugins monitor publicly available security intelligence feeds and flag any vendor that appears in a data breach or regulatory action notice, triggering an out-of-cycle review without waiting for the annual schedule. The Access Control Tools enforce a governance rule that no vendor contract can be renewed without a completed risk assessment on file.
The Result: Daniel’s team identified a material cybersecurity issue with one vendor through the continuous monitoring alerts, 47 days before that vendor publicly disclosed the incident. The early warning allowed the credit union to implement mitigating controls and avoid the data exposure that affected other customers of the same vendor. He values the COBIT framework integration we configured, which maps vendor control requirements directly to the IT governance standards OSFI expects his credit union to maintain.
How we do it
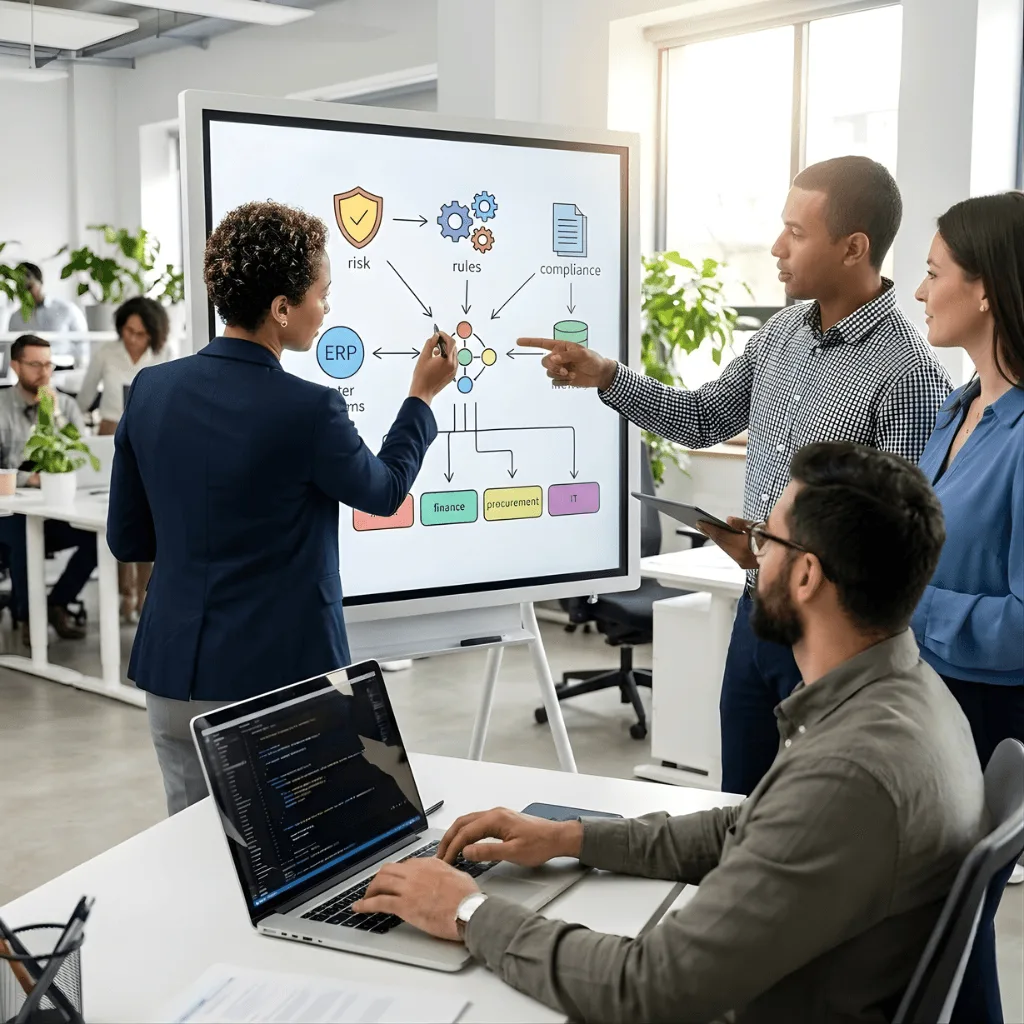
Our process is focused on securely integrating risk management and legal controls directly into your core ERP system.
Risk Mapping and Rules
We start by identifying all the risks and rules your company must follow (like SOX or GDPR). We map out where these risks exist in your ERP (like in finance or procurement). This creates the blueprint for control points.
Control Automation
We automate the checking of controls to prevent fraud and errors. We build rules to ensure that no single person can perform conflicting tasks (segregation of duties). This ensures continuous and reliable ERP compliance.
Reporting and Auditing
We configure the system to make audits simple and fast. We set up automated reports that prove you are following regulations. This gives management a clear view of security and compliance risks.
Risk Mapping and Rules
We start by identifying all the risks and rules your company must follow (like SOX or GDPR). We map out where these risks exist in your ERP (like in finance or procurement). This creates the blueprint for control points.
Control Automation
We automate the checking of controls to prevent fraud and errors. We build rules to ensure that no single person can perform conflicting tasks (segregation of duties). This ensures continuous and reliable ERP compliance.
Reporting and Auditing
We configure the system to make audits simple and fast. We set up automated reports that prove you are following regulations. This gives management a clear view of security and compliance risks.
Tools
Key Tools vorza360 Offers
SAP GRC/Oracle GRC Connectors
Specialized interfaces to integrate our custom solutions with major existing GRC platforms.
Access Control Tools (SoD)
Software used to define and automatically enforce rules that prevent employees from having conflicting, risky access rights.
Compliance Reporting Dashboards
Custom reporting tools that pull data from the ERP to instantly generate necessary regulatory reports.
Security Risk Services Plugins
Plugins that monitor user activities and system settings to provide proactive ERP security risk services.
Multiple Platform Support
We ensure our solutions integrate with the major enterprise platforms where governance, risk, and compliance are managed.
SAP (S/4HANA/ECC)
Integration with the most common enterprise software platform.
Oracle Fusion/EBS
Full support for Oracle’s large-scale ERP environments.
Microsoft Dynamics 365
Linking with Microsoft’s unified suite of business applications.
ServiceNow
Connecting risk and compliance data with IT service and operations management.
Audit Management Systems
Integration with tools used for internal and external audit processes.
Cloud Hosting (AWS/Azure)
Secure, high-availability hosting for sensitive ERP risk and compliance data.
SAP (S/4HANA/ECC)
Integration with the most common enterprise software platform.
Oracle Fusion/EBS
Full support for Oracle’s large-scale ERP environments.
Microsoft Dynamics 365
Linking with Microsoft’s unified suite of business applications.
ServiceNow
Connecting risk and compliance data with IT service and operations management.
Audit Management Systems
Integration with tools used for internal and external audit processes.
Cloud Hosting (AWS/Azure)
Secure, high-availability hosting for sensitive ERP risk and compliance data.
Multiple Frameworks Support
COSO Framework
Used for designing and evaluating internal controls over financial reporting.
ISO 31000
Provides guidelines for implementing effective enterprise risk management (ERM).
COBIT
Framework for IT governance and management, ensuring technology controls are strong.
Segregation of Duties (SoD) Logic
Coding rules to prevent users from performing risky combinations of tasks to avoid fraud.
Regulatory Mapping Tools
Frameworks that map specific laws (like GDPR) to necessary control points in the ERP.
Continuous Control Monitoring (CCM)
Logic that automatically and constantly checks if internal controls are working correctly.
Risk Taxonomy
A structured way of defining, identifying, and classifying all possible business risks.
Audit Trail Framework
Ensuring every critical action in the ERP is logged and tracked for easy review during an
Custom Headless Development
We are an eCommerce website design company, that uses the best creative skills to meet your business needs and ensure customer satisfaction. We’re with you every step of the way, from the beginning of your project to its completion.
Fashion & Apparel
Food & Grocery
Retail
FMCG
Real Estate
Construction
Hotel
Healthcare
Telecom
Fintech
Manufacturing
Automotive
Our ERP Risk & Compliance Cycle
Our systematic cycle ensures a successful deployment of your ERP governance risk and compliance solution.
Step 1
Risk Assessment
Step 2
Control Design
Step 3
Configuration
Step 4
Testing & Validation
Step 5
Deployment & Training
Step 6
Monitor & Optimize
Step 1
Risk Assessment
Identify all regulations and map current business risks and internal controls.
Step 2
Control Design
Define access rules (SoD), set control points in ERP modules, and configure risk models.
Step 3
Configuration
Implement the GRC module, build custom control tests, and set up alert systems.
Step 4
Testing & Validation
Test all access rules, validate control points, and run realistic audit simulations.
Step 5
Deployment & Training
Roll out the ERP risk management software, secure final user access, and train staff on new control processes.
Step 6
Monitor & Optimize
Continuously monitor control performance, update risk libraries, and automate ERP regulatory compliance reporting.
Here is what our Clients are saying About us
Pieter Janssen (Netherlands)
vorza360 built a risk and compliance management system for our financial services organisation that tracks regulatory obligations, maps controls, and monitors compliance status in real time. Our compliance team manages risk rather than chases paperwork.
Sara Al-Madani (Saudi Arabia)
vorza360 developed a compliance ERP for our bank that manages policy obligations, control testing, audit findings, and regulatory reporting in a single system. Our regulators have commented positively on the quality of our compliance documentation.
Silviu Florescu (Romania)
vorza360 built an enterprise risk management system for our organisation that consolidates risk registers across departments, tracks mitigation actions, and provides board-level risk dashboards. Risk governance that used to exist in spreadsheets is now systematic.
Vikram Pillai (India)
vorza360 developed a compliance management platform for our pharmaceutical company covering GMP compliance, document control, deviation management, and CAPA tracking. Our audit findings have reduced and our regulatory submissions are better evidenced.
Charlotte Nielsen (Denmark)
vorza360 built a risk and compliance system for our insurance company managing operational risk, compliance obligations, and internal audit findings in a unified platform. Our risk committee has better information and our regulatory relationship has improved.
Vikram Pillai (India)
vorza360 developed a compliance management platform for our pharmaceutical company covering GMP compliance, document control, deviation management, and CAPA tracking. Our audit findings have reduced and our regulatory submissions are better evidenced.
More about ERP
Custom ERP Development
vorza360 provides full custom ERP software development services, creating powerful…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is a Risk & Compliance ERP and why does a business need one?
A Risk & Compliance ERP integrates governance, risk management, and regulatory compliance controls directly into your core business operations software. As businesses grow and regulations multiply, from SOX and GDPR to ISO standards and industry-specific rules, managing compliance manually becomes impossible and dangerous. vorza360 builds Risk & Compliance ERP systems that automate control monitoring, maintain complete audit trails of every critical business action, enforce access restrictions to prevent fraud, and generate regulatory reports automatically, turning compliance from a burden into a built-in business process.
How does vorza360 prevent fraud and unauthorized access through the Risk & Compliance ERP?
We implement Segregation of Duties (SoD) logic, rules that ensure no single employee can perform conflicting tasks that together would allow fraud or error, such as both raising and approving a purchase order. These rules are enforced automatically by the system, blocking any transaction that violates defined control policies. Our Access Control Tools configure granular user permissions so every employee can only access the specific data and functions their role requires, creating a strong internal control environment.
How does the Risk & Compliance ERP make audit preparation easier?
Audit preparation is dramatically simplified by our Audit Trail Framework, which ensures that every critical action within the ERP, every transaction, approval, data change, or access event, is automatically logged with a timestamp and user identity. Our Compliance Reporting Dashboards can generate the specific regulatory reports your auditors require at the click of a button, pulling data directly from this audit trail. What previously took days of manual document gathering can be done in minutes with a vorza360 Risk & Compliance ERP.
Which regulatory frameworks does vorza360's Risk & Compliance ERP support?
Our Risk & Compliance ERP solutions are built to support a wide range of regulatory and governance frameworks, including SOX (Sarbanes-Oxley) for financial reporting controls, GDPR for data privacy, HIPAA for healthcare data, ISO 31000 for enterprise risk management, COSO for internal control design, and COBIT for IT governance. We also conduct a thorough risk mapping exercise at the start of every project to identify all regulations specific to your industry and geography, ensuring the system is configured to meet your exact compliance obligations.
Can vorza360 integrate Risk & Compliance controls into our existing SAP or Microsoft Dynamics ERP?
Yes. We specialize in extending existing enterprise ERP platforms with GRC (Governance, Risk, and Compliance) capabilities. We use SAP GRC and Oracle GRC connectors to integrate our compliance modules directly with SAP S/4HANA, SAP ECC, Oracle Fusion, and Oracle EBS environments. For Microsoft Dynamics 365 users, we build native integration with the full Dynamics suite. This means you gain enterprise-grade compliance controls without replacing your existing ERP investment.