
Azure Networking
Build a fast and secure digital foundation with vorza360’s expert Azure network services. From private connections to advanced security, we provide the managed networking solutions your business needs to stay connected.

Shopify

WordPress

Figma

PHP

Flutter

React Js

Node Js

Python

Swift

Java

Vue.js

Kotlin

CSS

HTML
JavaScript
Customer Success Story
Soren Bakke (Norway)
The Challenge: Soren runs a specialized maritime engineering firm in Oslo that handles massive 3D models of ship hulls. His team was struggling with “data lag” because their large files were traveling over the public internet to reach their cloud storage. Every time a designer saved a change, the whole system would stutter. He was also deeply concerned about “digital pirates” since his designs are highly confidential and worth millions. He needed a fast, private “bubble” where his team could work without the risks or the slow speeds of the open web.
The vorza360 Solution We acted as Soren’s digital highway engineers, building a custom Virtual Network (VNet) specifically for his firm. We created “secret tunnels” using Private Endpoints, ensuring his design data never had to touch the risky public internet. To keep the bad guys out, we configured an Azure network security group to act as a smart gatekeeper, only allowing his verified staff into the system. It’s like moving your office from a busy public square into a private, gated community with its own high-speed private road.
The Result The “data lag” is gone, and Soren’s team is now working at the speed of thought. His blueprints are shielded by a professional-grade Azure network security system, and he no longer worries about data leaks. He loves the easy words we used to explain his new “private bubble” and values the rock-solid reliability of his Oslo office.
Elara Vance (Canada)
The Challenge Elara manages a fast-growing e-commerce platform in Toronto and was terrified of her website crashing during a major holiday sale. Her old setup couldn’t handle the “traffic spikes,” and she was worried that a single cyber-attack could bring her entire business to a halt. She needed a way to spread the workload and a “front door” that could automatically block hackers while welcoming customers with open arms.
The vorza360 Solution We implemented an Azure Load Balancer to ensure her apps never slow down by spreading incoming work evenly across multiple servers. We also set up an Application Gateway to act as a professional shield, protecting her site against “DDoS” attacks that try to crash servers. It’s like having a team of expert security guards at a stadium who not only check tickets instantly but also open extra gates the moment a large crowd arrives, keeping the line moving perfectly.
The Result Elara’s last big sale was a record-breaker with zero downtime. Her website stayed lightning-fast for every customer, and her Azure web app networking settings are now tuned for global success. She appreciates the professional Azure network services vorza360 provides and feels like she has a true technical partner in Canada.
Niall O’Sullivan (Ireland)
The Challenge: Niall runs a financial consultancy in Dublin and has a team that is split between the city office and several remote locations across the Irish countryside. He was struggling to keep everyone connected to the same secure database. His remote staff were using “messy” connections that felt slow and unsafe. He needed to bridge the gap between his physical office and the cloud, making them feel like one single, secure network.
The vorza360 Solution We provided an insightful hybrid connection by setting up an Azure virtual network gateway. We created secure “Point-to-Site” VPNs for his remote team, allowing them to work from home with the same safety as if they were sitting in the Dublin office. We also used VNet Peering to link his different cloud spaces together, ensuring a seamless flow of information. It’s like building a secure, invisible bridge that connects every home office directly to the main headquarters, so everyone is always on the same team.
The Result The “connection gaps” have vanished for Niall’s firm. His consultants can access secure files from anywhere in Ireland without a single glitch. He values the Azure networking certification standards we follow and the fact that we handle all the daily “heavy lifting” of his Azure network services management.
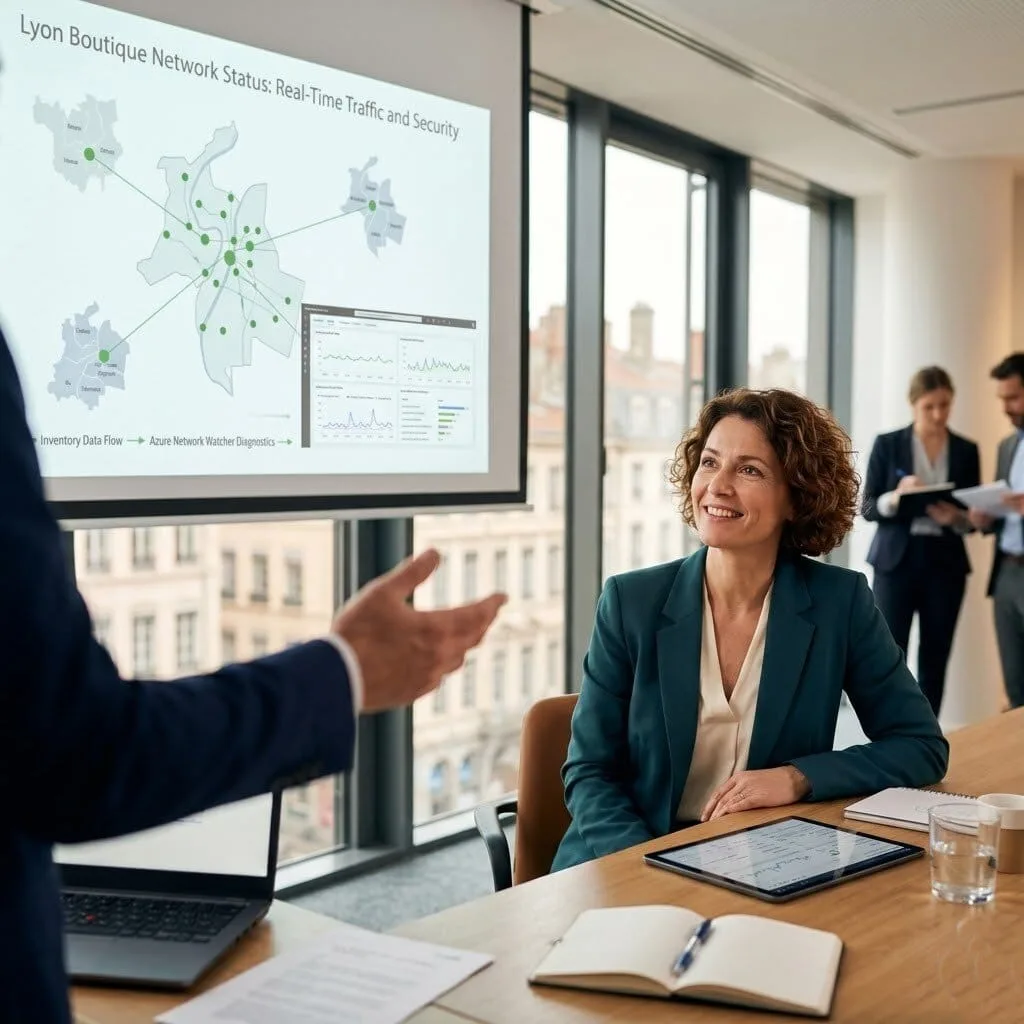
Marcelle Dubois (France)
The Challenge Marcelle manages a chain of high-end boutiques in Lyon and needed a way to manage her inventory across twenty different locations in real-time. Her biggest headache was blind spots; she couldn’t see why her network was slowing down until it was too late. She needed a way to “see” her traffic and fix glitches before they affected her sales staff or her customers.
The vorza360 Solution We used our tech edge to install Azure Network Watcher, a professional diagnostic tool that allows us to “see” her network health instantly. We also added a professional-grade shield using Azure Firewall to protect her entire virtual environment. We focused on Azure accelerated networking to ensure her inventory data moves between shops in a blink. It’s like having a high-tech control tower that watches every road in your city, allowing you to clear a traffic jam before the drivers even notice it.
The Result The “blind spots” are a thing of the past for Marcelle. She can now see exactly how her data is flowing and knows her Azure network security groups are blocking any suspicious activity. She loves the simplified management vorza360 provides and the fact that her French boutiques are always online and fast.
Bram van der Meer (Netherlands)
The Challenge Bram manages a busy medical clinic in Rotterdam and must follow very strict rules about how patient data is handled. He was using a “standard” cloud setup, but he was worried it didn’t meet the legal requirements for privacy. He needed a centralized way to manage his cloud network that was both 100% secure and easy for his non-technical staff to understand.
The vorza360 Solution We acted as Bram’s expert consultants, performing a regular audit to ensure his network follows all compliance rules. We simplified the management of his multiple Azure virtual networks so he has a single “command center” for his business. We used Azure DNS to manage his clinic’s website addresses, ensuring they are always reachable and fast for his patients. It is like having a professional office manager who also happens to be a world-class security expert, keeping everything organized and locked down.
The Result Bram’s clinic passed its latest data audit with flying colors. He no longer worries about “tech complexity” because he knows vorza360 is handling the proactive monitoring of his Azure network services. He values the human-first approach we take and the easy words we use to keep him informed in the Netherlands.
Beatriz Ortiz (Spain)
The Challenge Beatriz runs a creative marketing firm in Madrid and wanted to host high-resolution video portfolios for her clients. However, her website was loading too slowly for customers in other countries, and she was worried about her “big files” being stolen or copied. She needed high-performance web networking that was fast enough for video but secure enough for her artists’ intellectual property.
The vorza360 Solution We tuned Beatriz’s Azure web app networking settings for maximum speed and security. We implemented global traffic routing so her videos load from the server closest to her customer, and added built-in security certificates (SSL) to protect her data. We also used Azure accelerated networking to make her site feel “instant.” It is like moving from a local theater to a global broadcast network, everyone gets a front-row seat, and the quality is always perfect.
The Result Beatriz’s firm is now attracting international clients because her website is so fast and professional. She loves that she can share her team’s hard work with the world without worrying about security or lag. She appreciates the expert guidance vorza360 provides based on the latest Azure network certification standards in Spain.
vorza360’s Tech Edge
Virtual Networks (VNet)
Network Security Groups (NSG)
Azure Load Balancer
+ 2
More
Application Gateway
Private Endpoints
vorza360’s Tech Edge
Virtual Networks (VNet)
We build an isolated virtual network in Azure that acts as a private “bubble” for your servers, keeping them safe from the public internet.
Network Security Groups (NSG)
Our team configures an Azure network security group for every part of your network, acting as a smart digital gatekeeper that only lets in the people you trust.
Azure Load Balancer
We ensure your apps never slow down by spreading incoming work evenly across multiple servers, providing 24/7 reliability.
Application Gateway
For your websites, we provide an advanced “front door” that protects against attacks while making sure your pages load instantly for customers.
Private Endpoints
We create “secret tunnels” for your data so that your databases and storage accounts never have to touch the risky public internet.
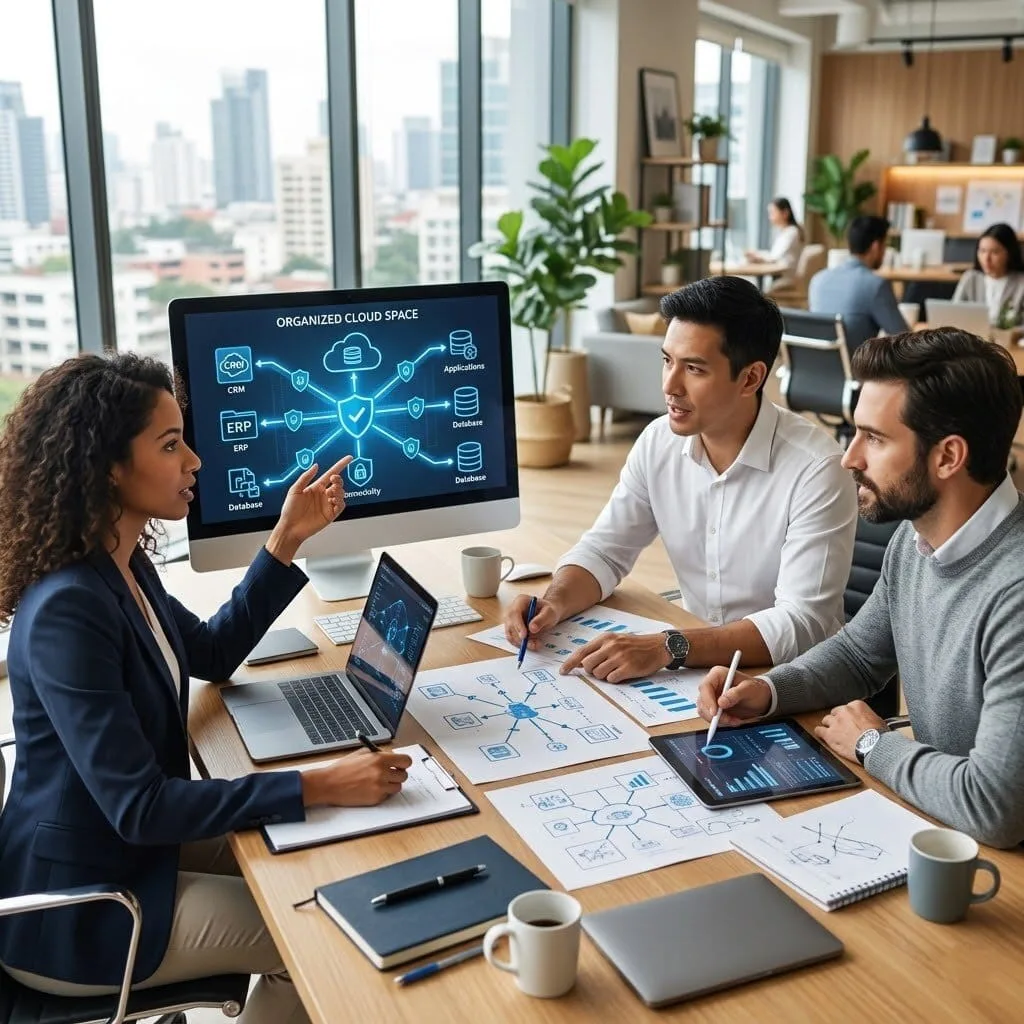
Secure Private Connectivity
We create a private and organized space in the cloud where your business applications can talk to each other safely.
Advantages
- Professional setup of Azure virtual networking environments.
- Logical separation of your web, app, and data layers for better safety.
- Custom IP address planning tailored to your office needs.
- Seamless integration with your existing Windows Azure networking setup.
- High-speed data paths that minimize lag and delays.
Robust Network Security
vorza360 acts as your 24/7 security guard, using a layered approach to keep hackers and threats away from your data.
Advantages
- Detailed configuration of every Azure network security group.
- Implementation of Azure network security protocols to block attacks.
- Real-time monitoring of all incoming and outgoing traffic.
- Protection against massive "DDoS" attacks that try to crash your site.
- Automated blocking of suspicious login attempts.
Hybrid Office Connections
We bridge the gap between your physical office and the cloud, making them feel like one single, secure network.
Advantages
- Setup of an Azure virtual network gateway for encrypted office-to-cloud tunnels.
- Secure "Point-to-Site" VPNs for your remote team members to work from home.
- Reliable Windows Azure virtual network syncing for your local servers.
- "Site-to-Site" connections that link your branch offices to Azure.
- Expert support for high-speed, private "ExpressRoute" connections.
High-Performance Web Networking
We ensure your web applications are fast, secure, and always ready for your customers, no matter how much traffic you get.
Advantages
- Expert tuning of Azure web app networking settings.
- Global traffic routing to reach customers in different countries.
- Built-in security certificates (SSL) to protect customer info.
- Caching services to make your images and videos load in a blink.
- Advanced Azure accelerated networking for your busiest systems.
Centralized Network Management
vorza360 takes over the daily “heavy lifting” of managing your cloud network so you can focus on your business goals.
Advantages
- Proactive monitoring of your Azure network services health.
- Troubleshooting of connection issues before they affect your work.
- Regular audits to ensure your network follows all compliance rules.
- Simplified management of multiple Azure virtual networks.
- Expert guidance based on the latest Azure networking certification standards.
Secure Private Connectivity
We create a private and organized space in the cloud where your business applications can talk to each other safely.
ADVANTAGES
- Professional setup of Azure virtual networking environments.
- Logical separation of your web, app, and data layers for better safety.
- Custom IP address planning tailored to your office needs.
- Seamless integration with your existing Windows Azure networking setup.
- High-speed data paths that minimize lag and delays.
Robust Network Security
vorza360 acts as your 24/7 security guard, using a layered approach to keep hackers and threats away from your data.
ADVANTAGES
- Detailed configuration of every Azure network security group.
- Implementation of Azure network security protocols to block attacks.
- Real-time monitoring of all incoming and outgoing traffic.
- Automated blocking of suspicious login attempts.
- Protection against massive "DDoS" attacks that try to crash your site.
Hybrid Office Connections
We bridge the gap between your physical office and the cloud, making them feel like one single, secure network.
ADVANTAGES
- Setup of an Azure virtual network gateway for encrypted office-to-cloud tunnels.
- Secure "Point-to-Site" VPNs for your remote team members to work from home.
- "Site-to-Site" connections that link your branch offices to Azure.
- Reliable Windows Azure virtual network syncing for your local servers.
- Expert support for high-speed, private "ExpressRoute" connections.
High-Performance Web Networking
We ensure your web applications are fast, secure, and always ready for your customers, no matter how much traffic you get.
ADVANTAGES
- Expert tuning of Azure web app networking settings.
- Global traffic routing to reach customers in different countries.
- Built-in security certificates (SSL) to protect customer info.
- Caching services to make your images and videos load in a blink.
- Advanced Azure accelerated networking for your busiest systems.
Centralized Network Management
vorza360 takes over the daily “heavy lifting” of managing your cloud network so you can focus on your business goals.
ADVANTAGES
- Proactive monitoring of your Azure network services health.
- Troubleshooting of connection issues before they affect your work.
- Regular audits to ensure your network follows all compliance rules.
- Simplified management of multiple Azure virtual networks.
- Expert guidance based on the latest Azure networking certification standards.
Why Choose vorza360 for This Service?
We build and manage your digital highways with a focus on speed and maximum security, ensuring your business stays connected and protected without you ever having to worry about the technical complexity.
We Build for Speed
By using Azure advanced networking techniques, we eliminate bottlenecks so your apps and team can work at the speed of thought.
Security-First Approach
We don’t just connect you; we protect you. Every connection we build is designed with Azure network security as the top priority.
Your Professional Partner
Our team maintains the highest level of expertise, applying lessons from Azure network certification to give you a network that is both modern and rock-solid.
Tools
Tools and Plugins for Frameworks

Azure Network Watcher
A diagnostic tool we use to “see” your network traffic and fix glitches instantly.

Azure Firewall
A managed plugin that adds a professional-grade shield to your entire virtual environment.

VNet Peering
A tool that allows us to link two separate Azure virtual networks together so they act as one.

Azure DNS
A service that manages your website addresses, ensuring they are always reachable and fast.
Here is what our Clients are saying About us

Petri Leinonen (Finland)
Our Azure network architecture had grown without any design, VNets with overlapping address spaces, peering connections that made no sense, and no clear segmentation between workloads. vorza360 redesigned our entire Azure network topology and the new architecture is clean, logical, and properly documented.
Nadia Al-Farsi (Oman)
vorza360 designed and implemented a hub-spoke Azure network topology for our organisation that centralises shared services while keeping workload VNets appropriately isolated. The ‘hub-and-spoke-by-design’ architecture they built gives us consistent connectivity with proper control over what can reach what.
Radu Popa (Romania)
We needed Azure Private Endpoints configured for all our PaaS services so database and storage traffic never traverses the public internet. vorza360 implemented Private Endpoints for every applicable service, updated DNS resolution correctly, and verified that public access was disabled. A significant improvement to our data security posture.
Arun Nair (India)
vorza360 set up Azure VPN Gateway and ExpressRoute coexistence for our hybrid connectivity so our on-premises network connects to Azure with both a resilient VPN path for failover and ExpressRoute for primary high-bandwidth connectivity. The ‘primary-plus-failover’ architecture they delivered meets both our performance and resilience requirements.
Tobias Andersen (Denmark)
vorza360 configured Azure Firewall as our central inspection point for all traffic between our Azure workloads and the internet. The ‘inspect-everything-leaving-Azure’ model they implemented replaced a patchwork of NSG rules that were increasingly difficult to manage and reason about.
Adaeze Eze (Nigeria)
vorza360 implemented Azure DDoS Protection Standard for our internet-facing Azure resources and configured the mitigation policies appropriately for our traffic profiles. The protection layer they put in place gave our security team confidence in our resilience against volumetric attacks that we simply didn’t have before.
More about Microsoft Azure
Azure Virtual Machines
Scale your business effortlessly with vorza360’s expert Azure virtual machine services.
Azure App Services
Launch and grow your web applications effortlessly with vorza360’s expert Azure app…
Azure Functions
Run your code without the hassle of managing servers with vorza360’s expert Azure…
Azure SQL Database
Secure and scale your business data with vorza360’s expert Azure SQL database services.
Azure Blob Storage
Simplify your data storage with vorza360’s expert Azure storage blob service.
Azure Active Directory
Secure your business with vorza360’s expert Microsoft Azure Active Directory service.
+ 5
More
Azure Kubernetes Service (AKS)
Simplify container management with vorza360’s expert Azure kubernetes services AKS.
Azure DevOps
Accelerate your software delivery with vorza360’s affordable Azure devops services.
Azure Logic Apps
Connect your apps and automate your business processes with vorza360’s expert Azure…
More about Microsoft Azure
Azure Virtual Machines
Azure App Services
Azure Functions
+ 12
More
Azure SQL Database
Azure Blob Storage
Azure Active Directory
Azure Kubernetes Service (AKS)
Azure DevOps
Frequently Asked Questions
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is Azure Virtual Network (VNet) and how does vorza360 design it for enterprise workloads?
Azure Virtual Network (VNet) is the fundamental networking building block in Azure, a logically isolated private network in the Azure cloud where you deploy Azure resources and control their network communication. A well-designed VNet architecture is essential for both security (isolating resources that should not be publicly accessible) and connectivity (enabling communication between Azure resources, on-premises systems, and the internet in a controlled manner). vorza360 designs Azure VNet architectures following Microsoft’s Cloud Adoption Framework and Azure Well-Architected Framework networking guidance: we implement a hub-and-spoke topology where a central hub VNet contains shared services (Azure Firewall, VPN/ExpressRoute gateways, Azure Bastion), and spoke VNets connect to it via VNet peering, each spoke containing a specific workload environment (production, staging, development). We design subnet segmentation within each spoke to isolate application tiers (web tier, application tier, data tier), applying Network Security Groups at each subnet boundary.
How does vorza360 connect on-premises networks to Microsoft Azure?
Connecting on-premises infrastructure to Azure is a fundamental requirement for hybrid cloud deployments, enabling Azure VMs to access on-premises databases, users to reach Azure-hosted applications from the office network, and active directory synchronization between on-premises and cloud identity systems. vorza360 implements hybrid connectivity through two primary approaches: Azure VPN Gateway creates an encrypted IPsec/IKE VPN tunnel over the public internet between the on-premises network and the Azure VNet, appropriate for moderate bandwidth requirements (up to 10 Gbps with VpnGw5) and variable usage patterns where the pay-per-hour gateway cost is acceptable. Azure ExpressRoute provides a dedicated private circuit connection between the on-premises network and Azure through a network service provider, avoiding the public internet entirely, providing guaranteed bandwidth (up to 100 Gbps), lower latency, and higher SLA than VPN, appropriate for latency-sensitive applications and large data transfer volumes. We design the connectivity solution based on bandwidth requirements, latency tolerance, cost, and compliance requirements.
How does vorza360 implement Azure Firewall for centralized network security?
Azure Firewall is a managed, cloud-native network security service that provides centralized network protection for all resources in an Azure VNet. Unlike Network Security Groups (which are stateful packet filters at the VNet level), Azure Firewall is a fully stateful firewall-as-a-service with built-in high availability, unrestricted scalability, and application-layer (Layer 7) filtering capabilities. vorza360 deploys Azure Firewall in the hub VNet of a hub-and-spoke architecture, routing all traffic from spoke VNets and on-premises networks through it using User Defined Routes (UDRs) configured on all subnets. We configure Azure Firewall policy rules: network rules (IP address and port-based filtering for non-HTTP/S traffic), application rules (FQDN-based filtering for HTTP/S and SQL traffic, allowing only specified domain names rather than IP ranges), IDPS (Intrusion Detection and Prevention System) signature-based threat detection, and DNS proxy configuration. We enable Azure Firewall diagnostics logging to Azure Monitor for comprehensive traffic auditing.
How does vorza360 configure Azure Load Balancer and Application Gateway for application delivery?
Azure provides two distinct load balancing services for different traffic types and requirements. Azure Load Balancer operates at Layer 4 (TCP/UDP), it distributes incoming connections across multiple backend VMs using hash-based distribution, providing high availability and scale for non-HTTP workloads (SQL Server clusters, RDP session hosts, custom application servers on non-standard ports). Azure Application Gateway operates at Layer 7 (HTTP/HTTPS), it provides URL-based routing, SSL termination, Web Application Firewall (WAF) capabilities, cookie-based session affinity, and connection multiplexing, appropriate for web application load balancing. vorza360 selects the appropriate service for each use case: Application Gateway with WAF for public-facing web applications (providing both load balancing and built-in OWASP protection), Azure Load Balancer for internal tier-to-tier communication and non-HTTP workloads. For global applications requiring traffic distribution across multiple Azure regions, we implement Azure Front Door which provides global load balancing with CDN, WAF, and intelligent routing.
How does vorza360 implement Azure Private Link for secure access to Azure PaaS services?
By default, Azure PaaS services (Azure SQL Database, Azure Blob Storage, Azure Key Vault, and others) are accessible over public endpoints, meaning traffic to these services traverses the Microsoft Azure backbone but technically originates from and terminates at public IP addresses. For organizations with strict security requirements or compliance mandates requiring all data to remain on private networks, Azure Private Link solves this by creating a private endpoint within your VNet, a private IP address in your VNet subnet that maps to the specific Azure PaaS resource. vorza360 implements Azure Private Link by deploying private endpoints for all PaaS services handling sensitive data, configuring Private DNS Zones that override the public DNS resolution for the service (so your VNet clients resolve the storage account name or SQL server name to the private endpoint IP rather than the public IP), disabling public network access on the PaaS resources (forcing all access through private endpoints only), and ensuring on-premises networks can reach the private endpoints via the ExpressRoute or VPN connection for hybrid scenarios.