Protect your business with vorza360’s managed security services. We provide secure user management and expert data protection to keep your systems safe and your team productive.
The Challenge: Peter’s company had a MySQL server accessible directly from the internet on the default port, with the root account using a weak password and several unused accounts left over from previous development work. A routine security scan flagged multiple critical findings before an attacker found them first.
The vorza360 Solution: vorza360 addressed every finding: bound MySQL to localhost removing internet exposure, enforced strong passwords and a password rotation policy, removed all anonymous users and unused accounts, restricted each application account to only the databases and permissions it required, and enabled the audit plugin to log privileged operations.
The Result: The follow-up security scan found no remaining critical findings on the database. Peter’s security team had a hardened MySQL installation with a documented security baseline they could maintain and demonstrate to their customers who were increasingly asking about their data security practices.
Yasmin Al-Hamdan (UAE)
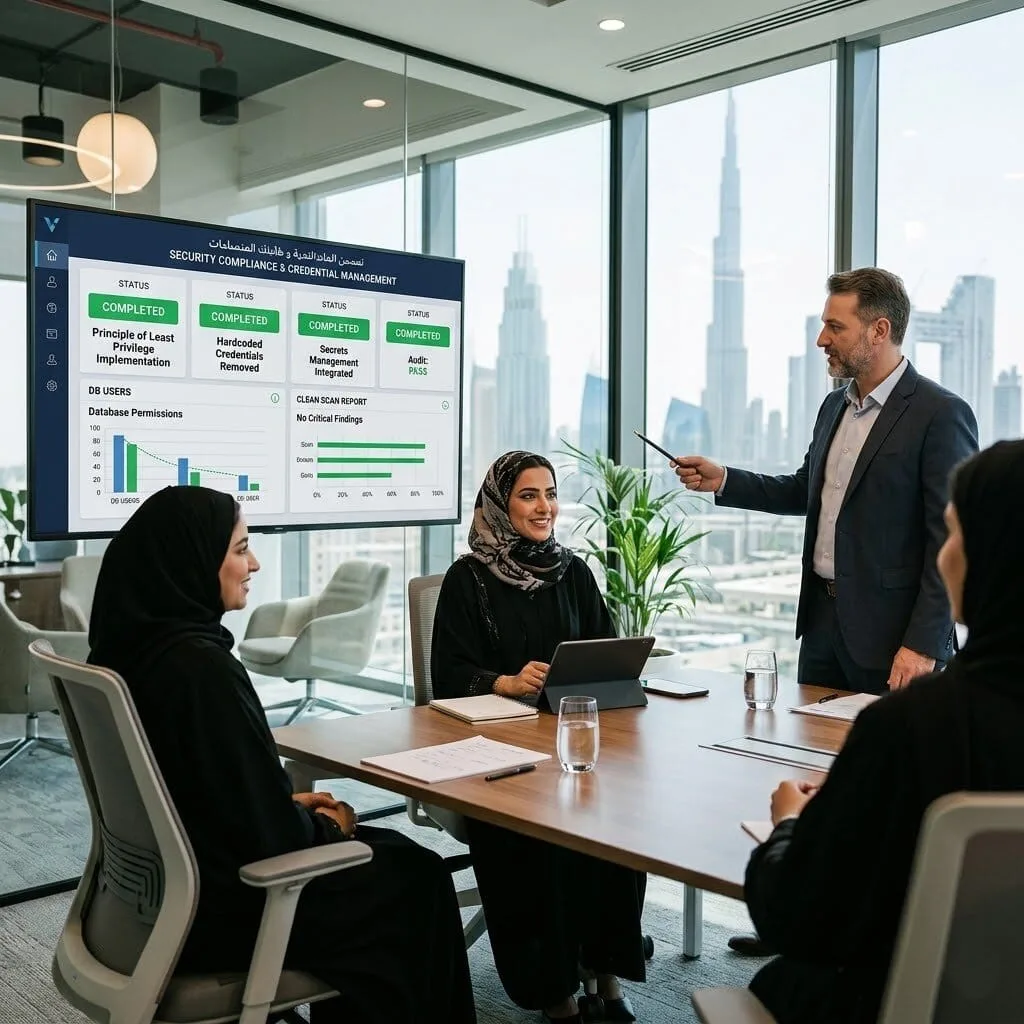
The Challenge: Yasmin’s company stored sensitive customer data in MySQL, but during a third-party security assessment, the assessor found that database credentials were hardcoded in plain text in multiple application configuration files, and the application accounts had far more database permissions than their operations actually required.
The vorza360 Solution: vorza360 created principle-of-least-privilege database accounts for each application, scoped to only the specific tables and operations each application genuinely needed. They worked with the development team to replace hardcoded credentials with environment variable-based configuration and vault-stored secrets, and audited all existing application accounts.
The Result: The over-privileged account problem was resolved, and credentials were removed from source code across all their repositories. Yasmin’s company passed their next security assessment with no credential-related findings, and the developer workflow for managing database credentials was documented to prevent regression.
Alexandru Marin (Romania)
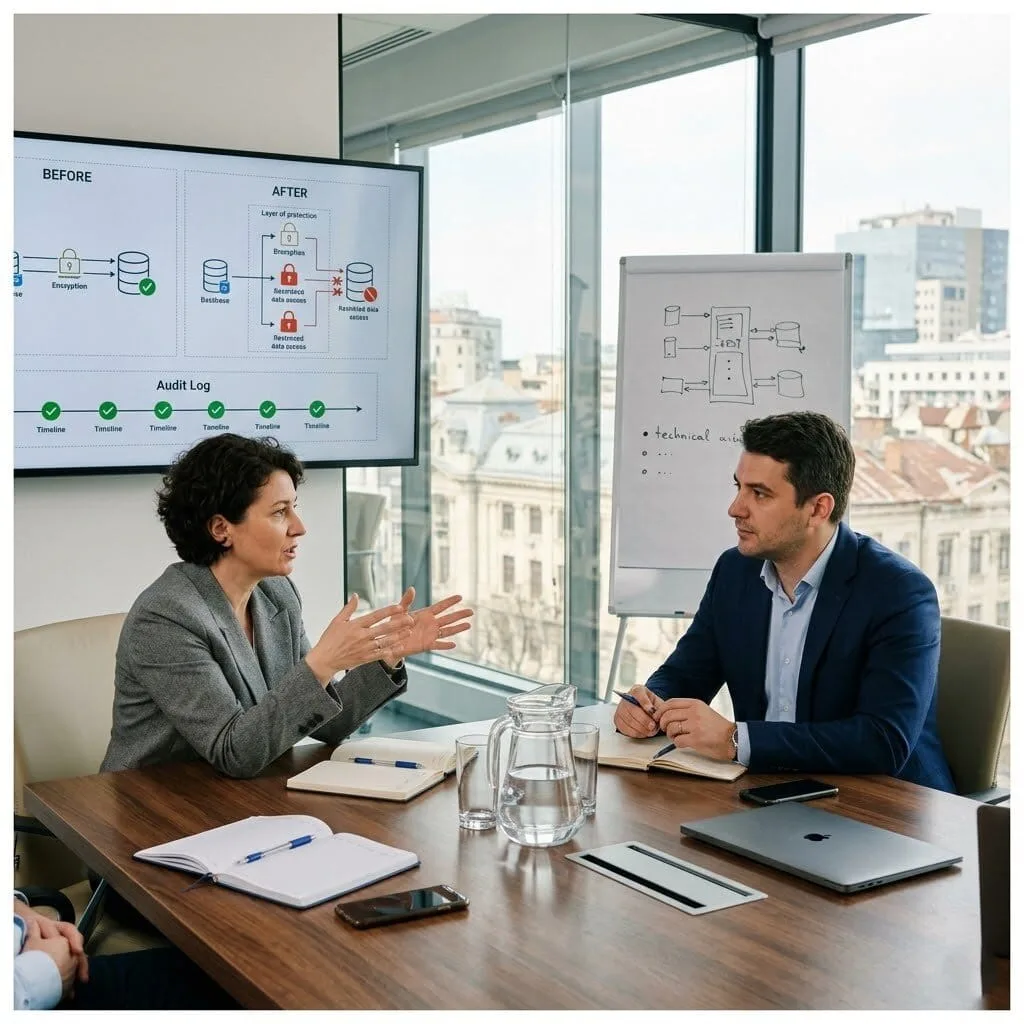
The Challenge: Alexandru’s company had suffered a SQL injection attack that had allowed an attacker to read data from their MySQL database through a vulnerable application. After cleaning up, they wanted to ensure that even if a future SQL injection occurred, the attacker would find the database as hard to exploit as possible.
The vorza360 Solution: vorza360 implemented defense-in-depth at the database layer: application accounts restricted to only the tables they legitimately accessed, stored procedures used for sensitive operations so application accounts didn’t need direct table access, connection encrypted via SSL, and the MySQL audit log enabled to detect unusual query patterns.
The Result: The database access layer was significantly hardened against exploitation. Alexandru’s security team had evidence of the controls in place, and the audit logging meant that any future attempt to probe the database through the application layer would be recorded and could trigger alerts.
Blessing Okafor (Nigeria)
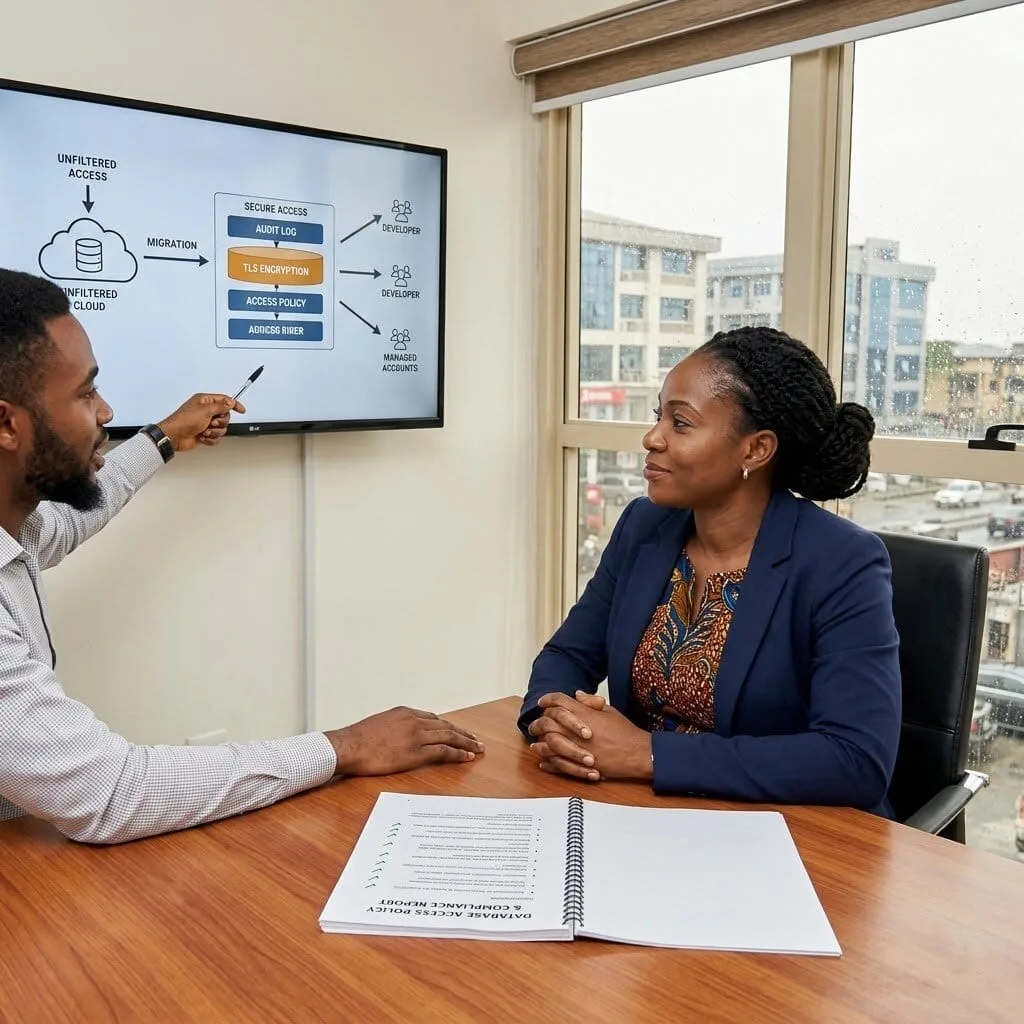
The Challenge: Blessing’s company had grown from a startup to a business with regulatory obligations, and their MySQL security had never kept pace. Multiple developers had root access, there was no audit log, database connections weren’t encrypted, and their compliance consultant had flagged it as a high-priority gap.
The vorza360 Solution: vorza360 removed root access from all developer accounts, created appropriately privileged service and administrative accounts, implemented TLS for all database connections, enabled the audit log plugin, and created a database access policy document that formally defined how access was managed, reviewed, and revoked.
The Result: Blessing’s company addressed the compliance gap within two weeks. The access policy document and audit log gave their compliance consultant the evidence they needed, and the removal of root access from developer accounts was welcomed by the developers themselves, who had never wanted that level of responsibility.
Rahul Verma (India)
The Challenge: Rahul’s company was preparing for PCI DSS compliance, which placed significant security requirements on their MySQL database storing card transaction data. Their current MySQL configuration met none of the PCI DSS technical requirements for database security.
The vorza360 Solution: vorza360 aligned the MySQL security configuration to PCI DSS requirements: encrypted connections for all clients, audit logging of all access to cardholder data tables, account management policies meeting PCI password requirements, network access restricted to only the application servers that required database access, and a documented database security policy.
The Result: The PCI DSS assessment passed the database controls section. Rahul’s company had a documented, evidence-backed MySQL security configuration that satisfied their assessor, and the controls were implemented in a way that the team could maintain and demonstrate at future assessments without recreating the work.
Johan Lindgren (Sweden)
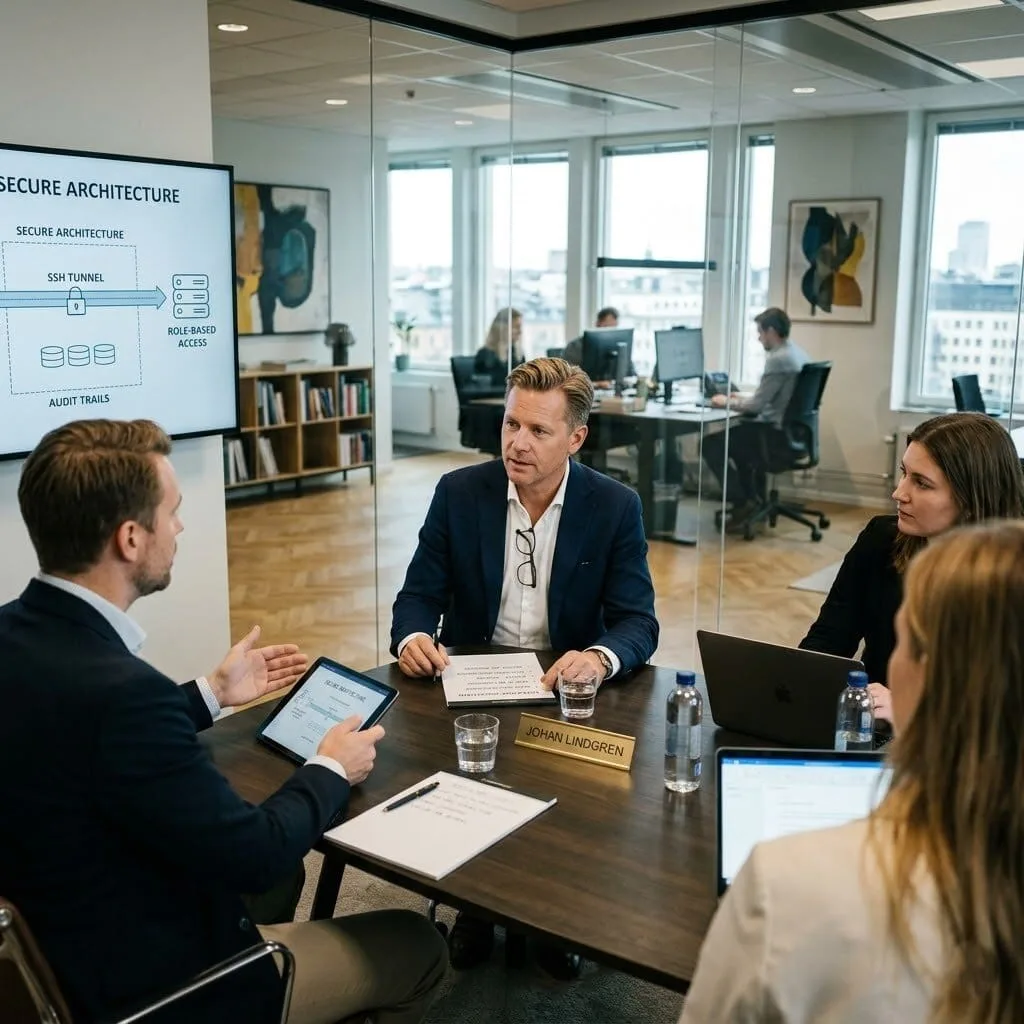
The Challenge: Johan’s company managed MySQL databases for several of their clients as part of their managed services offering. A security review of their own practices found that they were connecting to all client databases using a single shared administrative account with full privileges, a significant security and accountability problem.
The vorza360 Solution: vorza360 implemented a per-client, per-engineer account model with only the permissions each engineer needed for their specific role. They implemented SSH tunnelling for all remote database connections replacing direct MySQL port exposure, and set up audit logging so that every action taken on a client database was attributable to a specific engineer.
The Result: Johan’s managed services offering had the security model their enterprise clients had been asking for. The audit trails gave their clients confidence that access was controlled and accountable, and the SSH tunnel approach meant client databases no longer needed to be exposed to any network beyond localhost.
How we do it
We provide a hands-on service to turn complex safety rules into simple business wins.
Creative Approaches
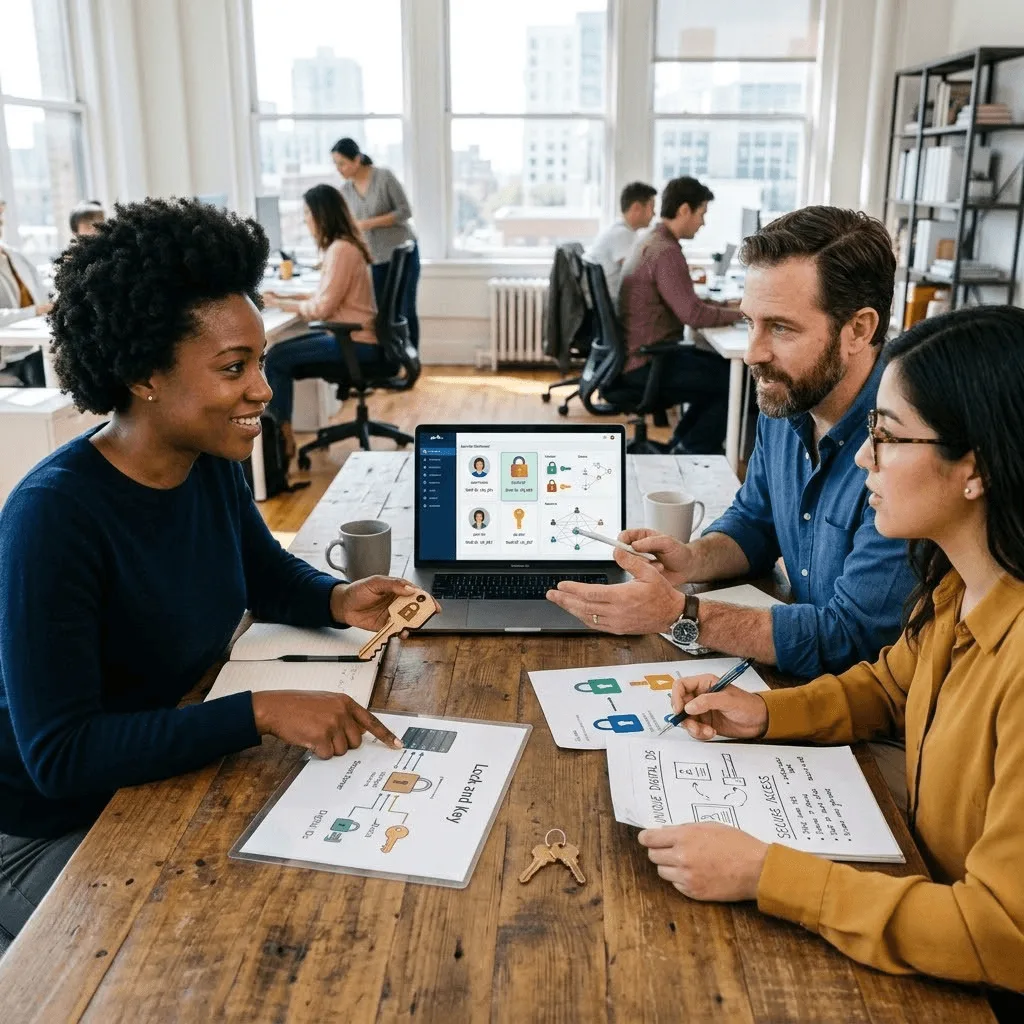
We use a “Lock and Key” method for user security management. Instead of just setting one password, we create unique digital IDs for every staff member, ensuring that only the right people can open your business’s digital doors.
Insightful Strategies
Our strategy centers on “Least Privilege” access. We provide an insightful review of your user management services to ensure employees only see the specific files they need for their daily work, keeping your core data private and protected.
Tailored Solutions
Every business has different risks, so we build a custom security management plan for you. We pick the specific secure database management platforms and tools that fit your budget while offering the strongest shield against hackers.
Creative Approaches
We use a “Lock and Key” method for user security management. Instead of just setting one password, we create unique digital IDs for every staff member, ensuring that only the right people can open your business’s digital doors.
Insightful Strategies
Our strategy centers on “Least Privilege” access. We provide an insightful review of your user management services to ensure employees only see the specific files they need for their daily work, keeping your core data private and protected.
Tailored Solutions
Every business has different risks, so we build a custom security management plan for you. We pick the specific secure database management platforms and tools that fit your budget while offering the strongest shield against hackers.
Tools
Tools vorza360 Offers for This Service
OpenVPN
A world-class tool for creating a secure “private tunnel” so your team can work safely from anywhere.
Keycloak
A powerful plugin for secure user management that lets your staff log into all their apps with one safe ID.
Fail2Ban
A smart security tool that automatically blocks hackers who try to guess your passwords.
Wazuh
A professional platform for security information and management that monitors your servers 24/7 for suspicious activity.
Multiple Platform Support
As a managed security services provider, we ensure your protection works everywhere your team does.
Linux Servers
We manage your user access management to keep your server’s “master” accounts locked and safe.
Windows Office
We set up user security management for your local PCs to prevent unauthorized logins.
AWS Cloud
We build secure “neighborhoods” in Amazon’s cloud to protect your high-speed web apps.
Microsoft Azure
Our team integrates your security with Azure’s business tools for a seamless experience.
Google Cloud
We use Google’s global network to provide data security management for your remote files.
Hybrid Systems
We create a bridge so your office and your cloud tools follow the same strict safety rules.
Linux Servers
We manage your user access management to keep your server’s “master” accounts locked and safe.
Windows Office
We set up user security management for your local PCs to prevent unauthorized logins.
AWS Cloud
We build secure “neighborhoods” in Amazon’s cloud to protect your high-speed web apps.
Microsoft Azure
Our team integrates your security with Azure’s business tools for a seamless experience.
Google Cloud
We use Google’s global network to provide data security management for your remote files.
Hybrid Systems
We create a bridge so your office and your cloud tools follow the same strict safety rules.
Multiple Framework Support
Node.js
Secure login systems for modern, real-time web applications and tools.
Python (Django)
Built-in data security management to protect your customer information.
PHP (Laravel)
Reliable user permissions that keep your business website organized and safe.
Java
Enterprise-grade security for large-scale corporate apps and banking tools.
React/Angular
Safe “front-end” designs that ensure users only see what they are allowed to.
WordPress
Specialized security hardening to protect your site from common online attacks.
SQL Databases
Encryption and secure user management for your most sensitive records.
Docker
Secure “containers” that keep your different apps isolated from each other.
Custom Headless Development
We are an eCommerce website design company, that uses the best creative skills to meet your business needs and ensure customer satisfaction. We’re with you every step of the way, from the beginning of your project to its completion.
Fashion & Apparel
Food & Grocery
Retail
FMCG
Real Estate
Construction
Hotel
Healthcare
Telecom
Fintech
Manufacturing
Automotive
Our Service Cycle
vorza360 follows a professional path to deliver top-tier managed IT security services.
Step 1
Security Audit
Step 2
Access Planning
Step 3
Tool Deployment
Step 4
User Onboarding
Step 5
Active Monitoring
Step 6
Continuous Support
Step 1
Security Audit
We find the weak spots in your current setup and identify who has access to your data.
Step 2
Access Planning
Our experts design a custom user access management map for your entire team.
Step 3
Tool Deployment
We install the best secure database management platforms and monitoring tools.
Step 4
User Onboarding
We help your staff set up their new, secure IDs and show them how to log in safely.
Step 5
Active Monitoring
Our team watches your security information and management logs 24/7 for any threats.
Step 6
Continuous Support
vorza360 stays by your side, updating your security rules as your business grows.
Here is what our Clients are saying About us
Hanna Lehtinen (Finland)
Our MySQL security was essentially non-existent, root access shared across teams, no audit logging, anonymous users still enabled. vorza360 locked everything down, implemented role-based access, and set up proper audit trails. A complete security overhaul that was long overdue.
Saad Al-Qahtani (Saudi Arabia)
vorza360 conducted a full MySQL security review ahead of our compliance audit and found several critical misconfigurations that had been there since installation. They fixed every issue, implemented least-privilege access for all users, and gave us documentation that satisfied our auditors completely.
Teodora Vasile (Romania)
We needed to implement strict data access controls in MySQL to meet GDPR requirements for our European customers. vorza360 designed and implemented a user permission structure that ensures each application component only accesses exactly the data it needs. Our DPO signed off without any concerns.
Oluwatobi Adeniyi (Nigeria)
vorza360 found that several of our MySQL user accounts had wildcard host permissions and excessive privileges that had accumulated over years. They cleaned everything up, implemented proper IP-based restrictions, and put a user provisioning procedure in place so it doesn’t drift again.
Per Lindgren (Sweden)
After a developer accidentally ran a destructive query against production using elevated credentials, we brought in vorza360 to fix our MySQL access model. They restructured permissions so developers work with read-only access by default and production writes require explicit authorisation. No more accidental disasters.
Zanele Mokoena (South Africa)
vorza360 implemented MySQL Enterprise Audit-equivalent logging using open source tooling that gave us full visibility into who accessed what data and when. The ‘complete-audit-trail’ they set up has been essential for our internal compliance reporting and has already flagged one suspicious access pattern.
More about MySQL
MySQL Installation & Configuration
Get your database started the right way with vorza360’s professional MySQL installation…
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
How does vorza360 implement MySQL user management following the principle of least privilege?
The principle of least privilege means every MySQL user account has only the specific permissions it needs to perform its function, nothing more. vorza360 implements this systematically: application database users receive only the SELECT, INSERT, UPDATE, and DELETE privileges on the specific databases and tables their application accesses, not blanket privileges on all databases. Read-only reporting users receive only SELECT access. Backup users receive only the privileges needed to execute mysqldump or XtraBackup (SELECT, RELOAD, LOCK TABLES, REPLICATION CLIENT). Replication users receive only REPLICATION SLAVE. Administrative accounts used for maintenance receive broader privileges but are protected with two-factor authentication and restricted host access. We audit the complete list of MySQL user accounts and their privileges as part of every security review, removing accounts that are no longer needed and tightening those with excessive permissions.
How does vorza360 encrypt MySQL data in transit and at rest?
Encrypting MySQL data in transit prevents network interception of sensitive database communications, particularly important in cloud environments, shared hosting, or any architecture where the application and database are on different servers. vorza360 configures MySQL to require TLS/SSL for all connections from application servers, configuring the server certificate, CA certificate, and optionally client certificates for mutual TLS authentication. We set require_secure_transport=ON to reject unencrypted connections entirely. For data at rest, we implement InnoDB Tablespace Encryption for tables containing sensitive data (healthcare records, financial data, personally identifiable information), using MySQL’s keyring plugin to manage the encryption keys. For cloud-managed MySQL (RDS, Azure Database for MySQL), we enable storage encryption at the instance level. We also implement transparent data encryption where supported for the operating system’s file system layer.
How does vorza360 protect MySQL from SQL injection attacks?
SQL injection attacks exploit applications that construct SQL queries by concatenating user-supplied input directly into query strings, allowing attackers to manipulate the query structure and execute unauthorized database commands. While SQL injection is primarily an application-layer vulnerability, vorza360 implements database-level defenses that limit its impact. We configure application database users with minimum necessary privileges so that even a successful injection can only access the data that user is authorized for. We implement stored procedures with EXECUTE-only privileges for sensitive operations, eliminating direct table access entirely. We enable MySQL’s audit log plugin to capture and alert on unusual query patterns that might indicate injection attempts. We review application code and queries for parameterization compliance, ensuring all variable data is passed as bound parameters rather than concatenated strings. We work with development teams to audit and remediate any injection vulnerabilities found during database security reviews.
How does vorza360 implement MySQL audit logging for compliance requirements?
MySQL audit logging records a complete history of database activity, who connected, what queries were executed, which tables were accessed, and whether operations succeeded or failed, providing the evidence trail required by compliance frameworks such as HIPAA, PCI-DSS, SOX, and GDPR. vorza360 implements audit logging using MySQL Enterprise Audit (for Enterprise Edition) or the open-source MariaDB Audit Plugin or Percona Audit Log Plugin for Community Edition. We configure the audit plugin to capture privileged account usage, DDL statements (CREATE, ALTER, DROP), and access to specifically sensitive tables rather than logging every query (which would produce unmanageable log volumes and performance overhead). We ensure audit logs are written to a location that the database user cannot modify, rotated and archived to long-term storage, and reviewed periodically for anomalous patterns. We provide compliance documentation describing the audit implementation for regulatory assessments.
How does vorza360 respond to a suspected MySQL security incident?
When a MySQL security incident is suspected, unauthorized access, unusual query patterns, data exfiltration indicators, or unfamiliar user accounts, vorza360 follows an incident response process focused on containment, investigation, and remediation. We immediately isolate the affected server from unnecessary network access to contain the incident while preserving the ability to investigate. We preserve evidence by capturing current process lists, open connections, recent audit log entries, and slow query log contents before anything is changed. We audit all MySQL user accounts for unauthorized accounts or privilege escalations. We review recent binary log entries for unauthorized data access or modification. We identify and close the attack vector, whether through a compromised application credential, a network exposure, or a MySQL vulnerability. We assess what data was accessed or modified. We implement additional controls to prevent recurrence and prepare an incident report documenting the timeline, impact, and remediation steps taken.