Secure your business with vorza360’s expert Microsoft Azure Active Directory service. We manage your identities and access, ensuring your team can work safely from anywhere with ease.
The Challenge: Stefan’s company was adopting Azure AD (Entra ID) as their primary identity platform but their on-premises Active Directory had years of accumulated clutter, disabled accounts still syncing, stale groups, and attributes that were inconsistent. Synchronising the mess to Azure AD would bring the problems to the cloud rather than leaving them on-premises.
The vorza360 Solution: vorza360 performed an on-premises AD cleanup before enabling Azure AD Connect: removed accounts that had been disabled for over 90 days, corrected inconsistent attributes that would cause sync errors, and scoped the Azure AD Connect sync to only the OUs and attributes that genuinely needed to be in Azure AD.
The Result: Azure AD Connect sync started cleanly with no errors and a clean set of identities in Azure AD. Stefan’s team had a much healthier on-premises AD as a secondary benefit of the cleanup, and the scoped sync meant Azure AD reflected their current organisation rather than years of accumulated history.
Aisha Al-Zahrani (Saudi Arabia)
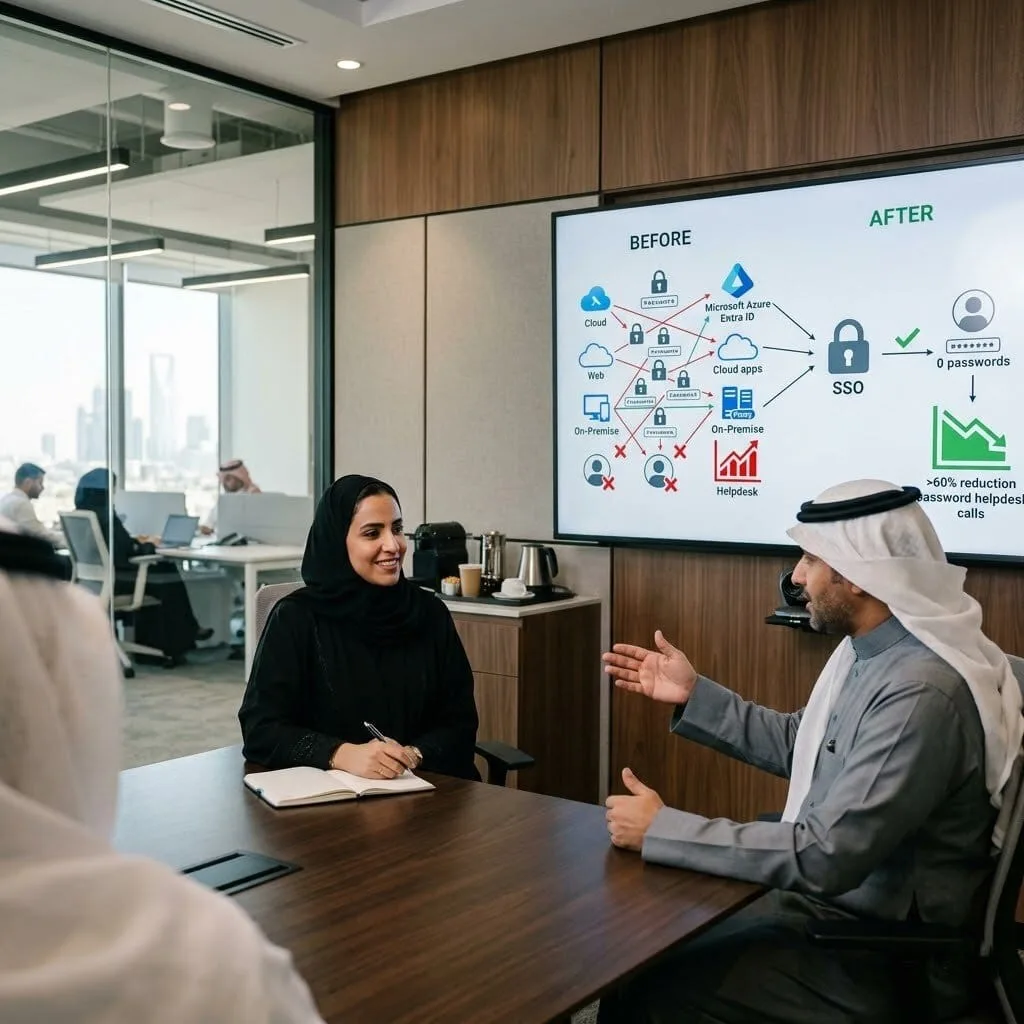
The Challenge: Aisha’s company had Entra ID with SSO configured for some applications but others still required separate passwords. Users were managing multiple credentials for different systems, password reset calls were high, and the inconsistent SSO coverage was a source of constant friction.
The vorza360 Solution: vorza360 extended SSO coverage to all remaining applications: SAML and OIDC integration for the applications that supported it, and Entra Application Proxy for the on-premises web applications that couldn’t be moved to cloud authentication directly. Self-service password reset was also enabled and communicated to users.
The Result: Users had single sign-on for all their applications, cloud and on-premises, for the first time. Password reset helpdesk calls dropped by over 60% as self-service reset handled the majority of requests. Aisha’s users stopped managing multiple credentials and the friction that had been generating helpdesk tickets became a solved problem.
Ciprian Marin (Romania)
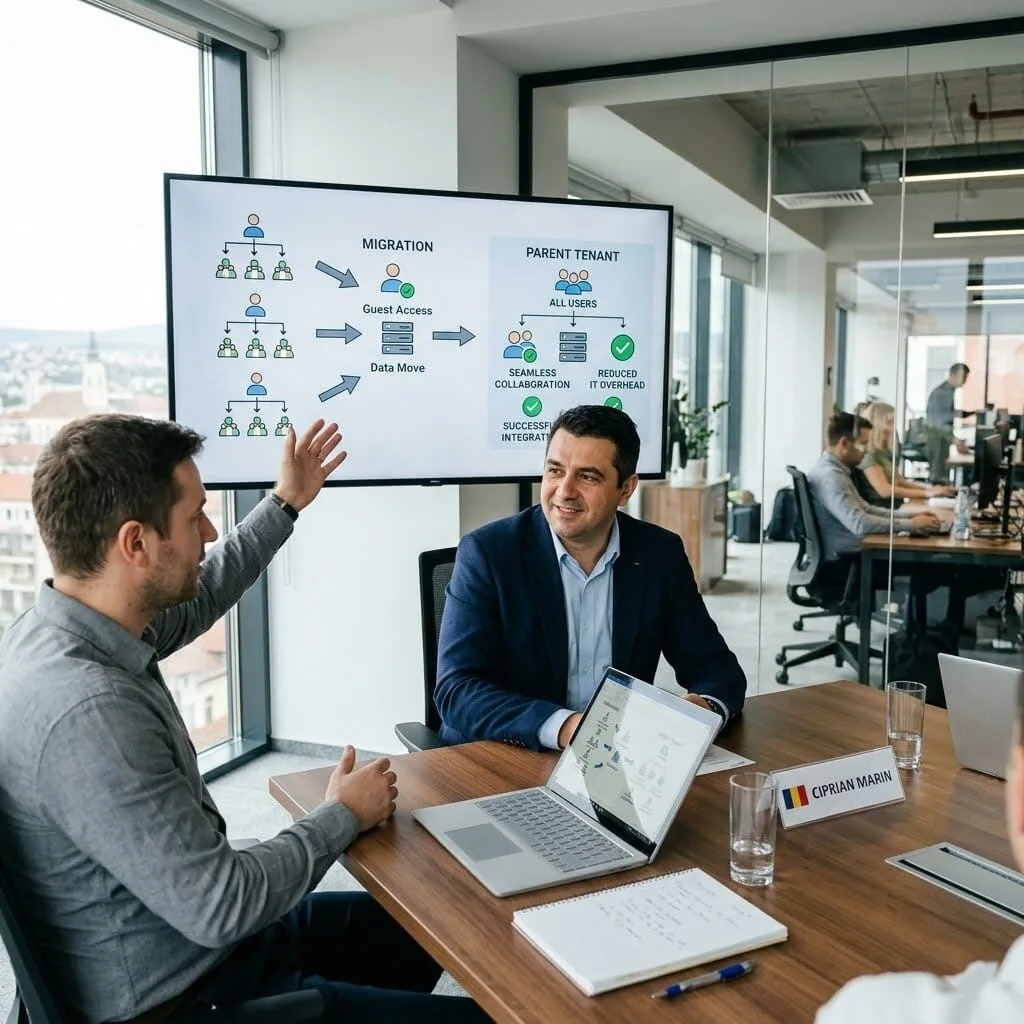
The Challenge: Ciprian’s company had multiple Azure AD tenants from acquisitions that needed to be consolidated. Users in the acquired companies had separate identities, couldn’t collaborate easily with the parent company, and managing multiple tenants was creating administrative overhead the IT team didn’t have capacity for.
The vorza360 Solution: vorza360 planned and executed the tenant consolidation: guest user access established as an interim measure for immediate collaboration, user accounts migrated from acquired tenant to parent tenant preserving group memberships and application assignments, and the acquired tenant decommissioned after all users were migrated and all applications were working correctly.
The Result: All users operated from a single Azure AD tenant after the consolidation. Collaboration between previously separate organisations became seamless, IT management overhead reduced to managing one tenant rather than three, and the acquisition integration that had been an IT obstacle was resolved.
Priya Nair (India)
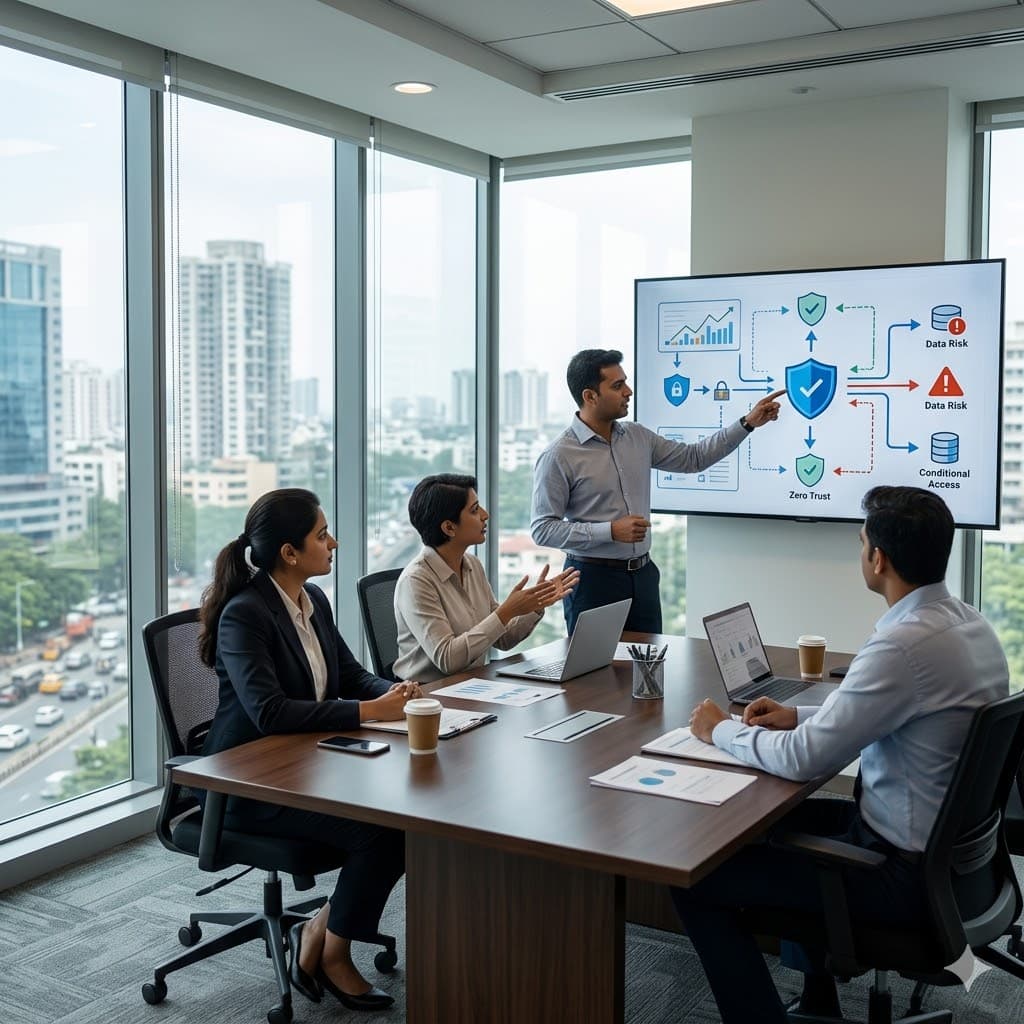
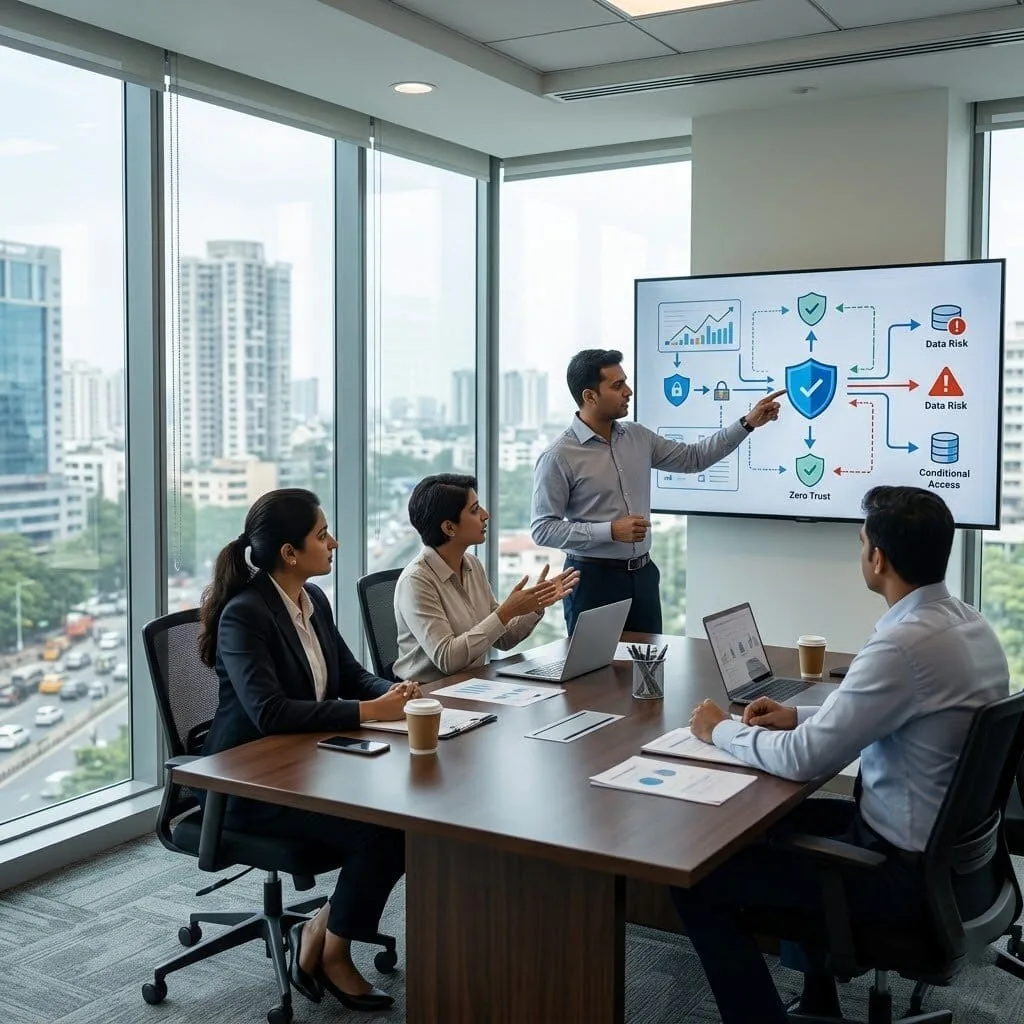
The Challenge: Priya’s company was implementing Zero Trust and needed their Entra ID Conditional Access to enforce risk-based access controls, requiring step-up authentication when sign-in risk was elevated and blocking access from anonymising proxies. Their existing Conditional Access policies were simple location-based rules that didn’t address identity risk.
The vorza360 Solution: vorza360 implemented risk-based Conditional Access policies using Entra ID Protection: sign-in risk policies requiring MFA when sign-in risk was medium or above, user risk policies requiring password change when user risk was elevated, and named location policies for trusted networks with appropriate reduction in MFA friction for low-risk scenarios.
The Result: Priya’s Conditional Access went from static location-based rules to dynamic, risk-based access control. The policies blocked several high-risk sign-in attempts in the first month that the old policies would have allowed through. Legitimate users experienced less friction on their normal sign-ins because the risk-based approach allowed trusted patterns without always requiring MFA.
Mikael Bergström (Sweden)
The Challenge: Mikael’s company was managing Azure AD application registrations manually, hundreds of app registrations with varying permission scopes, secret expiry dates that were tracked in a spreadsheet, and no review process for applications that were no longer in use.
The vorza360 Solution: vorza360 audited all application registrations, identified and deleted registrations with no sign-in activity in over 90 days, implemented secret expiry alerting via Azure Monitor so upcoming expirations triggered notifications to the owning team, and established a quarterly app registration review process.
The Result: The application registration estate was rationalised from several hundred to the subset actually in use. Mikael’s team stopped discovering expired secrets at the worst possible moment, when an application failed because its secret had silently expired, and the quarterly review process meant the estate would stay clean rather than accumulating again.
Yewande Olatunji (Nigeria)
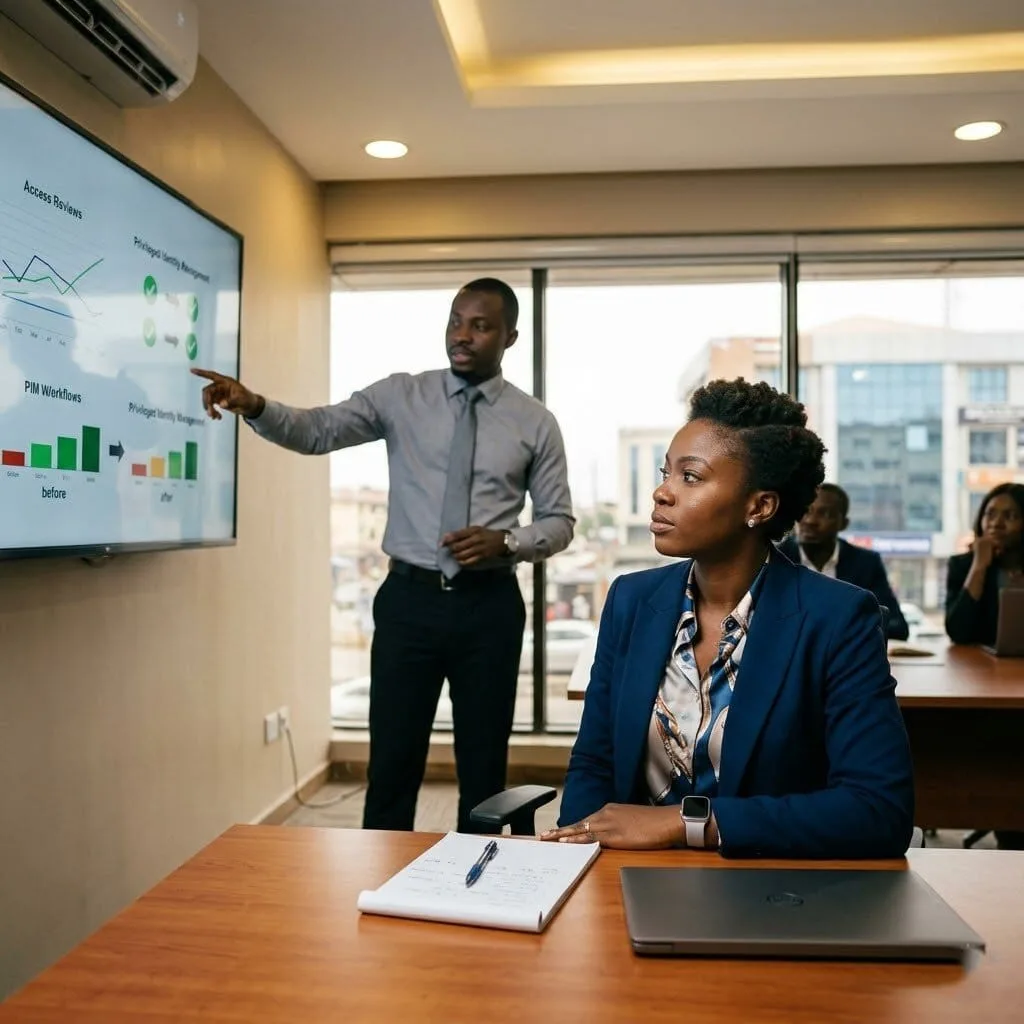
The Challenge: Yewande’s company was preparing for external auditors who would be reviewing their identity governance practices. Their Entra ID had no access reviews configured, privileged roles were permanently assigned rather than using PIM (Privileged Identity Management), and there was no evidence of periodic access certification.
The vorza360 Solution: vorza360 implemented Entra ID Governance access reviews for all privileged roles and high-sensitivity group memberships, configured PIM for all Azure and Entra ID privileged roles converting permanent assignments to eligible assignments requiring just-in-time activation, and established a quarterly access certification cycle.
The Result: The auditors reviewed the identity governance configuration and found it met their requirements. Yewande’s company had PIM protecting all privileged roles, eliminating standing privileged access, and the access review evidence gave auditors the certification documentation they were looking for. The controls implemented for the audit were genuine improvements, not just audit theatre.
vorza360’s Tech Edge
Identity & Access Management
Conditional Access Policies
Single Sign-On (SSO)
+ 2
More
Multi-Factor Authentication (MFA)
Azure AD B2B & B2C
vorza360’s Tech Edge
Identity & Access Management
Whether you have a team of 2 or 200, our shared team inboxes keep everyone on the same page and in the loop.
Conditional Access Policies
Our team sets up “smart rules” that check a user’s location and device before letting them in, adding an invisible layer of protection.
Single Sign-On (SSO)
We simplify your day by letting you log in just once to access all your Azure active directory application tools without remembering dozens of passwords.
Multi-Factor Authentication (MFA)
We add a quick extra step (like a code on your phone) to prove it’s really you, making it nearly impossible for hackers to get in.
Azure AD B2B & B2C
We help you safely share your apps with partners or customers without giving away the keys to your entire kingdom.
Unified Login Management
We bring all your apps under one roof so your team only needs one username and password.
Advantages
Setup of Microsoft Azure active directory service for all employees.
One-click access to email, files, and HR tools.
Reduced "password fatigue" for your staff.
Centralized control for your IT security.
Faster onboarding for new team members.
Modern Security Guarding
We use smart technology to watch your digital front door and block suspicious activity instantly.
Advantages
Real-time monitoring of every login attempt.
Blocking of access from high-risk locations.
Automated alerts for unusual account behavior.
Security "scores" to help improve your safety.
Reliable active directory Microsoft Azure service protection.
External Partner Collaboration
We make it easy to work with people outside your company without compromising your internal security.
Advantages
Secure guest access for contractors and vendors.
Control over exactly what files outsiders can see.
Easy "offboarding" when a project is finished.
Professional login screens for your customers.
Safe and simple Azure active directory services for partners.
Password-Free Future
vorza360 helps you move away from risky passwords by using modern tech like fingerprints or face ID.
Advantages
Setup of "Passwordless" login options.
Use of the Microsoft Authenticator app for easy entry.
Drastic reduction in "forgotten password" support calls.
Higher security than traditional typed passwords.
Improved Azure active directory services user experience.
Automated Group Management
We organize your team into digital groups so permissions are always updated automatically when roles change.
Advantages
Automatic access based on job title or department.
Self-service options for joining project teams.
Clean and organized user lists.
Compliance-ready reporting for audits.
Simplified management with the Azure active directory module.
Unified Login Management
We bring all your apps under one roof so your team only needs one username and password.
ADVANTAGES
Setup of Microsoft Azure active directory service for all employees.
One-click access to email, files, and HR tools.
Reduced "password fatigue" for your staff.
Faster onboarding for new team members.
Centralized control for your IT security.
Modern Security Guarding
We use smart technology to watch your digital front door and block suspicious activity instantly.
ADVANTAGES
Real-time monitoring of every login attempt.
Blocking of access from high-risk locations.
Automated alerts for unusual account behavior.
Security "scores" to help improve your safety.
Reliable active directory Microsoft Azure service protection.
External Partner Collaboration
We make it easy to work with people outside your company without compromising your internal security.
ADVANTAGES
Secure guest access for contractors and vendors.
Control over exactly what files outsiders can see.
Easy "offboarding" when a project is finished.
Professional login screens for your customers.
Safe and simple Azure active directory services for partners.
Password-Free Future
vorza360 helps you move away from risky passwords by using modern tech like fingerprints or face ID.
ADVANTAGES
Setup of "Passwordless" login options.
Use of the Microsoft Authenticator app for easy entry.
Drastic reduction in "forgotten password" support calls.
Higher security than traditional typed passwords.
Improved Azure active directory services user experience.
Automated Group Management
We organize your team into digital groups so permissions are always updated automatically when roles change.
ADVANTAGES
Automatic access based on job title or department.
Self-service options for joining project teams.
Clean and organized user lists.
Compliance-ready reporting for audits.
Simplified management with the Azure active directory module.
Why Choose vorza360 for This Service?
We provide a secure and stress-free identity solution that protects your business from intruders while making it easy for your team to log in and stay productive.
We Simplify Security
Identity management can be complex, but we handle the setup and the “rules” so you just enjoy a safe login experience.
Cost-Efficient Planning
We help you understand Azure active directory pricing to ensure you get the security features you need at a fair Azure active directory cost.
Ongoing Support
vorza360 doesn’t just “set it and forget it.” We constantly adjust your security policies to keep up with new online threats.
Tools
Tools and Plugins for Frameworks
Azure AD Connect
A tool we use to sync your office’s old login system with the new cloud system.
Microsoft Authenticator
The plugin that allows your phone to act as your secure digital key.
App Registrations
A tool our team uses to link your custom business apps to your secure login.
Identity Governance
A framework we use to ensure only the right people have access to sensitive data over time.
Here is what our Clients are saying About us
Hannu Korhonen (Finland)
Our Azure AD had been set up without much thought for security, no MFA enforced, no Conditional Access policies, guest accounts accumulating without review. vorza360 implemented a proper identity governance framework that addressed every gap. Our identity security posture improved fundamentally in a single engagement.
Rasha Al-Zahrawi (Kuwait)
vorza360 configured Azure AD Conditional Access policies for our organisation that enforce MFA based on user risk, device compliance, and location context. The ‘risk-appropriate authentication’ model they built is significantly more secure than our previous blanket MFA approach and generates far fewer user complaints.
Cristina Moldovan (Romania)
vorza360 implemented Azure AD B2C for our customer-facing application so external users have a proper identity experience, self-service registration, social login options, and branded authentication pages, without us having to build any of that ourselves. A professional identity solution delivered quickly.
Suresh Iyer (India)
vorza360 set up Azure AD Privileged Identity Management for our administrative accounts so elevated access is time-limited and requires justification rather than permanently assigned. The ‘just-in-time privilege’ model they implemented has satisfied our security audit requirements and reduced our standing privileged access significantly.
Sofie Andersen (Denmark)
Our hybrid identity setup between on-premises Active Directory and Azure AD had several sync issues causing inconsistent user experiences. vorza360 audited the Azure AD Connect configuration, resolved the sync errors, and implemented proper filtering so only the right objects sync to the cloud. Clean and consistent now.
Adeola Adeyemi (Nigeria)
vorza360 configured Azure AD access reviews for our guest user accounts and privileged role assignments so we have a formal quarterly process to validate that access is still appropriate. Guest accounts and admin assignments that had accumulated for years were reviewed and the unnecessary ones removed in the first cycle.
More about Microsoft Azure
Azure Virtual Machines
Scale your business effortlessly with vorza360’s expert Azure virtual machine services.
Got questions? We’ve got answers. Find everything you need to know about using our platform, plans, and features
What is Azure Active Directory (Azure AD) and how does it differ from on-premises Active Directory?
Azure Active Directory (now called Microsoft Entra ID) is Microsoft’s cloud-based identity and access management service. While on-premises Active Directory Domain Services (AD DS) manages identities for Windows domain-joined computers and provides Kerberos and LDAP authentication within a corporate network, Azure AD is built for the modern cloud and internet-based authentication. Azure AD manages user identities for cloud applications (Microsoft 365, Salesforce, ServiceNow, thousands of SaaS applications), provides single sign-on across all integrated applications, enables multi-factor authentication, supports Conditional Access policies that evaluate risk before granting access, integrates with mobile device management, and provides B2B (partner) and B2C (customer) identity capabilities. vorza360 configures Azure AD as the central identity platform for organizations, whether they are cloud-only, hybrid (syncing with on-premises AD), or migrating from on-premises infrastructure entirely.
How does vorza360 configure Azure AD Conditional Access to protect business data?
Azure AD Conditional Access is a powerful security capability that evaluates signals about a login attempt, who is the user, what device are they using, what location are they connecting from, what application are they trying to access, and applies policies that determine whether to grant access, require MFA, or block the attempt entirely. vorza360 configures Conditional Access policies that implement Microsoft’s recommended security baselines and your specific requirements: we require MFA for all users accessing any cloud application, enforcing it from any device and location to eliminate password-only authentication. We configure policies that block access from countries where your organization has no legitimate users. We implement device compliance requirements through Microsoft Intune integration, requiring that managed and compliant devices are used for access to sensitive applications. We configure risk-based policies using Azure AD Identity Protection that automatically require step-up authentication or block access when a login shows signals of compromise (impossible travel, credential leaked on dark web).
How does vorza360 implement Azure AD Single Sign-On (SSO) for business applications?
Azure AD Single Sign-On allows employees to authenticate once with their corporate identity and then access all their work applications, Microsoft 365, Salesforce, GitHub, Slack, HR systems, and thousands of other SaaS applications, without being prompted to log in again for each one. vorza360 implements Azure AD SSO by registering each application in the Azure AD Enterprise Applications gallery (most major SaaS applications are pre-integrated with one-click setup) or configuring custom SAML 2.0 or OpenID Connect integrations for applications not in the gallery. We configure the application’s attribute mappings, ensuring that user properties like department, job title, and group memberships are sent as claims to the application so it can make authorization decisions. We test SSO functionality across all integrated applications and configure automated user provisioning (SCIM) where supported, so users are automatically created, updated, and deprovisioned in connected applications when their Azure AD account changes.
How does vorza360 configure Azure AD for hybrid identity when an organization has both on-premises and cloud resources?
Most organizations with existing on-premises Active Directory want employees to use the same username and password for both on-premises systems and cloud services, Azure AD Connect enables this by synchronizing identities from on-premises AD to Azure AD. vorza360 configures hybrid Azure AD identity by deploying Azure AD Connect on a domain-joined server, configuring the synchronization scope (which OUs and attributes to sync), selecting the appropriate sign-in method, Password Hash Synchronization (simplest, most resilient), Pass-Through Authentication (passwords validated against on-premises AD without storing hashes in cloud), or Federation with AD FS. We configure Seamless SSO which allows domain-joined Windows devices on the corporate network to access cloud applications without any sign-in prompts. We implement Azure AD Connect Health for monitoring synchronization health. For organizations wanting to extend Azure AD authentication to on-premises legacy applications, we deploy Azure AD Application Proxy as a secure, cloud-delivered reverse proxy.
How does vorza360 implement Privileged Identity Management (PIM) in Azure AD?
Azure AD Privileged Identity Management (PIM) is a service that manages, controls, and monitors access to important resources, preventing users from having permanent, always-active administrative roles that increase the risk of credential compromise causing widespread damage. vorza360 implements Azure AD PIM by converting permanent administrative role assignments (Global Administrator, User Administrator, Security Administrator) to eligible assignments, users are eligible for the role but must explicitly activate it when needed, providing justification and triggering MFA at the point of activation. Role activations are time-limited (typically 1 to 8 hours) and automatically expire. PIM generates approval workflows for the highest-privilege roles (Global Administrator requiring peer approval before activation). PIM provides access reviews, periodic campaigns that ask reviewers to confirm whether specific users still need their eligible role assignments, automatically removing access for uncertified assignments. This significantly reduces the window of opportunity for attackers who compromise an administrative account.